





DATASHEET
KELA Technical Intelligence
Automated detection of compromised IPs and domains involved in cybercrime activity.
Share:
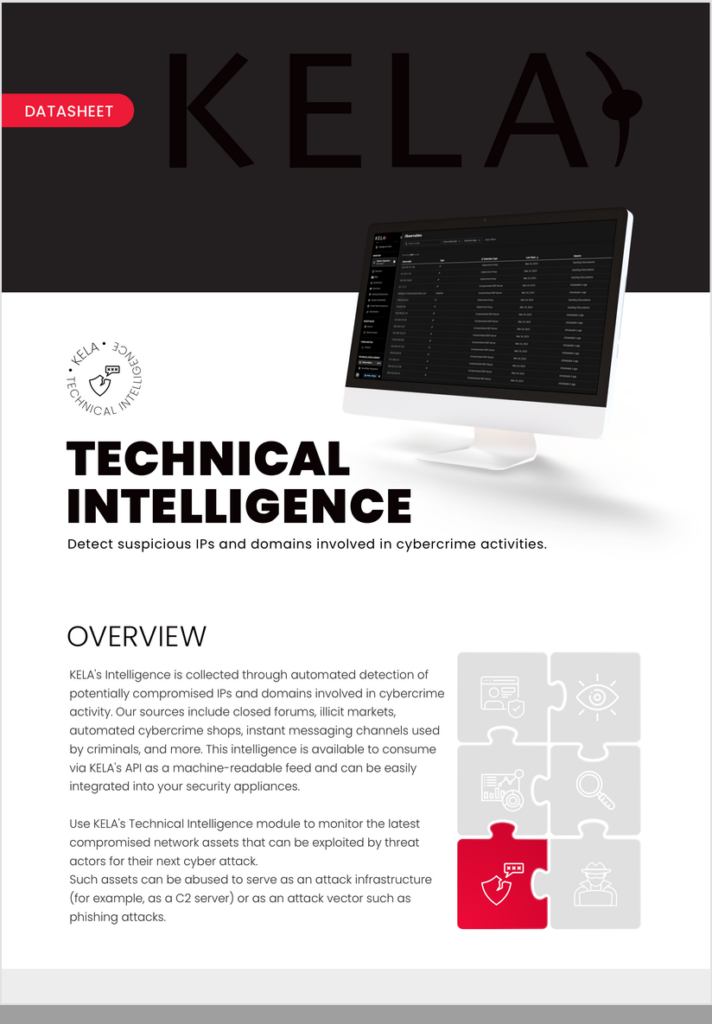
KELA’s Technical Intelligence turns the cybercrime underground into a machine-readable feed of indicators. It automatically detects potentially compromised IPs and domains mentioned in closed forums, illicit markets, automated cybercrime shops and instant messaging channels, and delivers them through KELA’s API in STIX and other formats.
Integrated into your SIEM, SOAR or security appliances, the feed lets you monitor or block compromised assets that could be abused as attack infrastructure, such as C2 servers, or as phishing vectors, before they are used against you.
Key benefits:
- Seamless integration: machine-readable intelligence in STIX format for your SIEM, SOAR or firewall
- Real-time updates on compromised IPs and domains seen in cybercrime activity
- Comprehensive coverage from a wide range of cybercrime underground sources
- Contextualized intelligence: understand the source and how each asset was compromised
- Improved threat hunting and proactive blocking of attack infrastructure



