







Third-Party Risk Management from the Attacker’s Side
Third-party risk management that watches your suppliers the way attackers do: their exposed assets, leaked credentials and infostealer infections, scored continuously from a domain with no questionnaires to wait for. See which vendor is a way in before it is used.
Which of your vendors is exposed right now?
Security posture shifts constantly across vendors. Continuous attack surface monitoring delivers up-to-date intelligence on third-party exposures, enabling informed decisions, faster remediation, and measurable risk reduction.

Identify
Real Threats. Real Data. In Real Time.
Uncover risks and signs of compromise tied to your vendors.

Monitor
Prioritize Risk with Intelligence, Not Guesswork.
Go beyond surface-level scoring. Distinguish high-risk vendors and escalate what matters most.

Mitigate
Act Fast with Clear, Targeted Insights.
Receive enriched intelligence and contextual recommendations to drive faster mitigation.
Turn Insight Into Risk Strategy
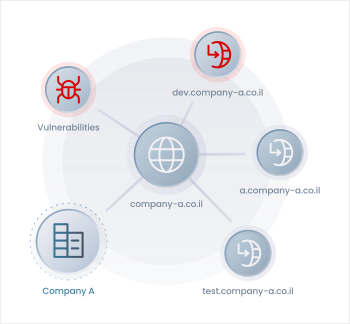
See Your Network the Way Attackers Do
Identify both known and unknown assets through an attacker’s perspective. External infrastructure across third parties is mapped from the outside in, exposing potential entry points and high-risk surfaces visible to adversaries.
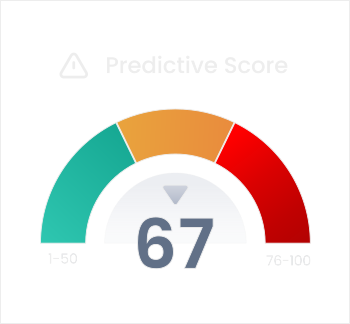
Predict Risk Before It’s Exploited
The predictive score reflects the likelihood of an attack, using CTI and external indicators such as threat trends, industry sector, and geographic exposure. By accounting for real-world attacker behavior and external context, it enables proactive decisions before an attack unfolds, not just based on what’s visible, but on what’s likely.
Align Third-Party Risk with Compliance Standards
Support compliance efforts by continuously monitoring vendor adherence through standardized and customized questionnaires. Capture critical security and regulatory data, ensure alignment with internal policies, and track responses across frameworks like NIS2, DORA, and ISO 27001. All while maintaining a clear audit trail.
Built for Scalability, Simplicity, and Speed
Designed to support large, diverse vendor ecosystems, the platform delivers key capabilities that make third-party risk management more efficient, flexible, and scalable
Onboarding
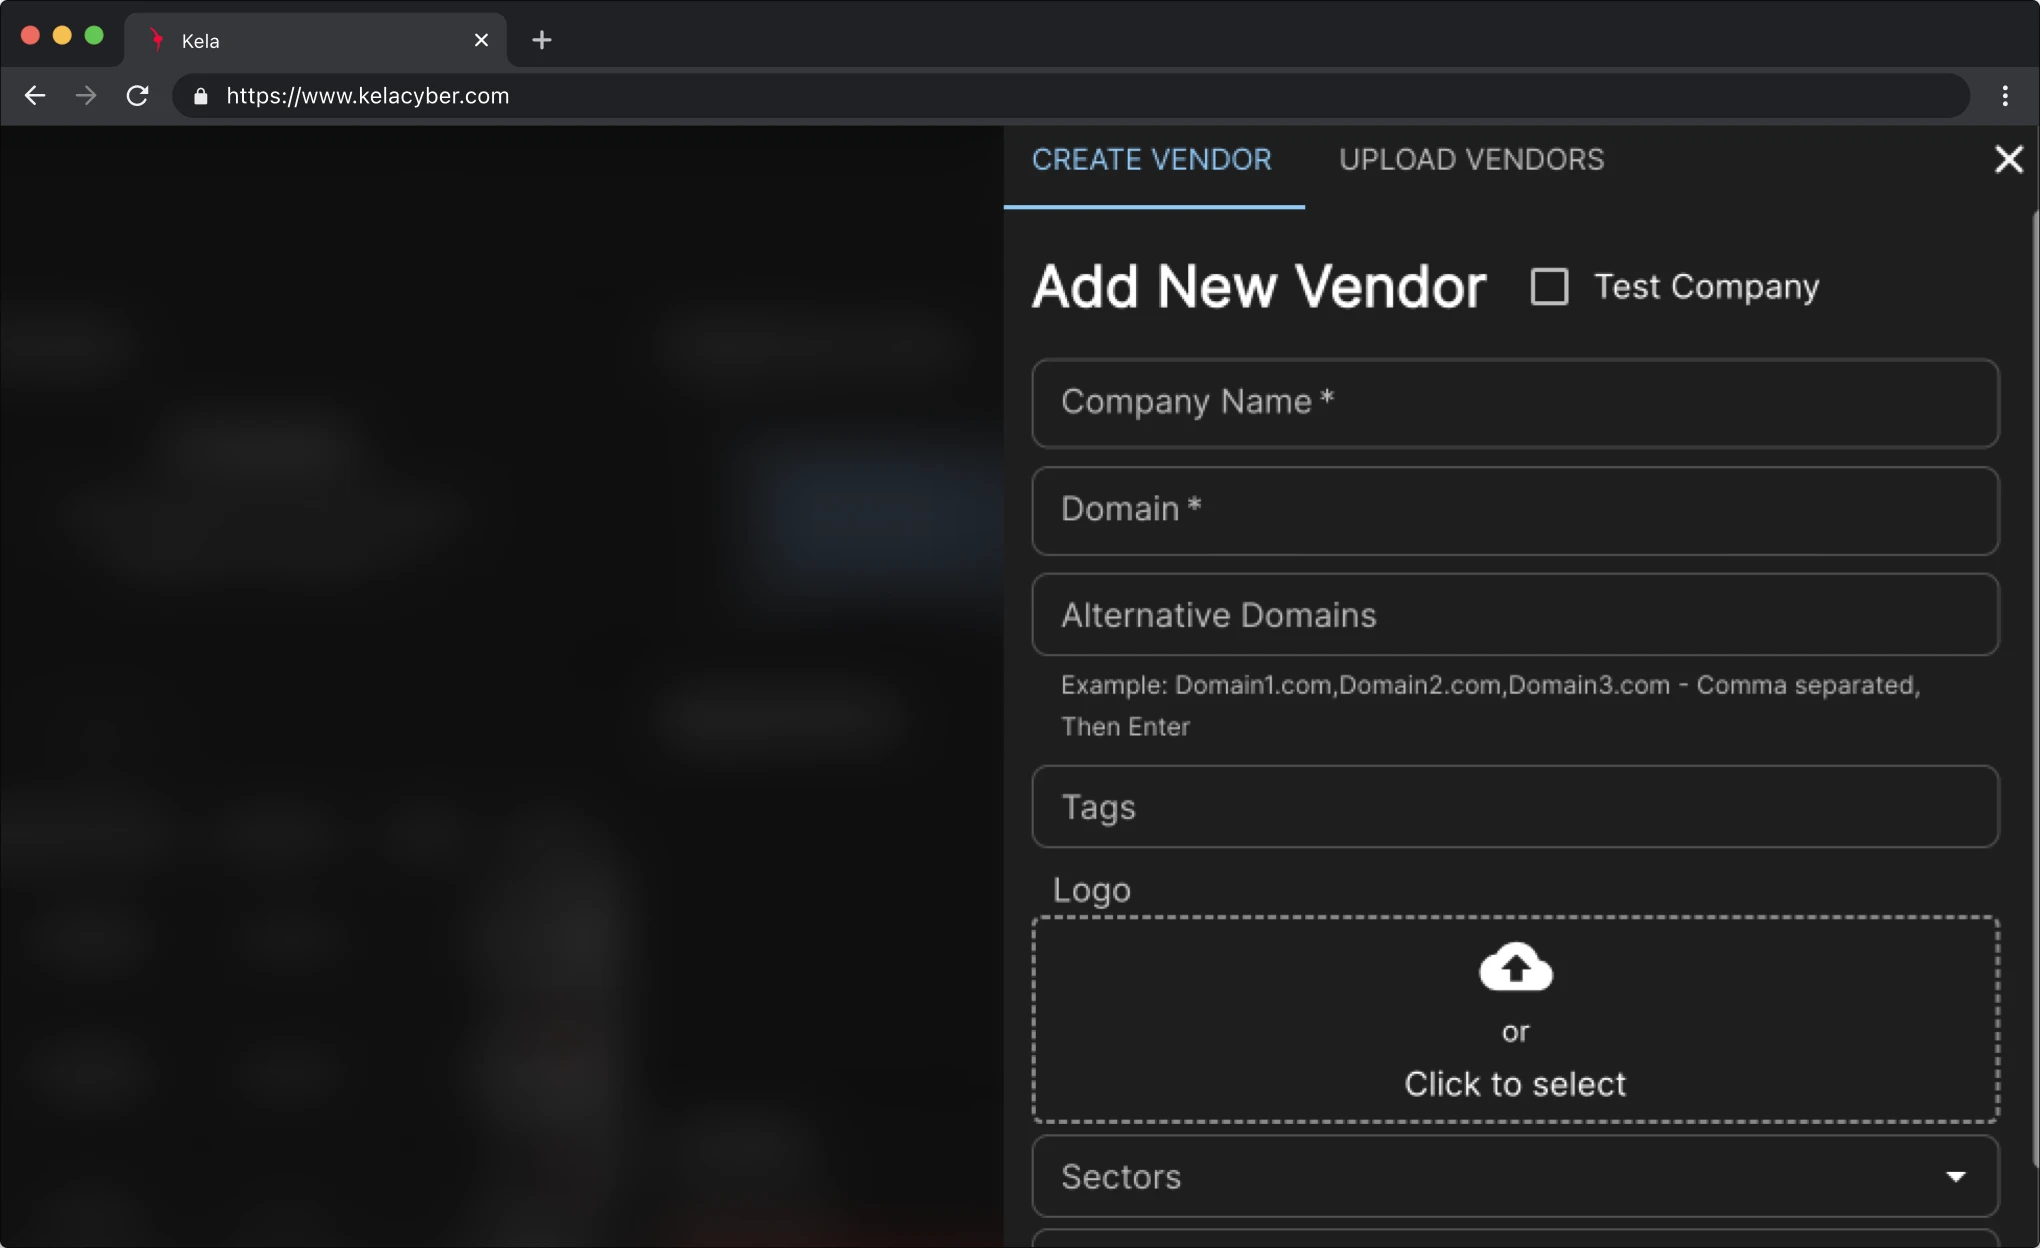
Agentless Onboarding
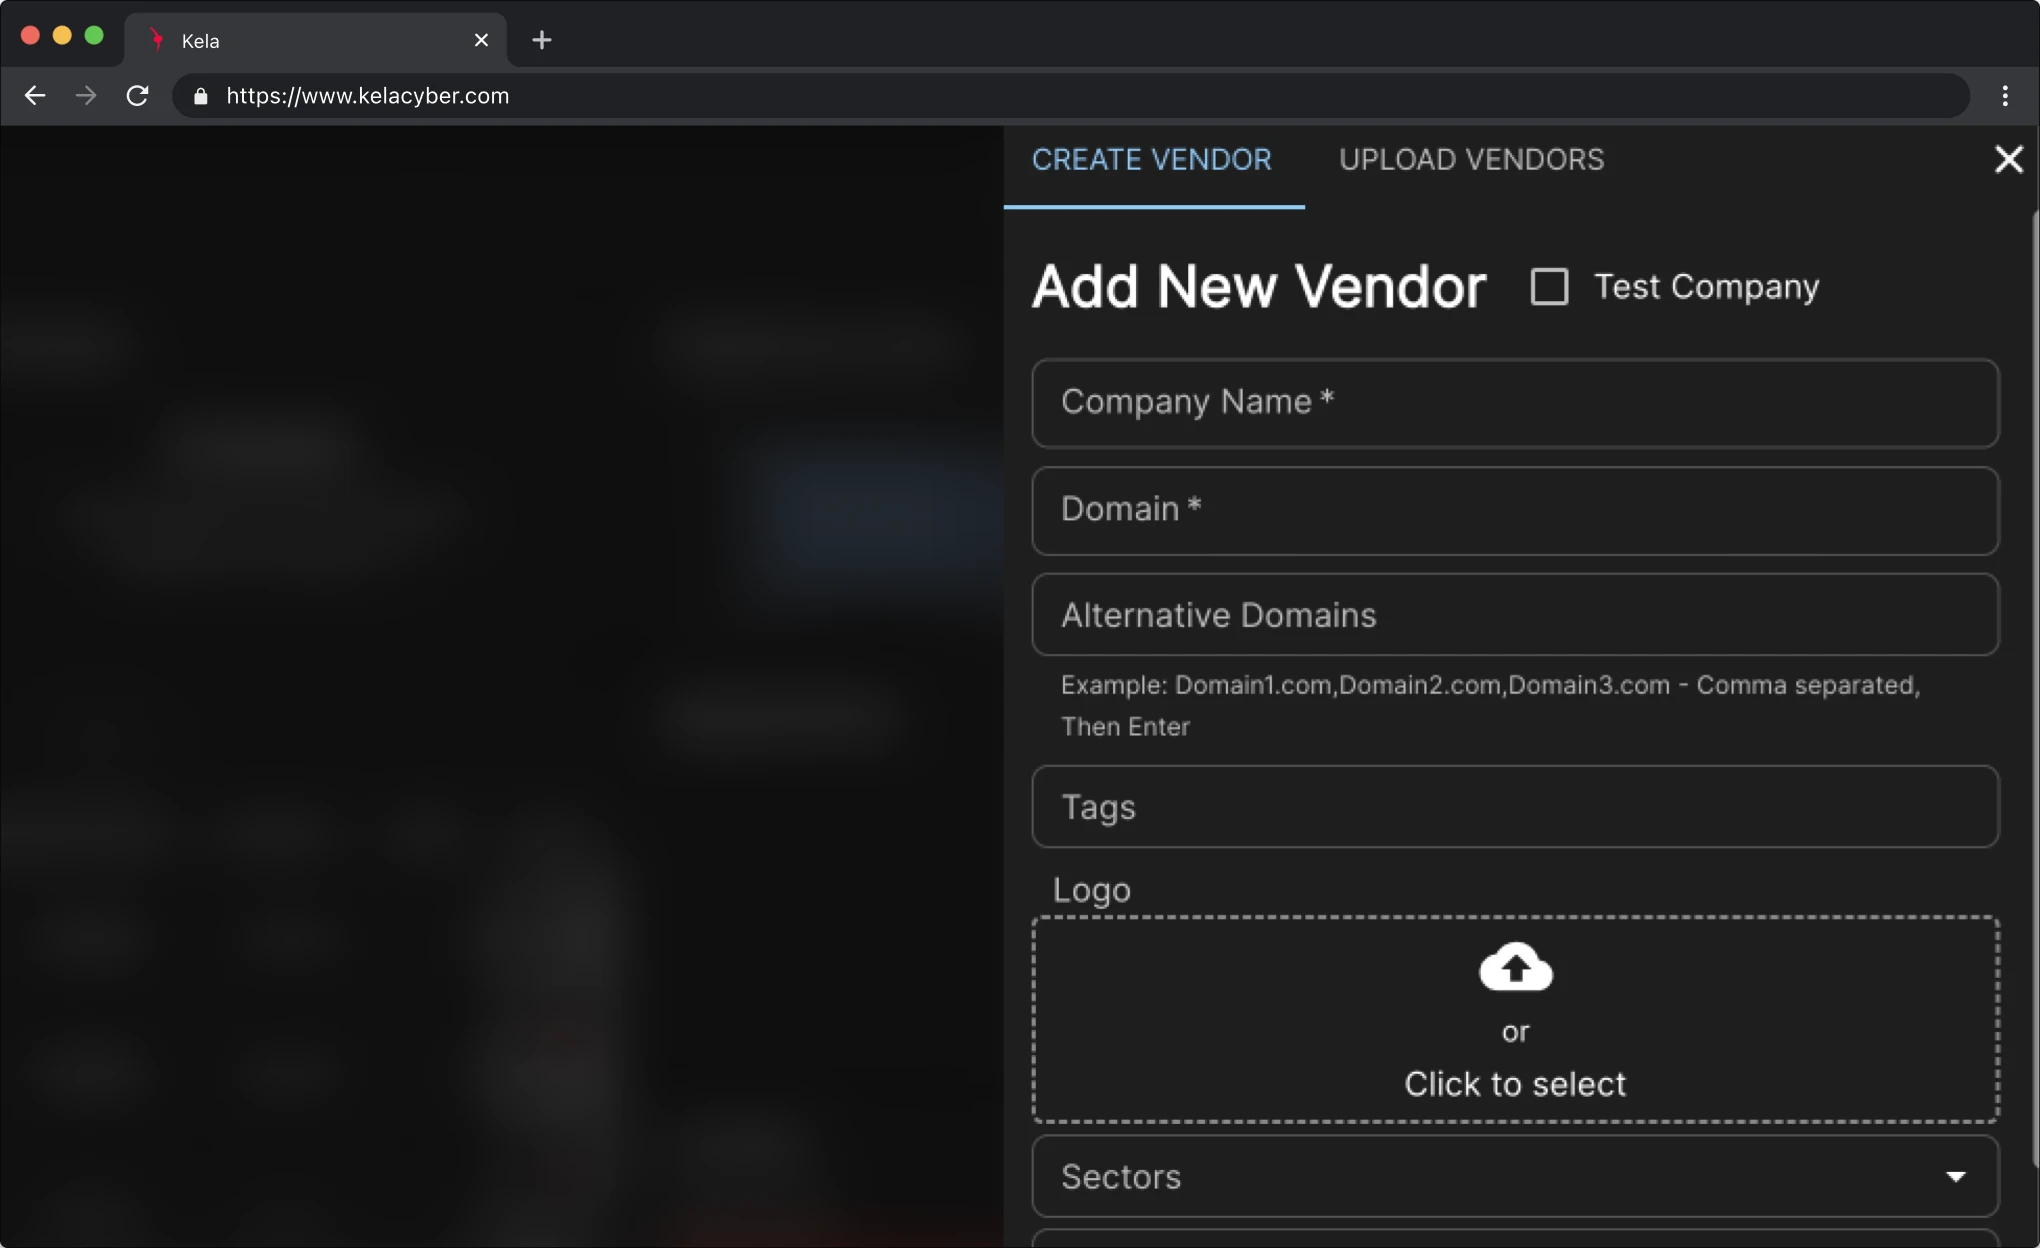
Instant, safe access using just a domain. No installation or setup required.
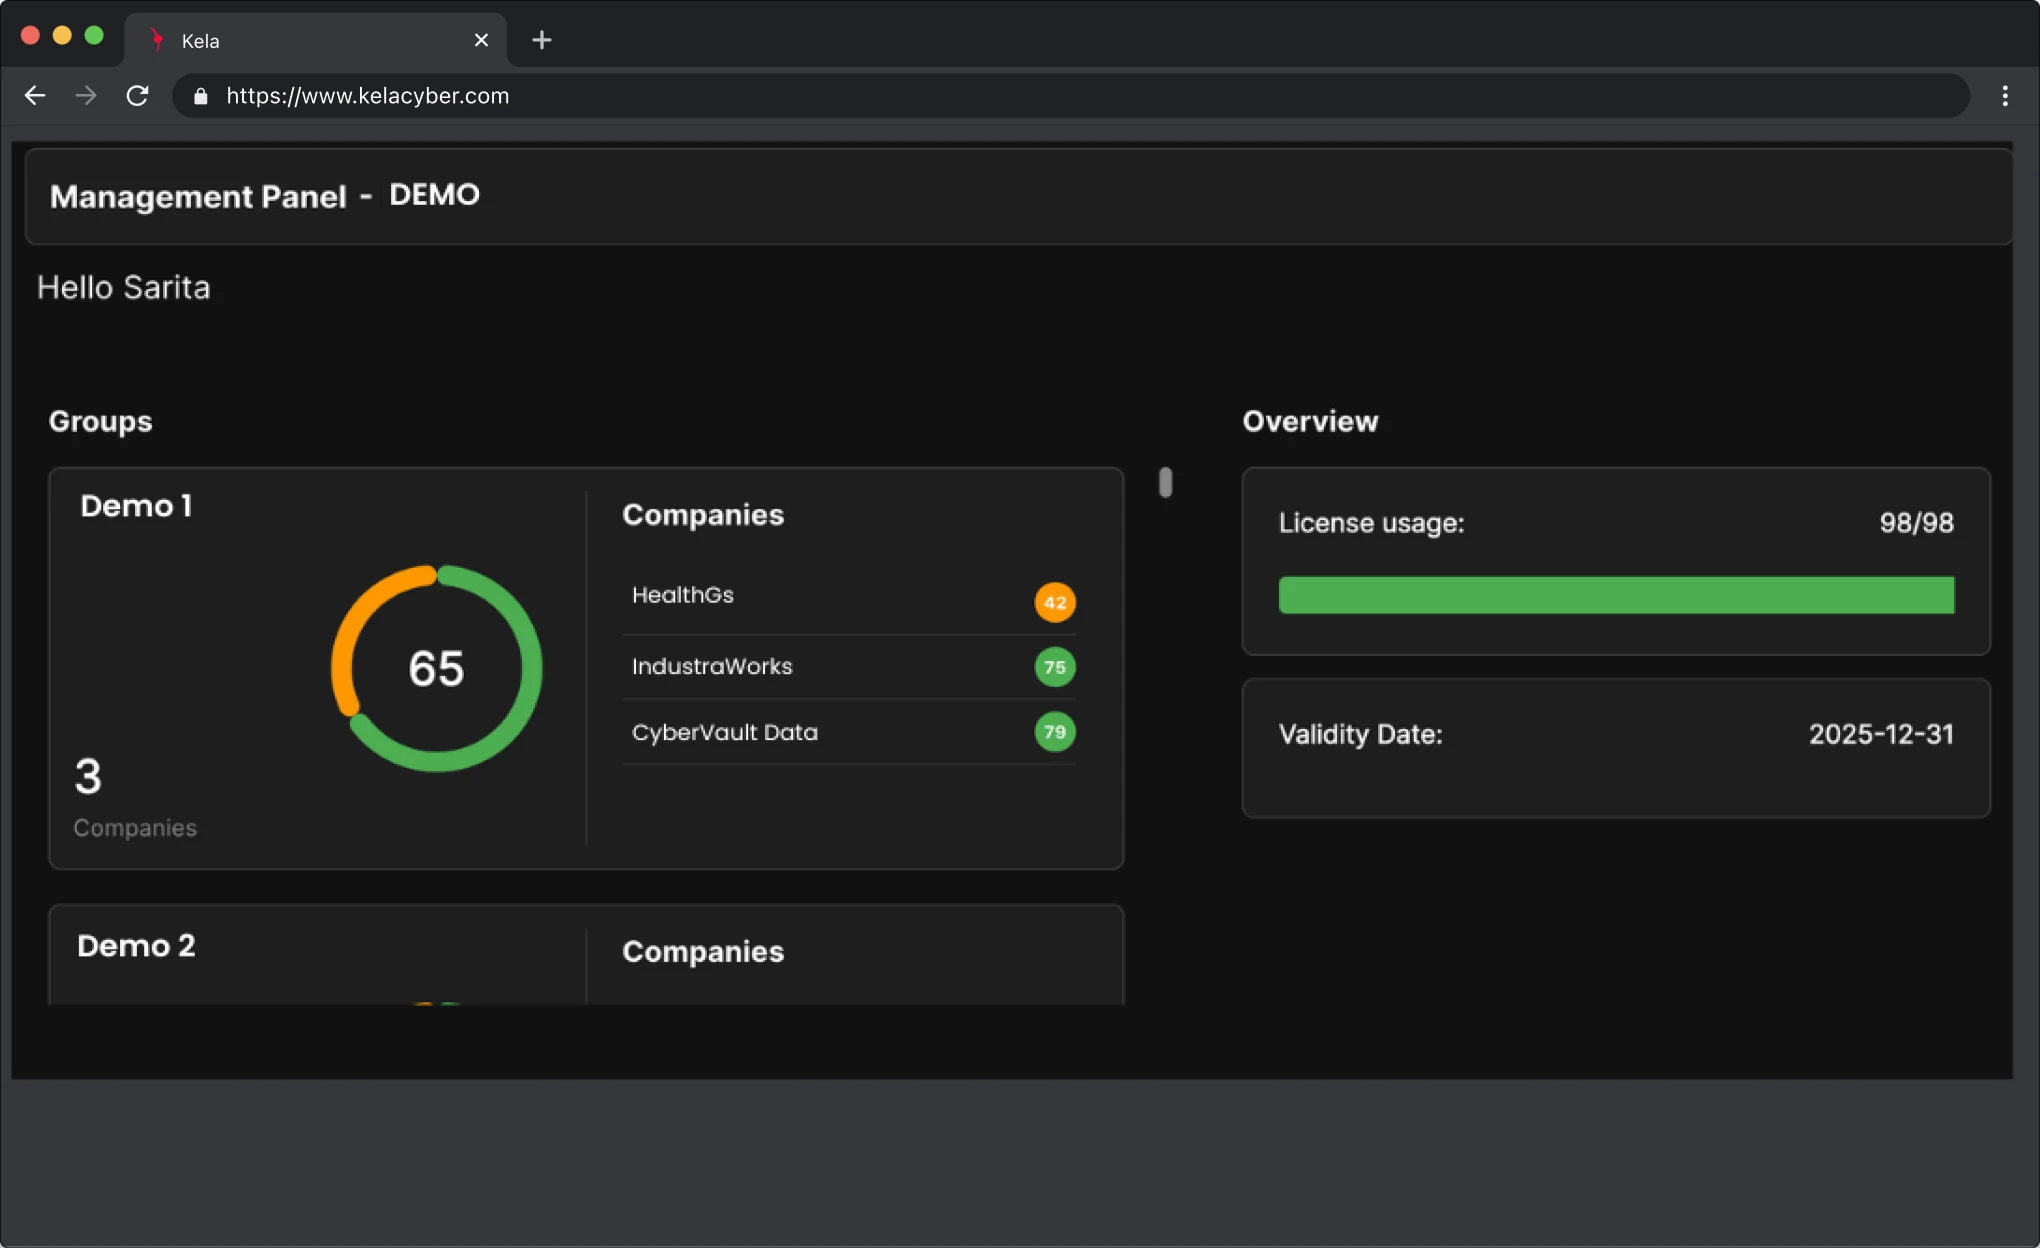
Multi-Tenant
Multi-Tenant Environment
Manage multiple organizations or business units from a single, centralized platform.
Reports
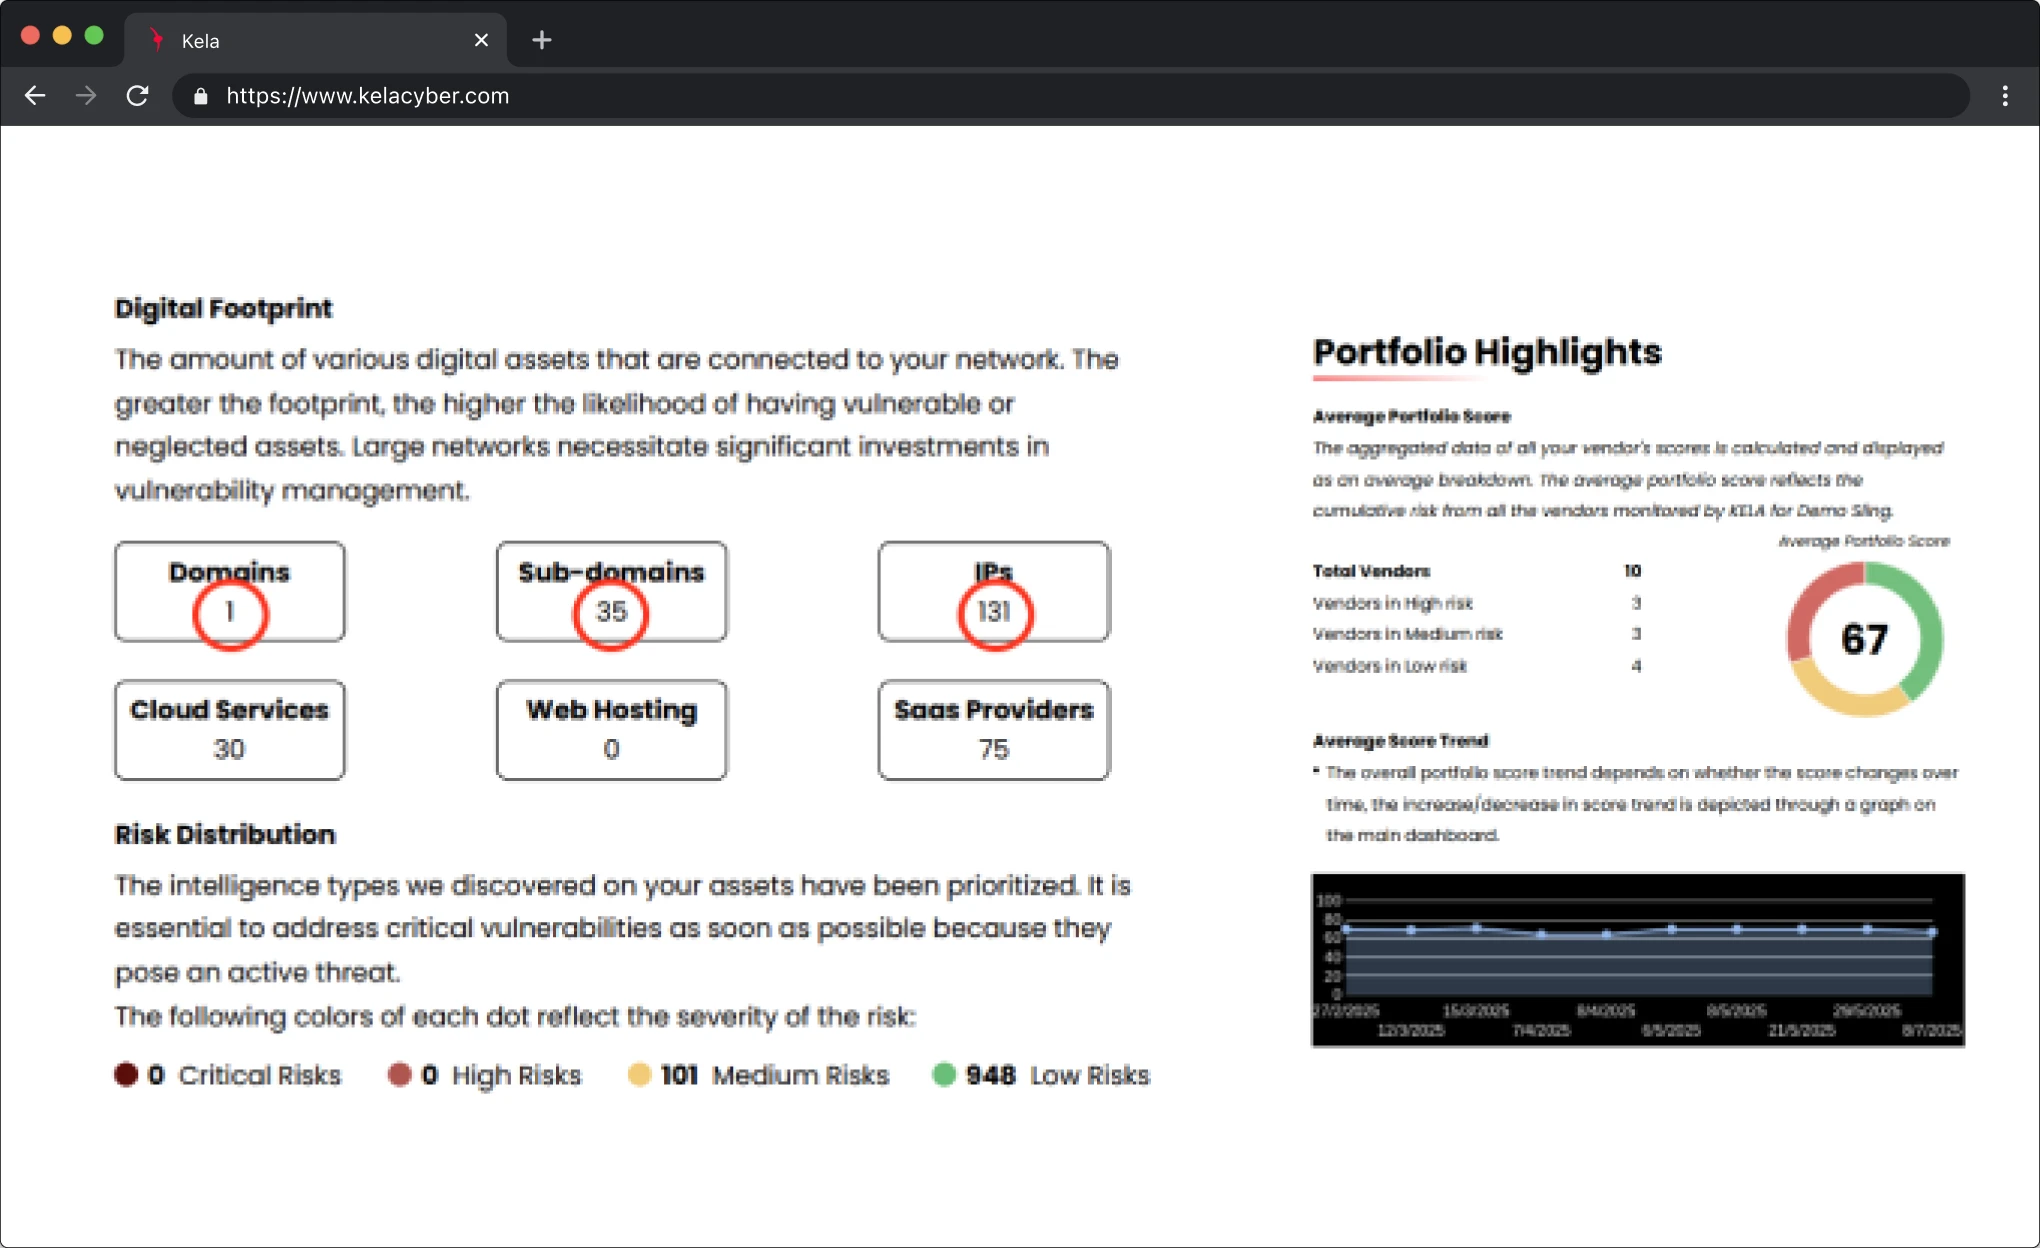
Downloadable Reports
Export portfolio, vendor cyber risk, and compliance insights as PDFs or editable DOCX files for easy sharing and customization.
Trends
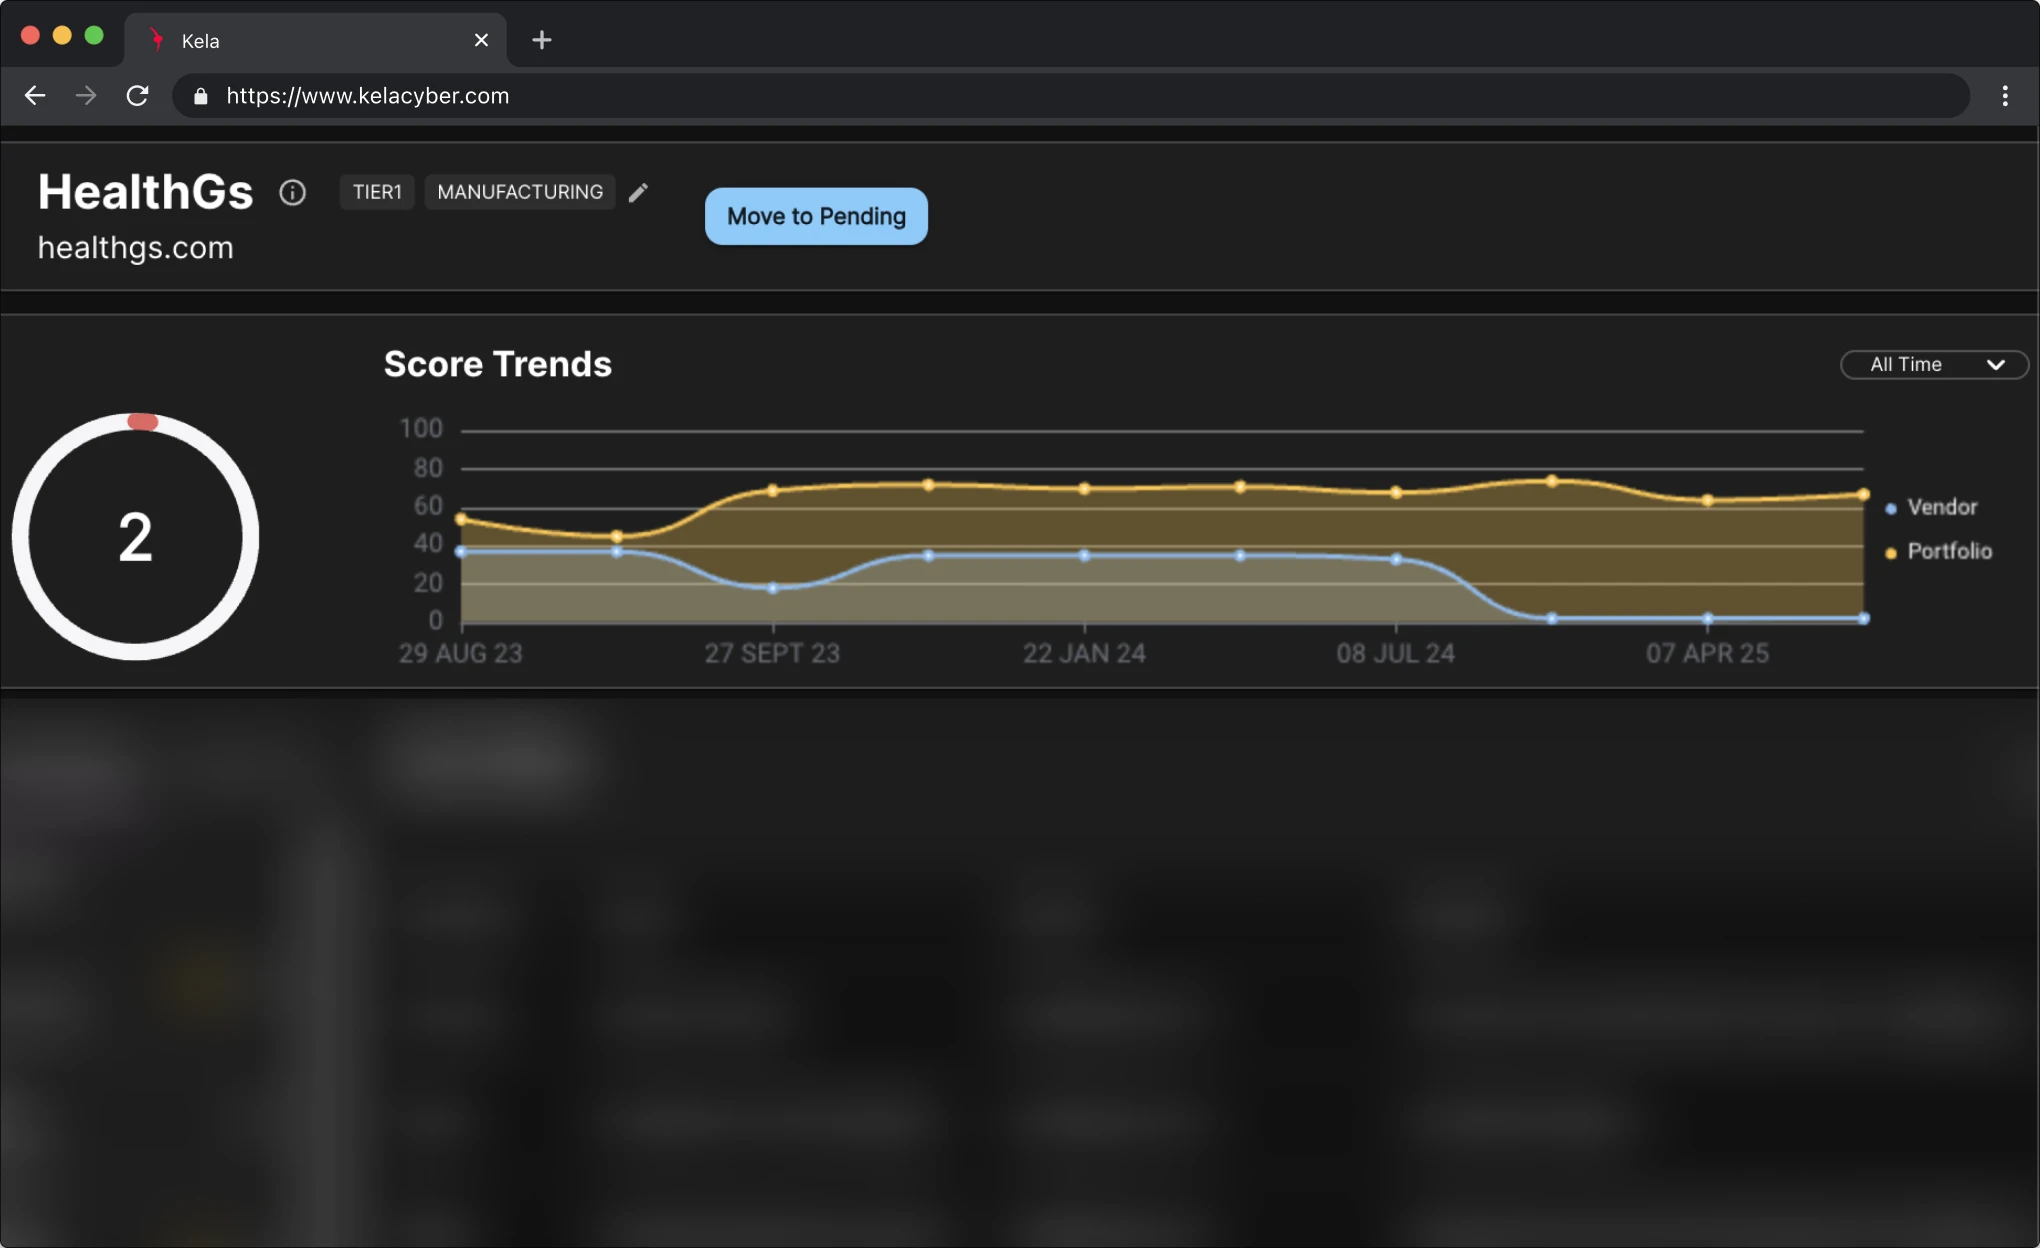
Score Trends
Track risk score changes over time across your entire portfolio and individual vendors to monitor progress and emerging threats.
Dashboards
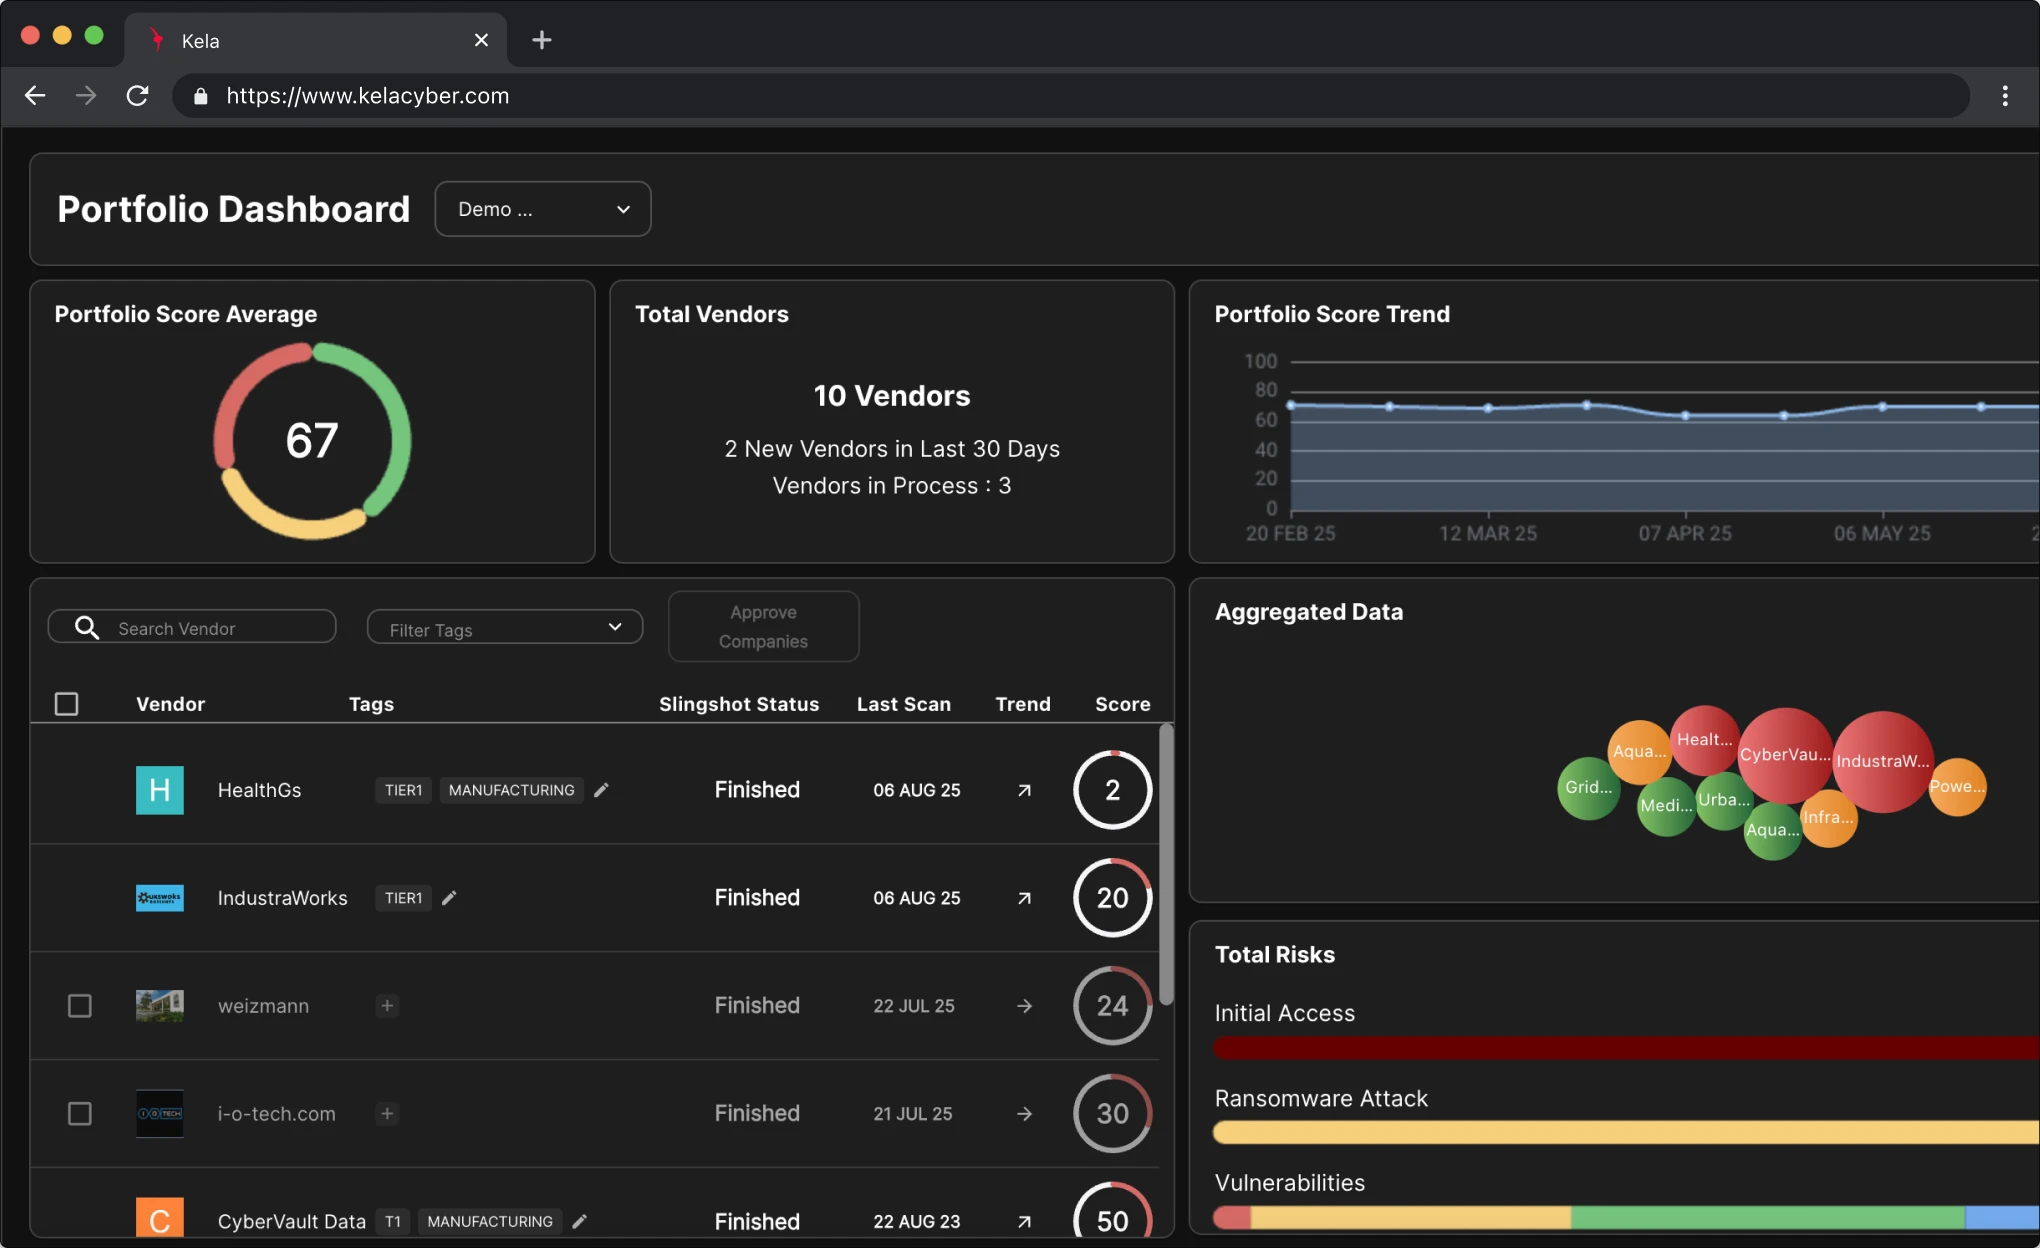
Dashboard View
Access in-depth insights with dedicated dashboards for portfolio, vendor, and compliance monitoring.
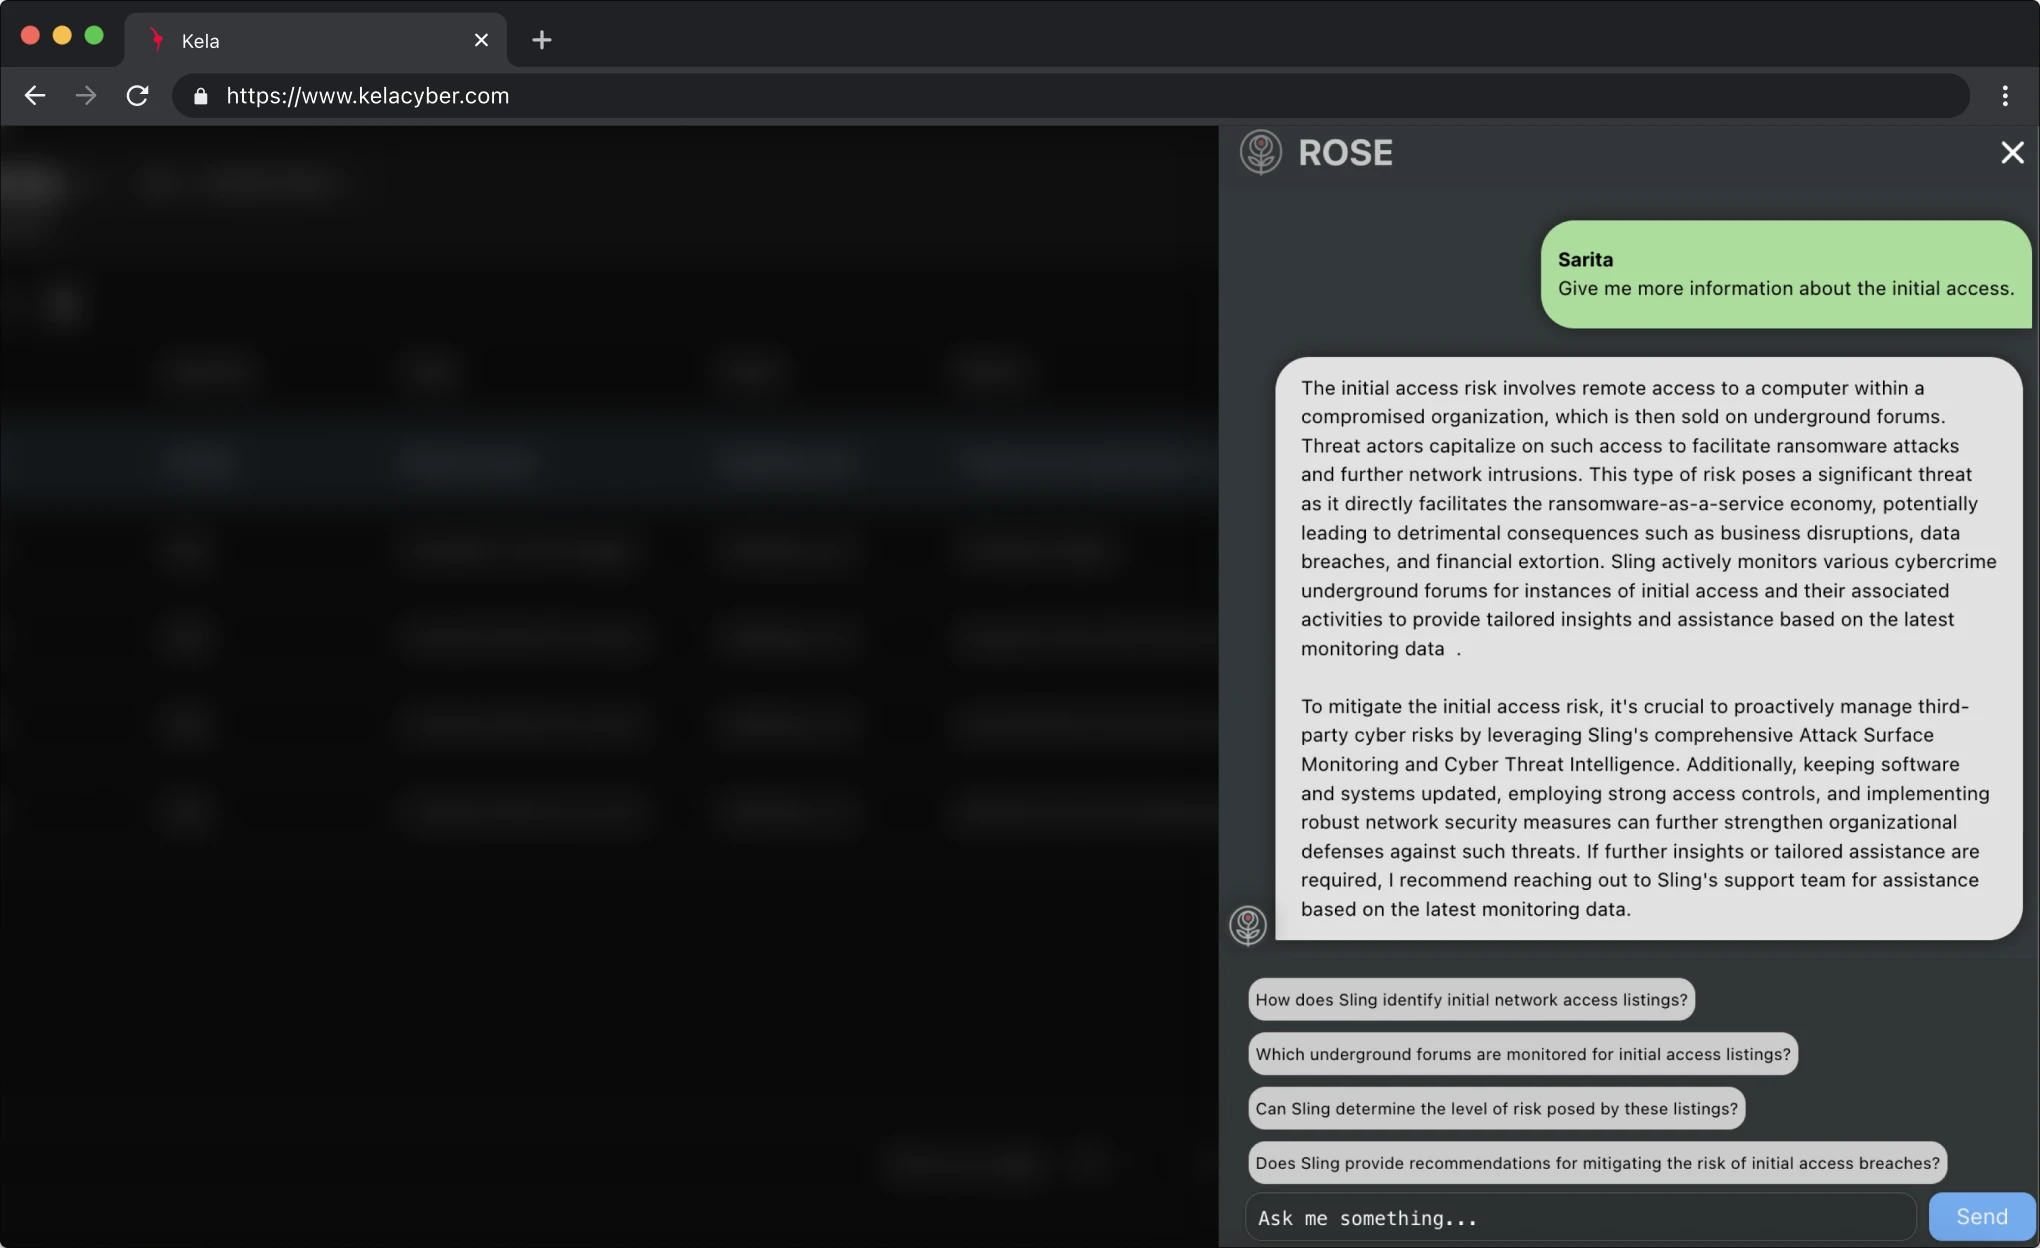
ROSE AI
ROSE AI
Conversational AI assistant for enriched risk context, faster investigations, and guided remediation.
Alerts
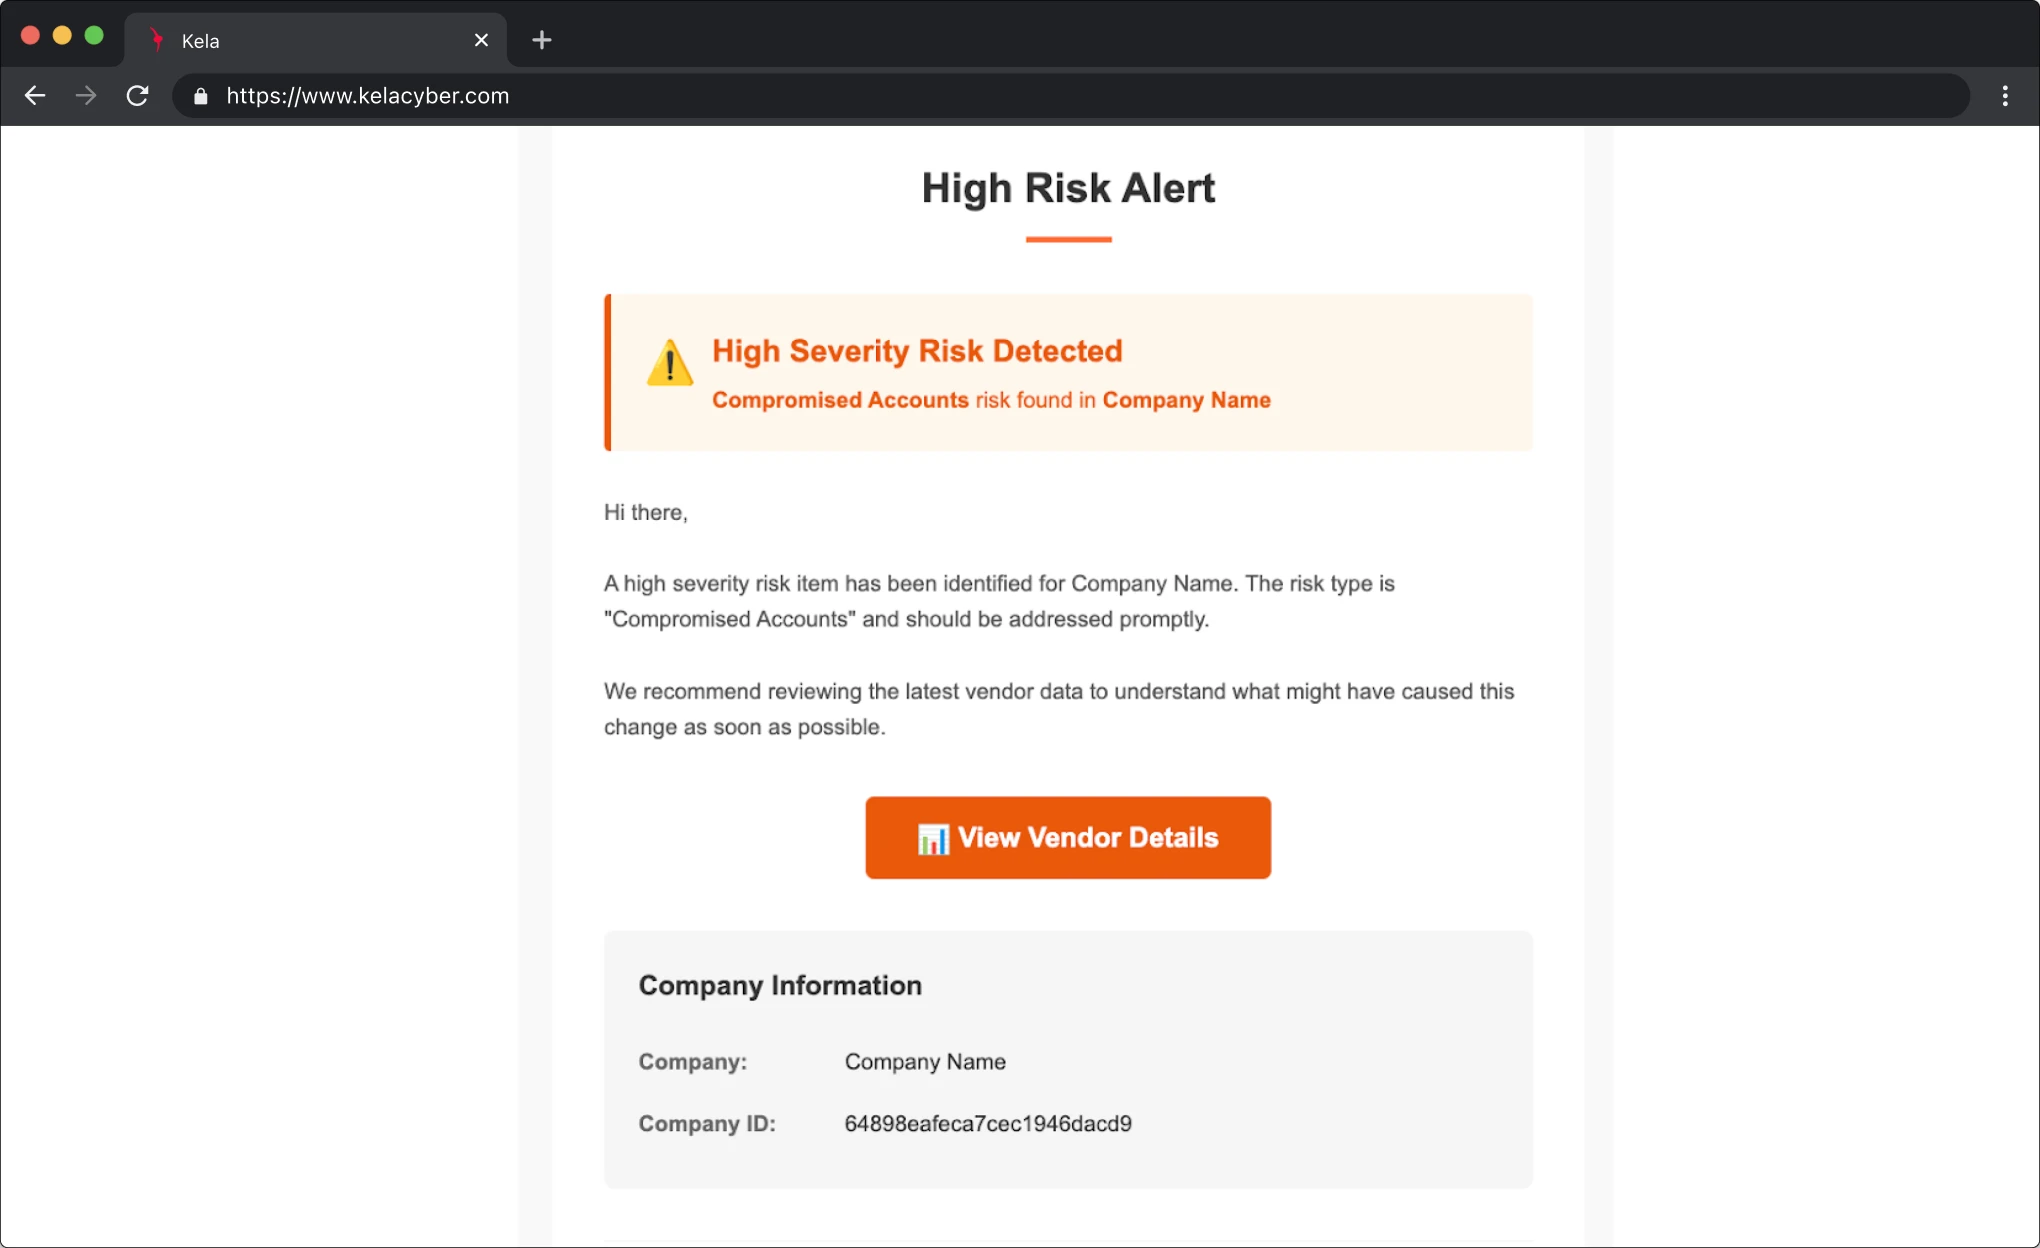
Real-Time Alerts
Instant email notifications on critical risk changes and emerging threats.
Blacklisting
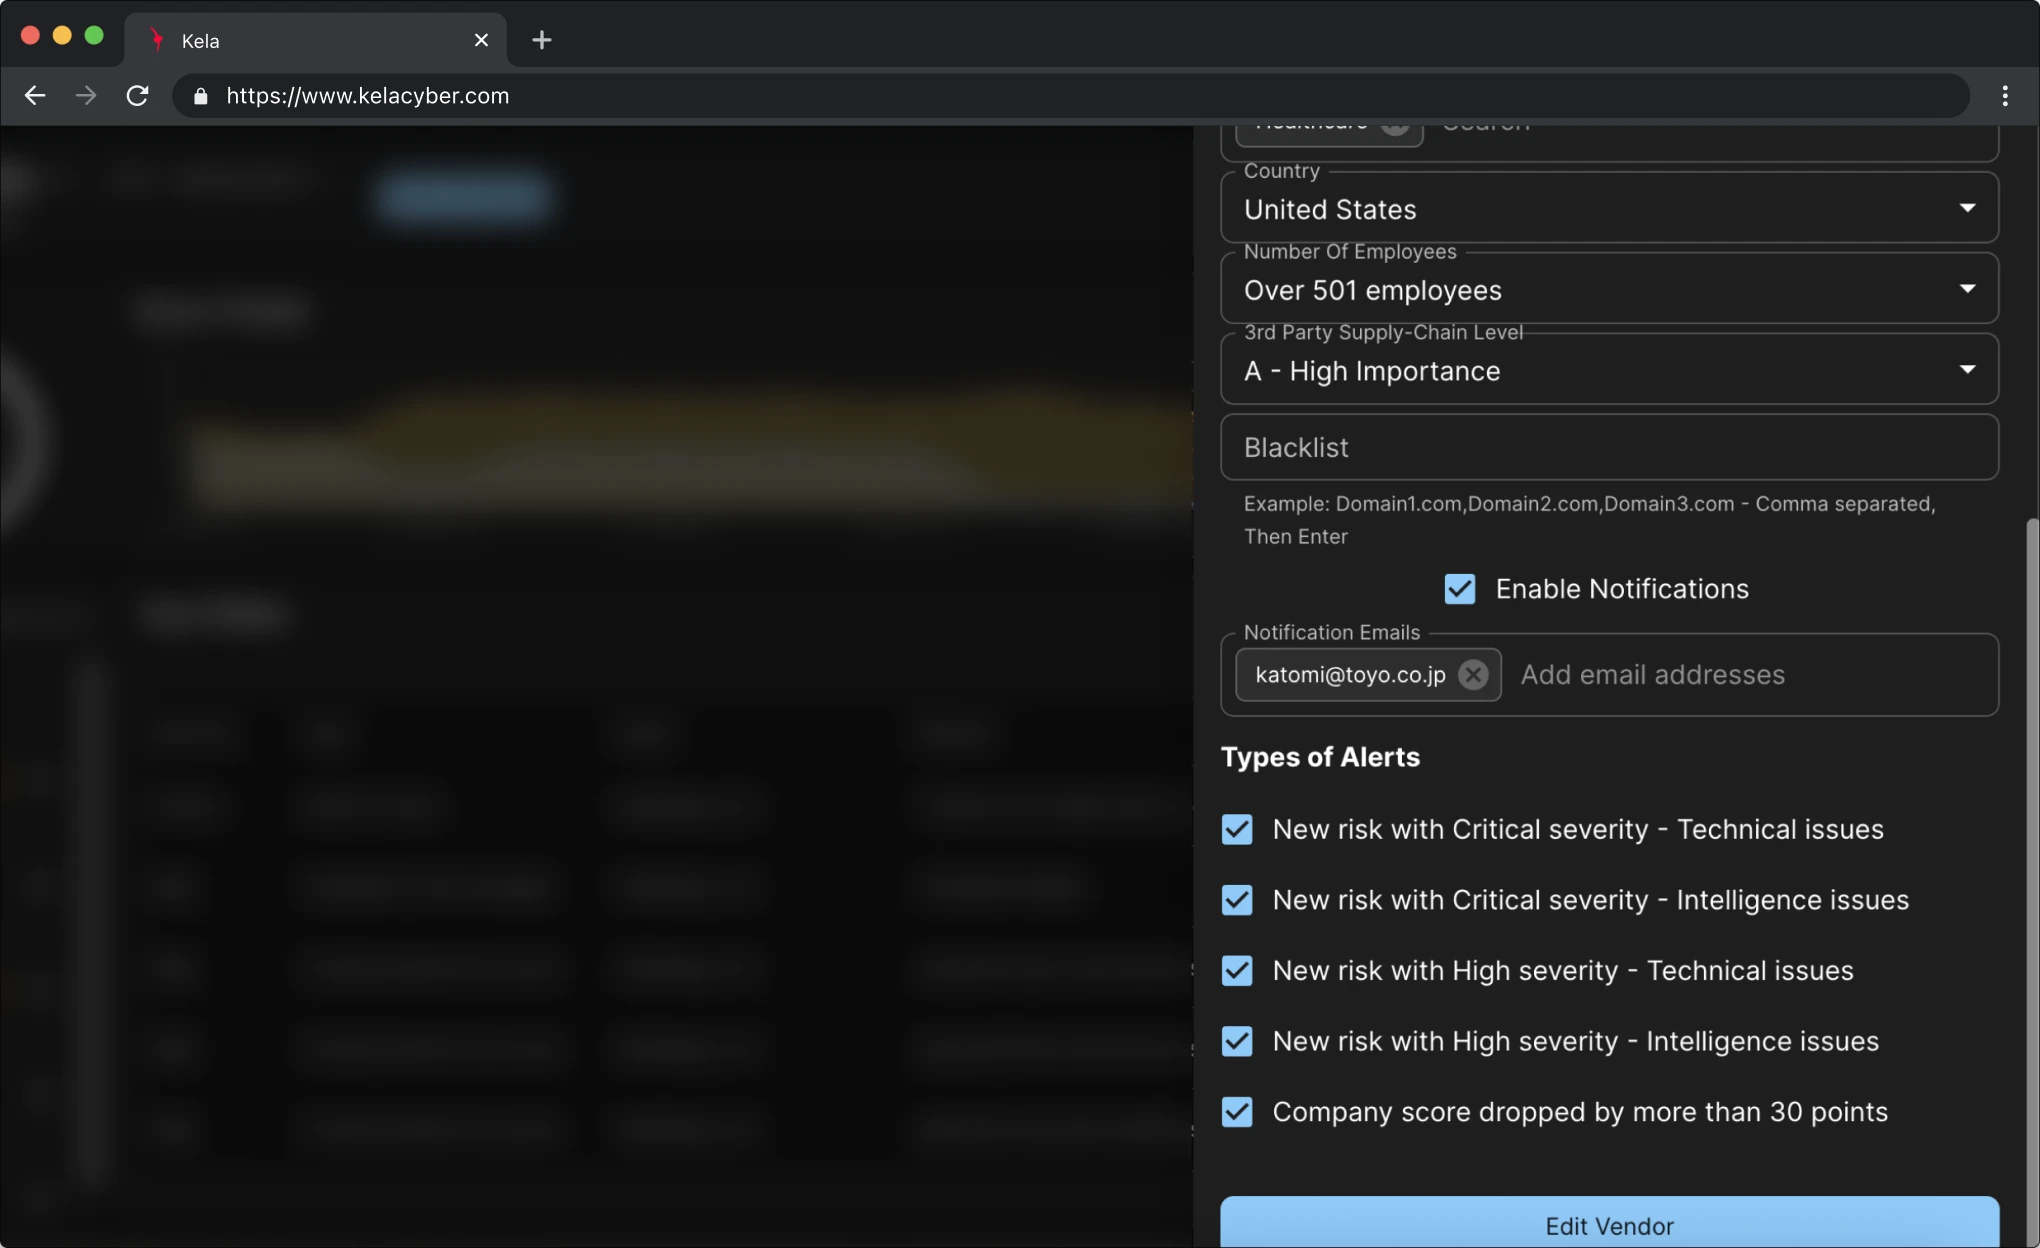
Asset Blacklisting
Easily blacklist any domain to exclude unwanted or irrelevant assets from your monitoring scope.
Risk Intelligence
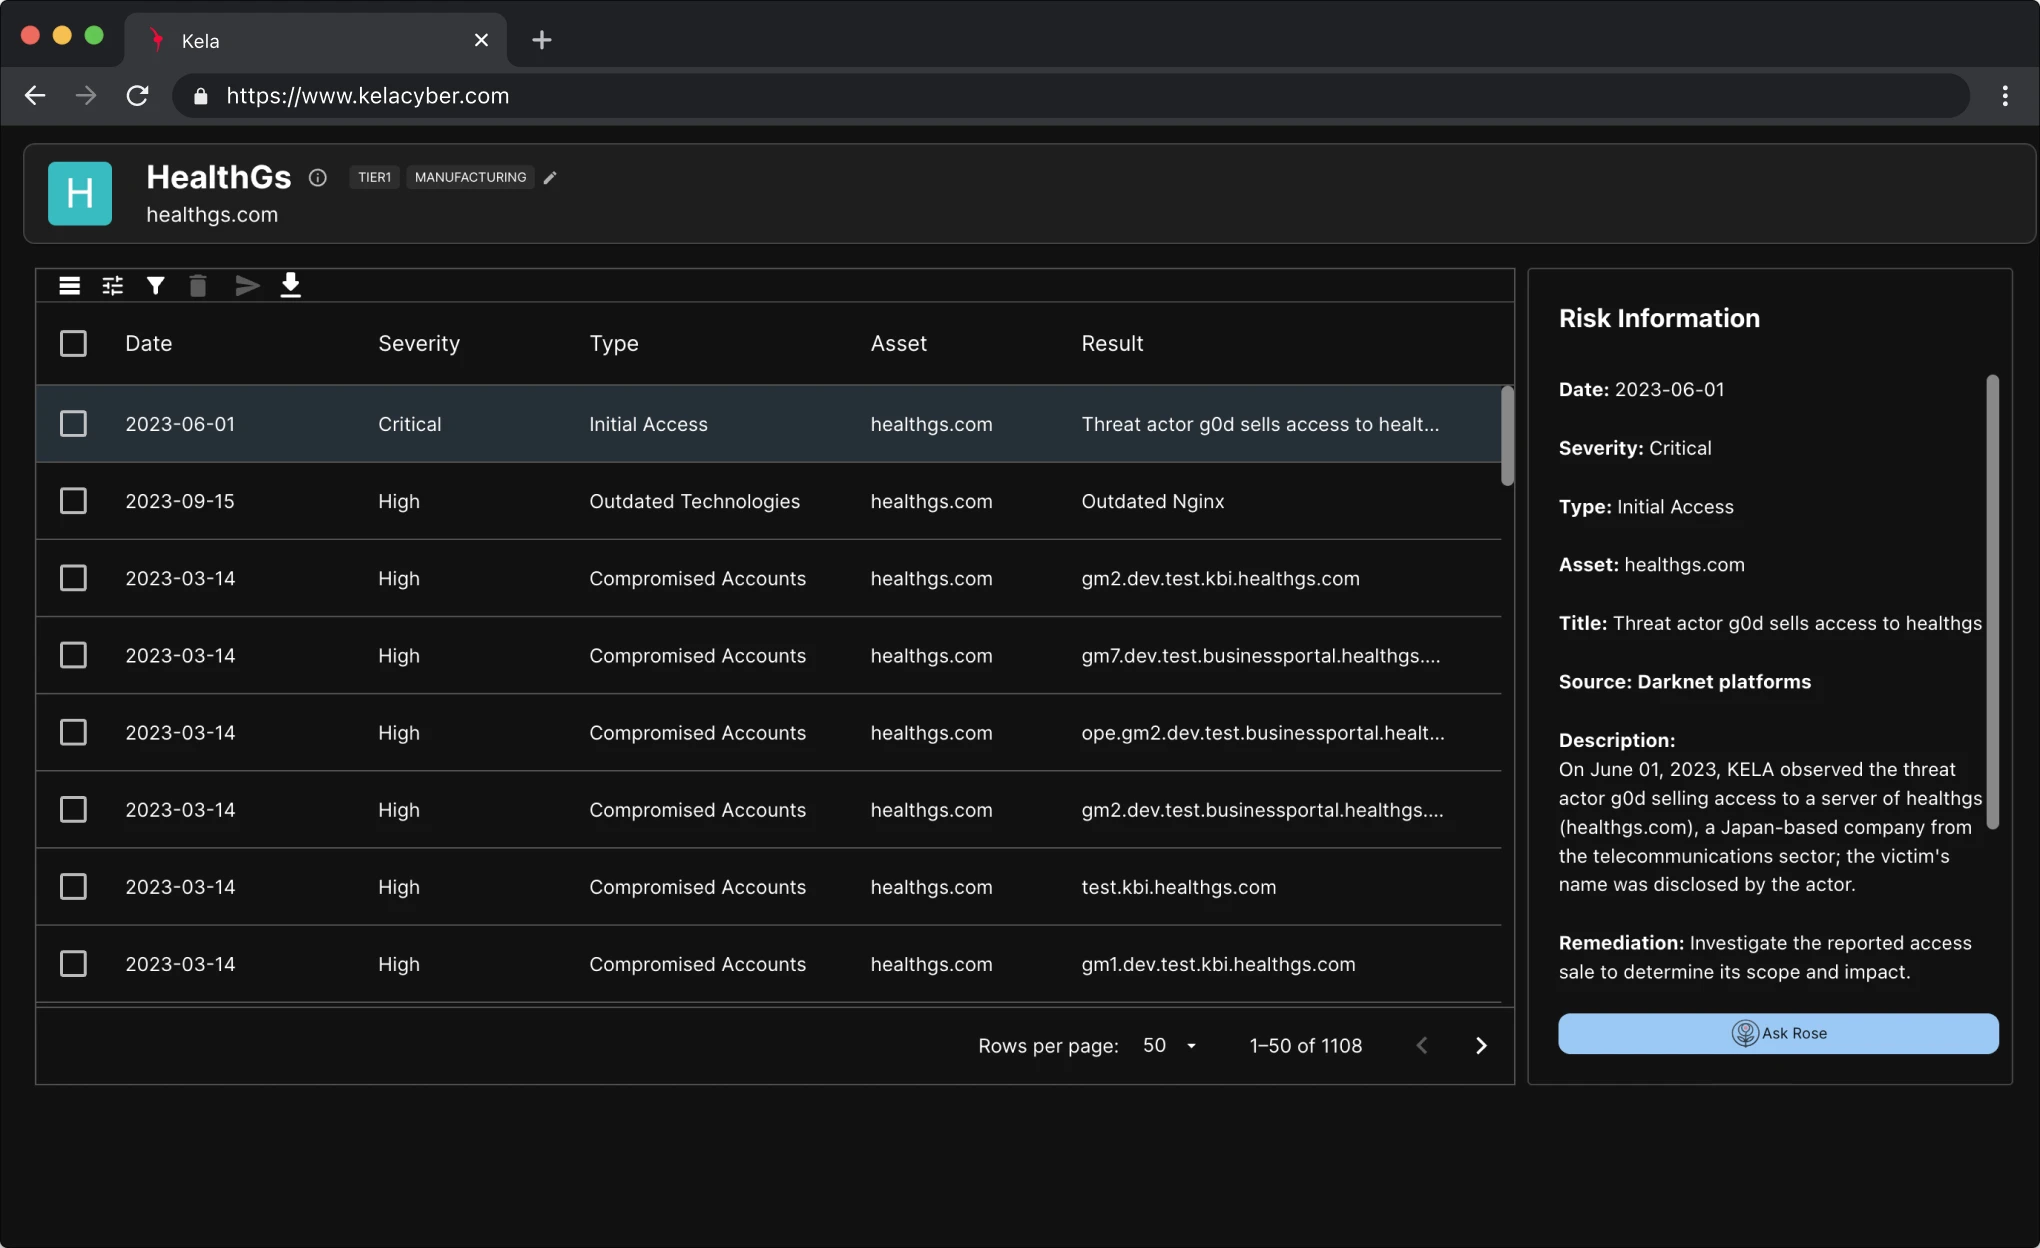
Risk List & Intelligence
View top and full risk lists by type and severity, including vulnerabilities, exposed credentials, and ransomware activity—enriched with technical, dark web, and ransomware intelligence for comprehensive threat detection.
Book a Demo
Prefer to schedule a meeting right now? Click here.
FAQ
Do I need consent from vendors to monitor their risk?
No. The platform uses passive, external scanning techniques that don’t require any action or consent from your vendors.
Do I need to install anything for monitoring?
No. The platform is completely agentless—monitoring begins with just a domain, with no setup or installation required.
How often are scans performed and data updated?
Monitoring is continuous to provide real-time visibility, while the frequency of the scans can be customized based on your specific needs.
What compliance frameworks are supported?
KELA TPRM supports a wide range of frameworks, including NIS2, DORA, ISO 27001, HIPAA and custom internal policies through customizable questionnaires.
Is the platform available in multiple languages?
Yes, currently, the user interface supports English, Spanish, Japanese, and Portuguese, with more languages planned.
Does the platform integrate with existing tools?
Yes. We offer integrations via API.


