







Prevent Breaches Before They Escalate with Proactive Cyber Threat Intelligence
Cyber Fusion for full visibility across intent, context, and infrastructure.
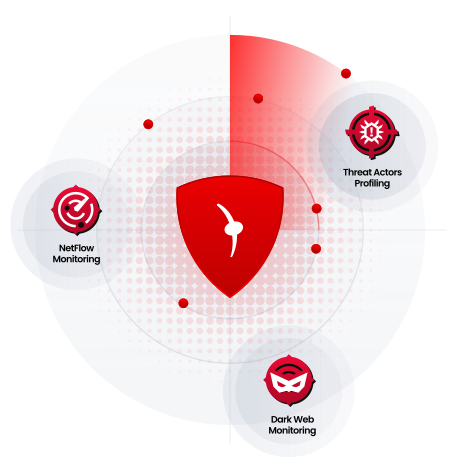
From Threat Signals to Actionable Truth
KELA’s unified CTI suite fuses adversary intent with enriched technical intelligence and global traffic telemetry to turn fragmented signals into actionable truth – helping teams validate threats faster and disrupt attacks earlier.

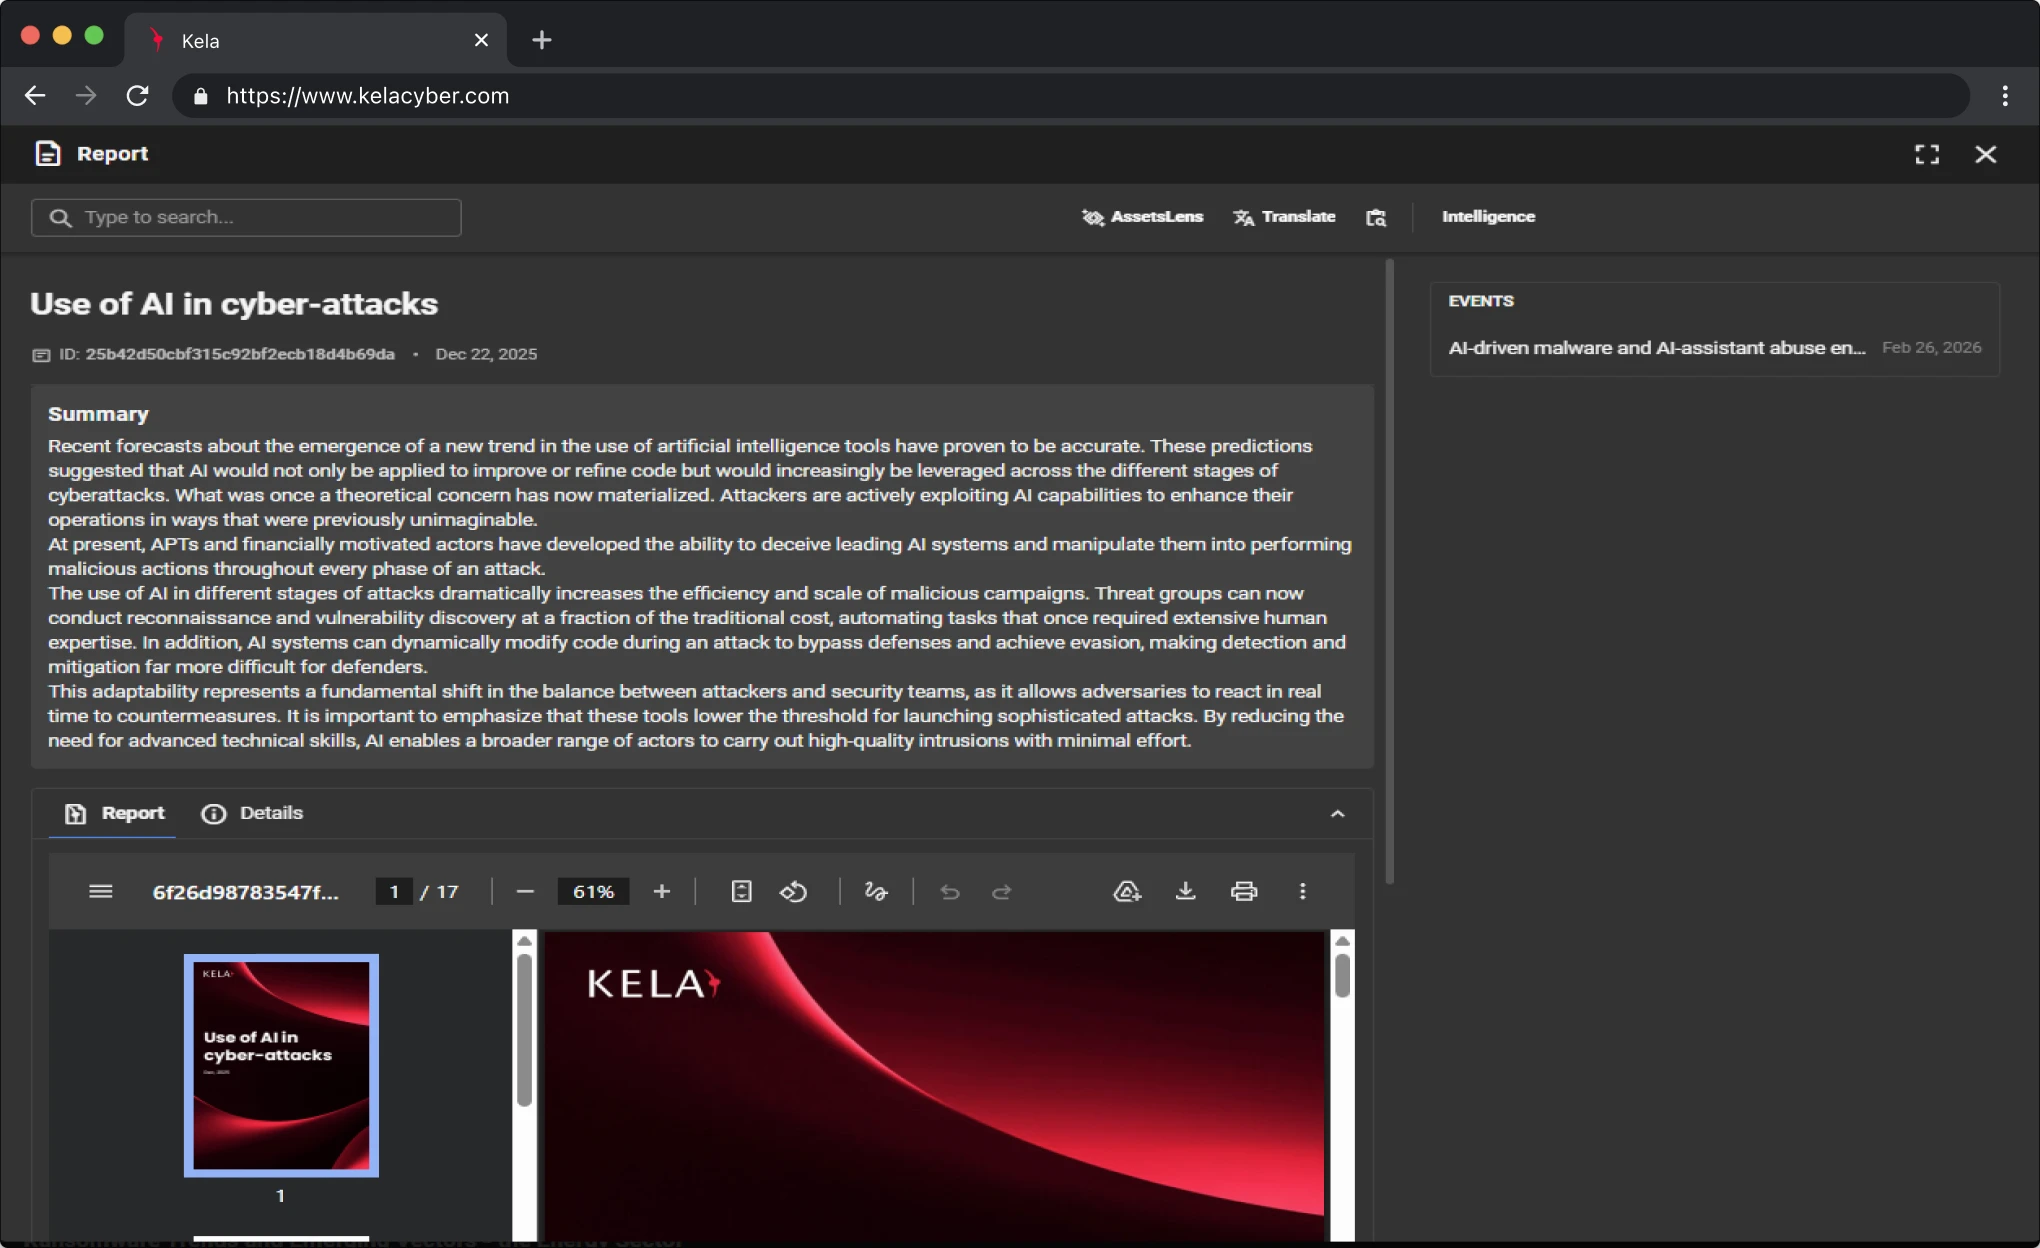
Intelligence Fusion
Turn fragmented signals into actionable truth.
Intelligence fuses disparate signals into a single, actionable truth

Global Network Intelligence
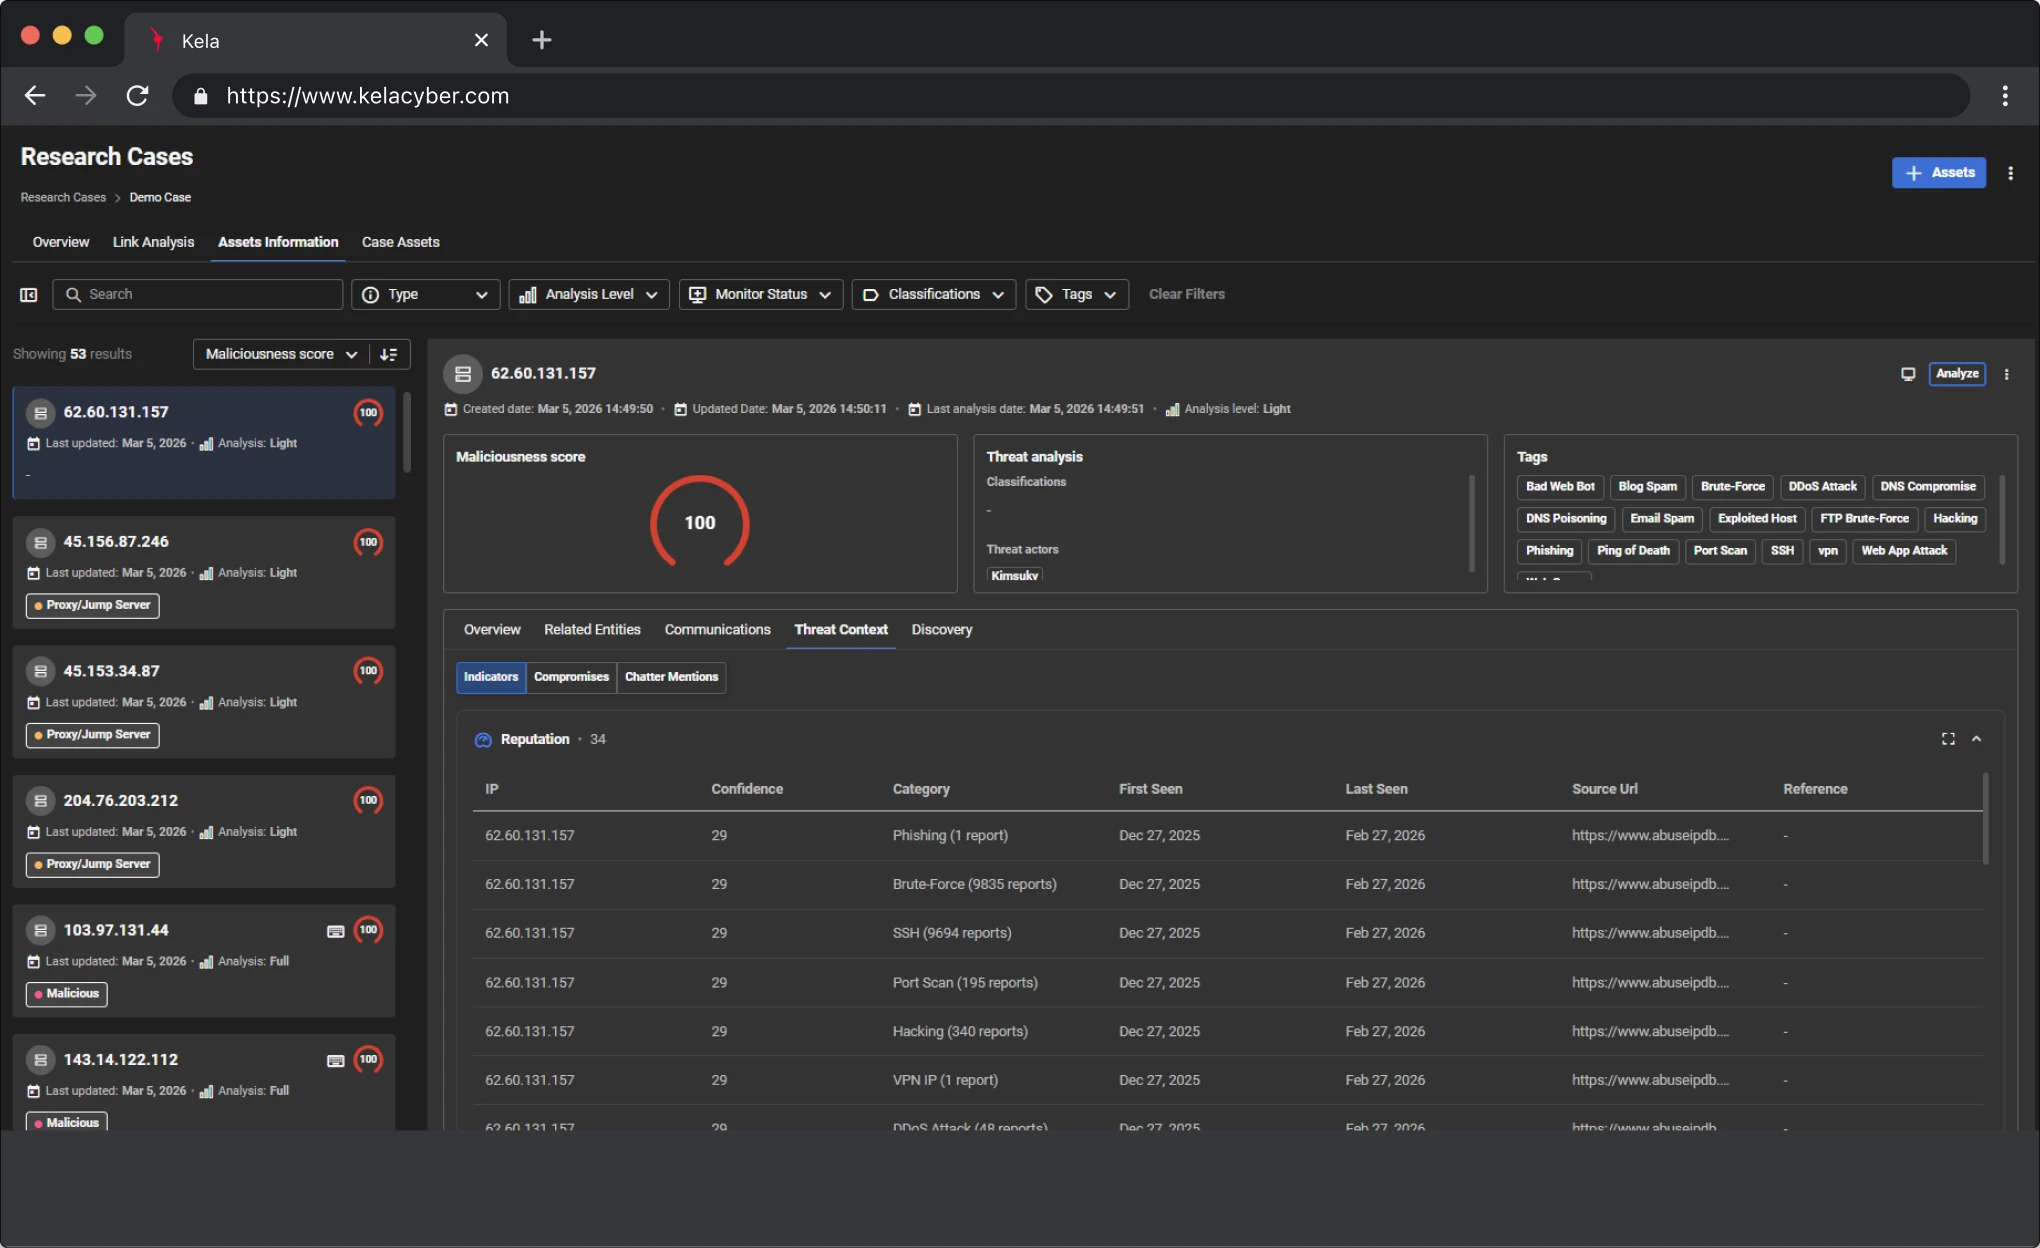
Validate threats with external telemetry
Gain visibility into global internet traffic to identify suspicious communications

Pre-emptive Threat Hunting
Disrupt attacks during staging and reconnaissance.
Get early warning from cybercrime ecosystems to shut down attacks before execution
Detect Earlier. Decide Faster. Act First.
Cyber Fusion – Beyond Data Collection
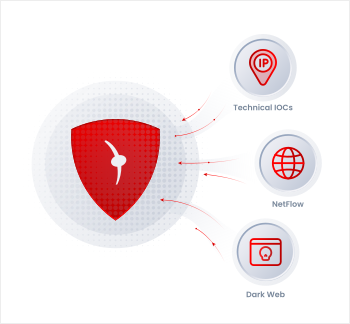
KELA fuses disparate signals into a single, actionable truth. It correlates adversary intent from underground chatter with technical infrastructure and live network telemetry (NetFlow) so you can see not only that you’re a target, but how an attack is progressing. KELA removes silos by centralizing dark web intelligence, technical IOCs, and global traffic data in the KELA Datalake, providing a coherent view of impending threats.
KELA Control – Providing Global Network Visibility
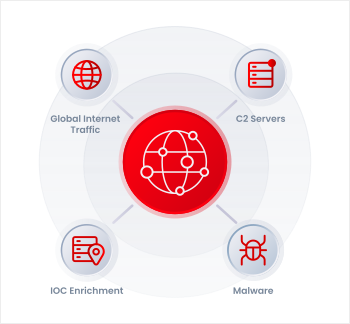
KELA Control dexpands technical visibility by monitoring global internet traffic to detect communications between your assets and malicious C2 infrastructure, while enriching every IOC with historical context, malware associations, and real-time activity patterns.
Pre-emptive Threat Hunting
KELA shifts the SOC from reactive alert clearing to proactive threat hunting by monitoring cybercrime staging areas like initial access brokers and infostealer logs for early warning. It then pairs each lead – such as leaked credentials or access-for-sale – with telemetry trails, enabling hunters to disrupt attacks during reconnaissance, before execution.
What is inside KELA’s cyber threat intelligence?
Capabilities that bridge the gap between raw signals and the actionable truth needed to stop attacks.
Automated Data Fusion
Automated Data Fusion
Every source, correlated into one intelligence view: forums, markets, messaging, infostealer logs and your own attack surface.
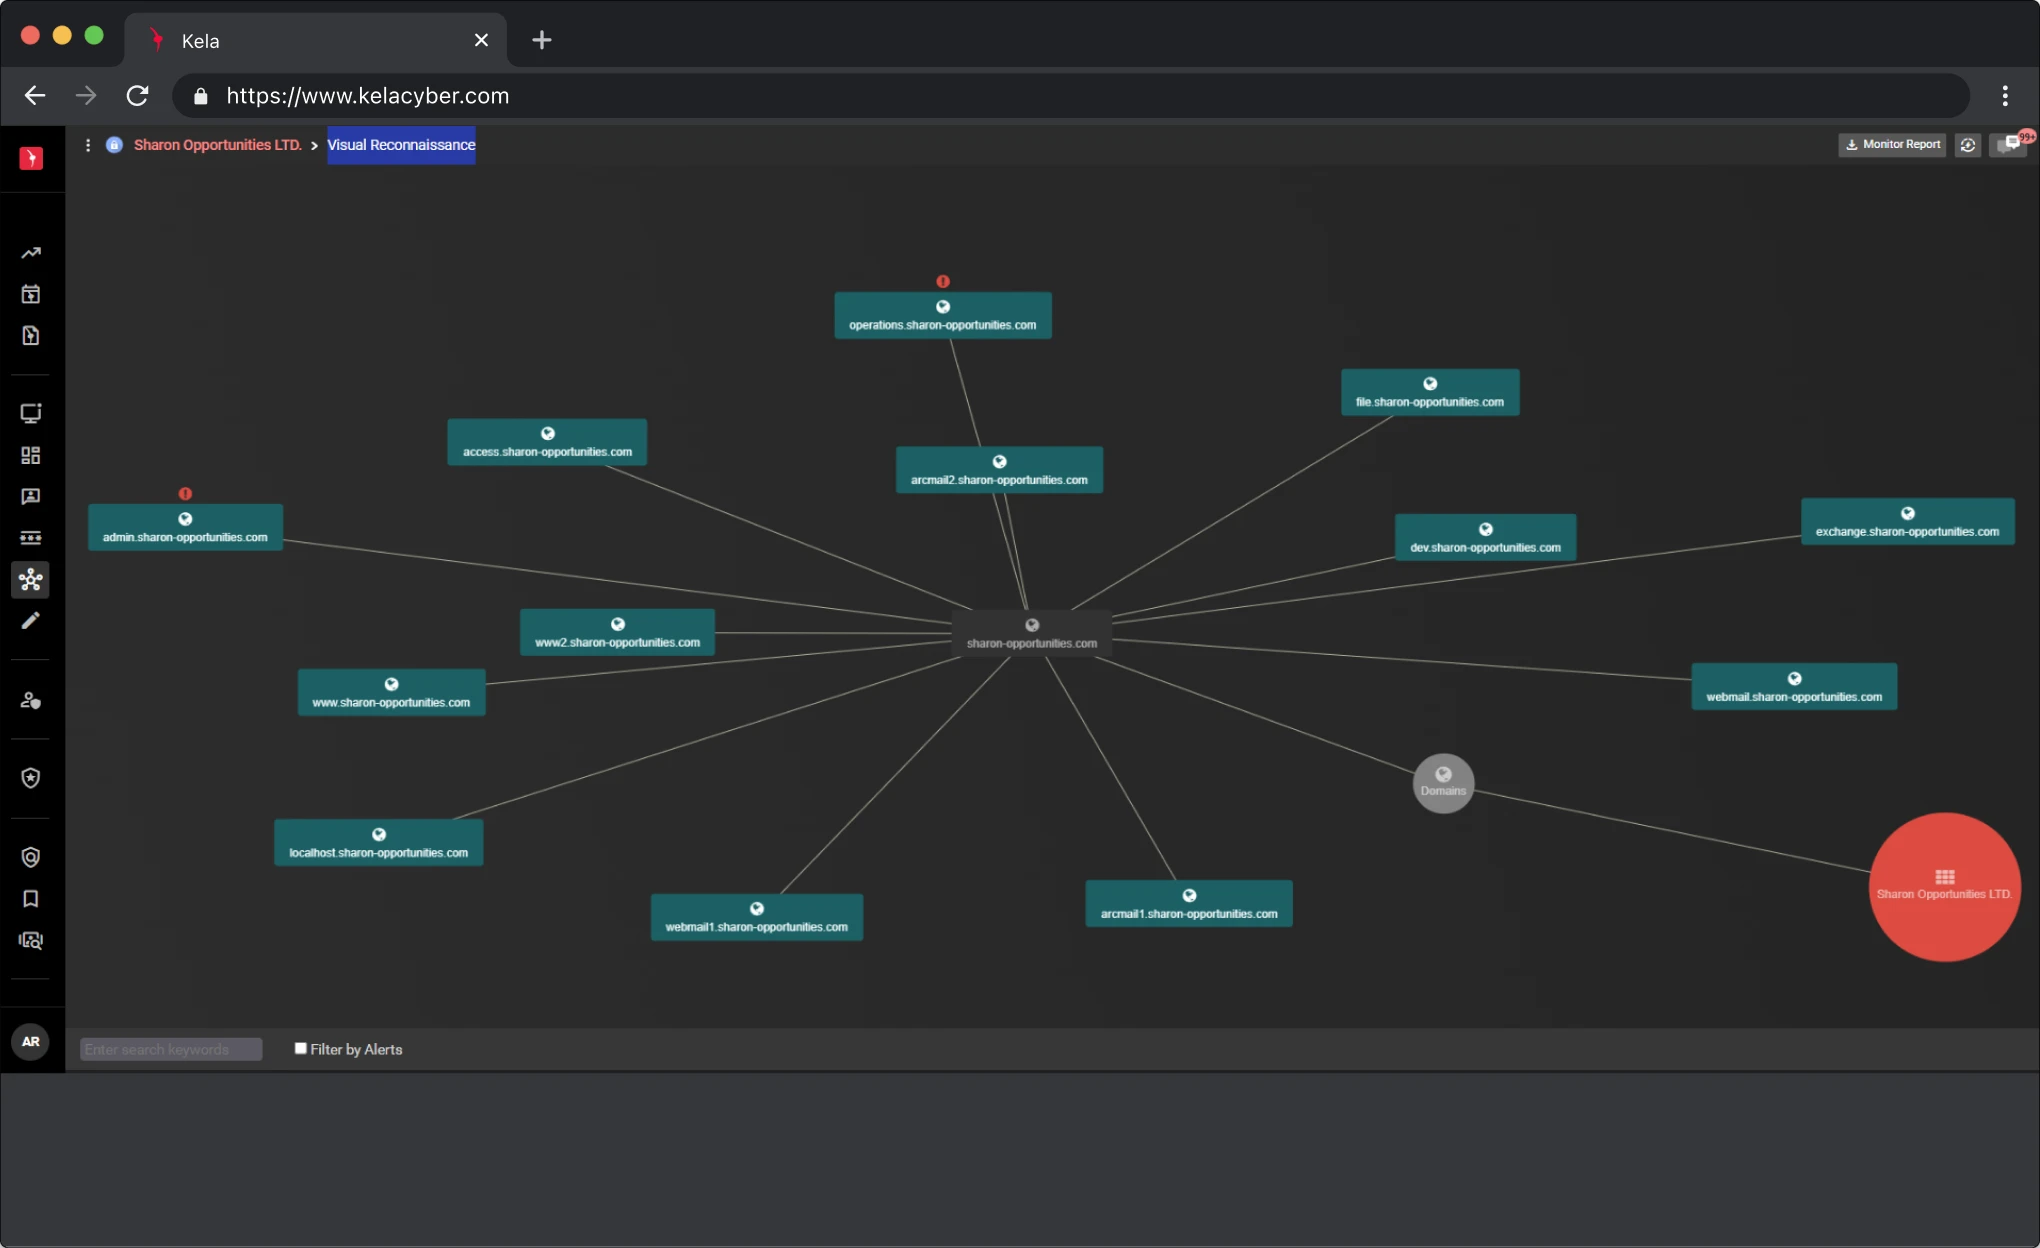
Visual Reconnaissance
Visual Reconnaissance
See your digital footprint through the eyes of an adversary to preemptively close security gaps.
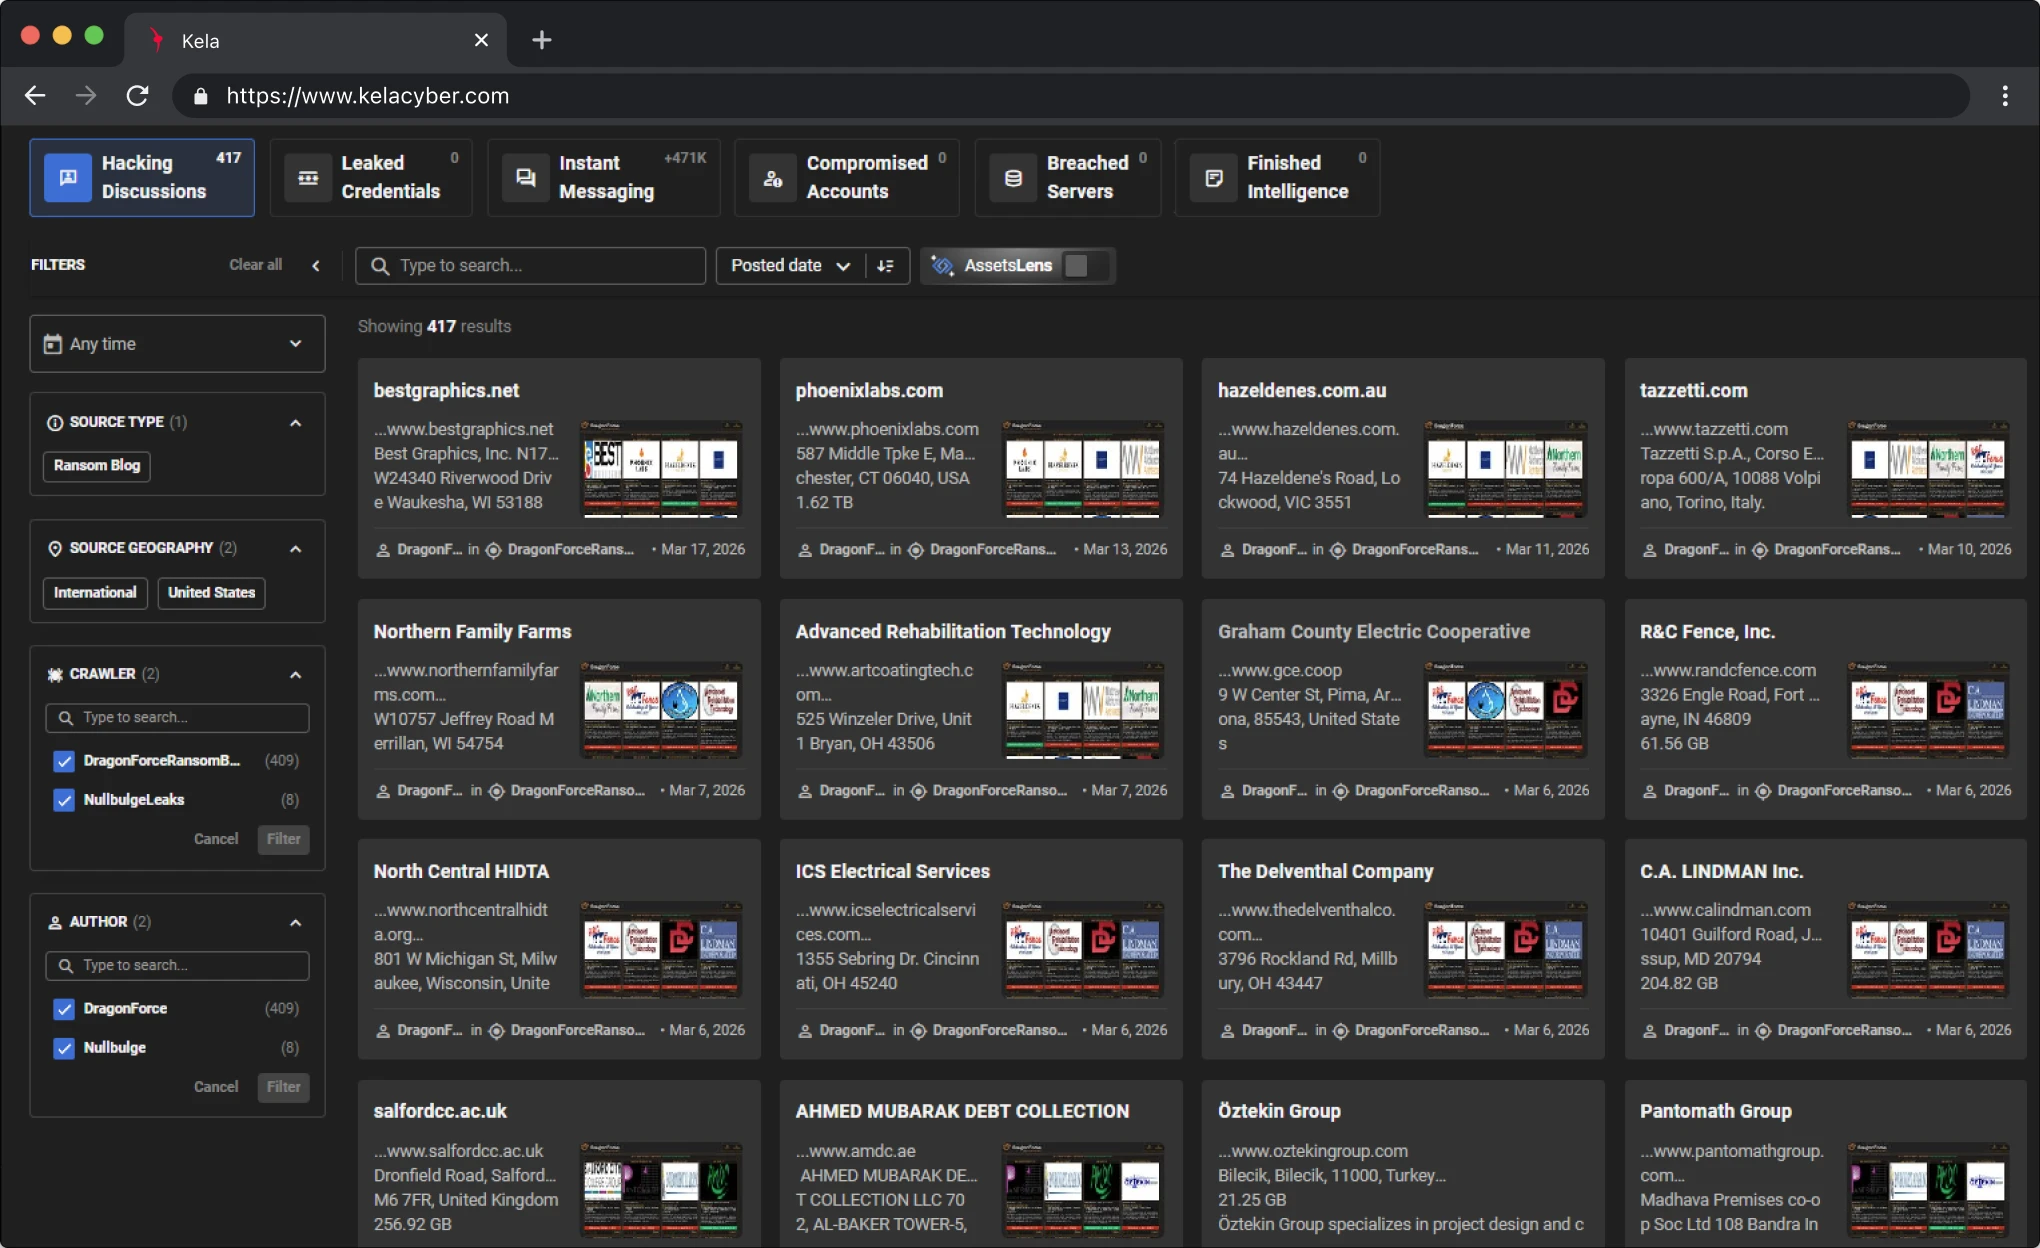
Dark Web Monitoring
Dark Web Monitoring
Identify leaked credentials and emerging threats by gaining eyes on the internet’s most hidden corners.
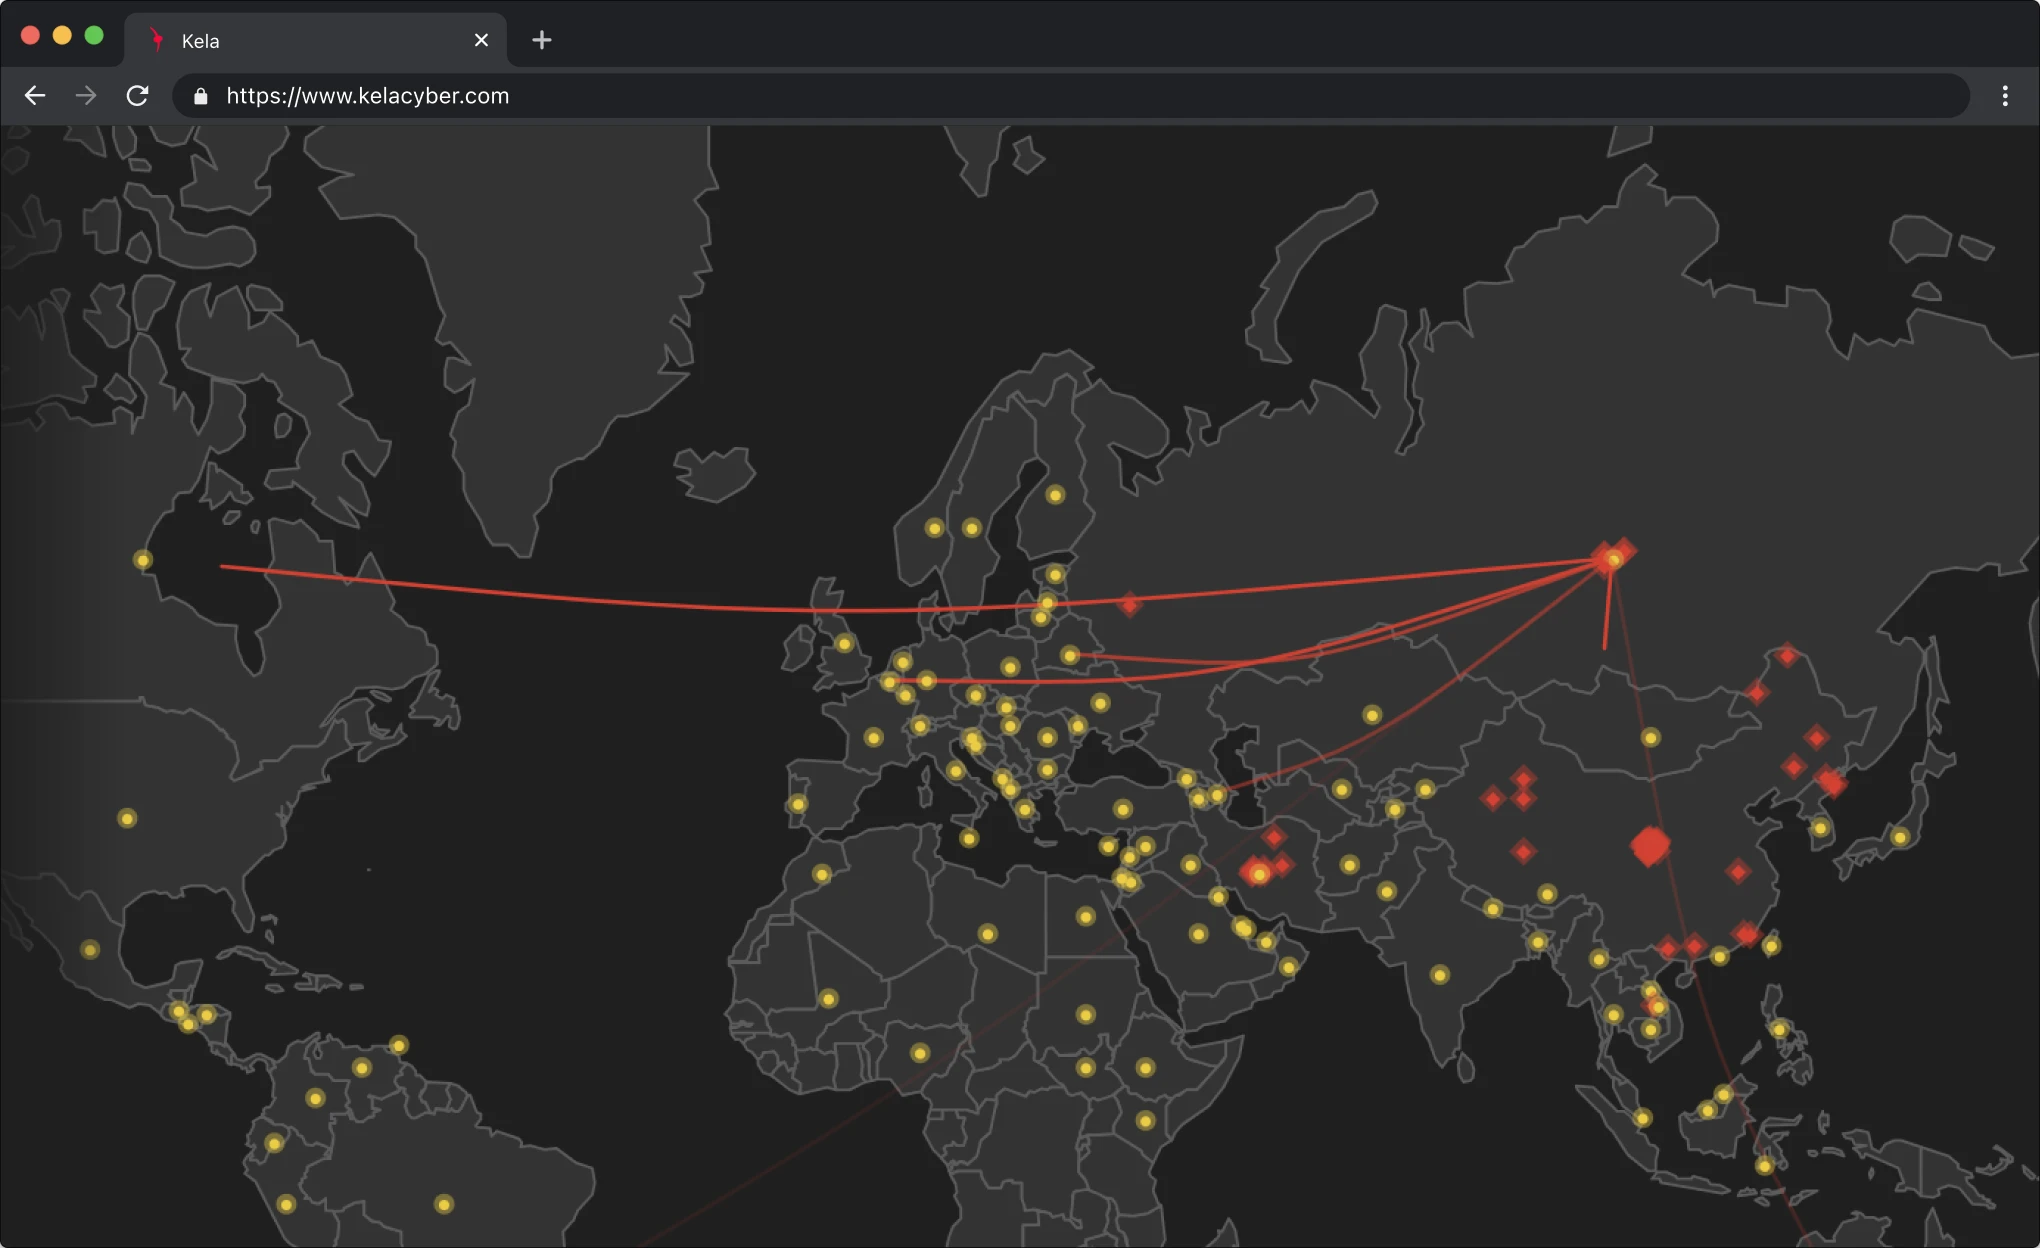
Global Netflow Monitoring
Global Netflow Monitoring
Track malicious traffic patterns and communication shifts across the global network landscape in real-time.
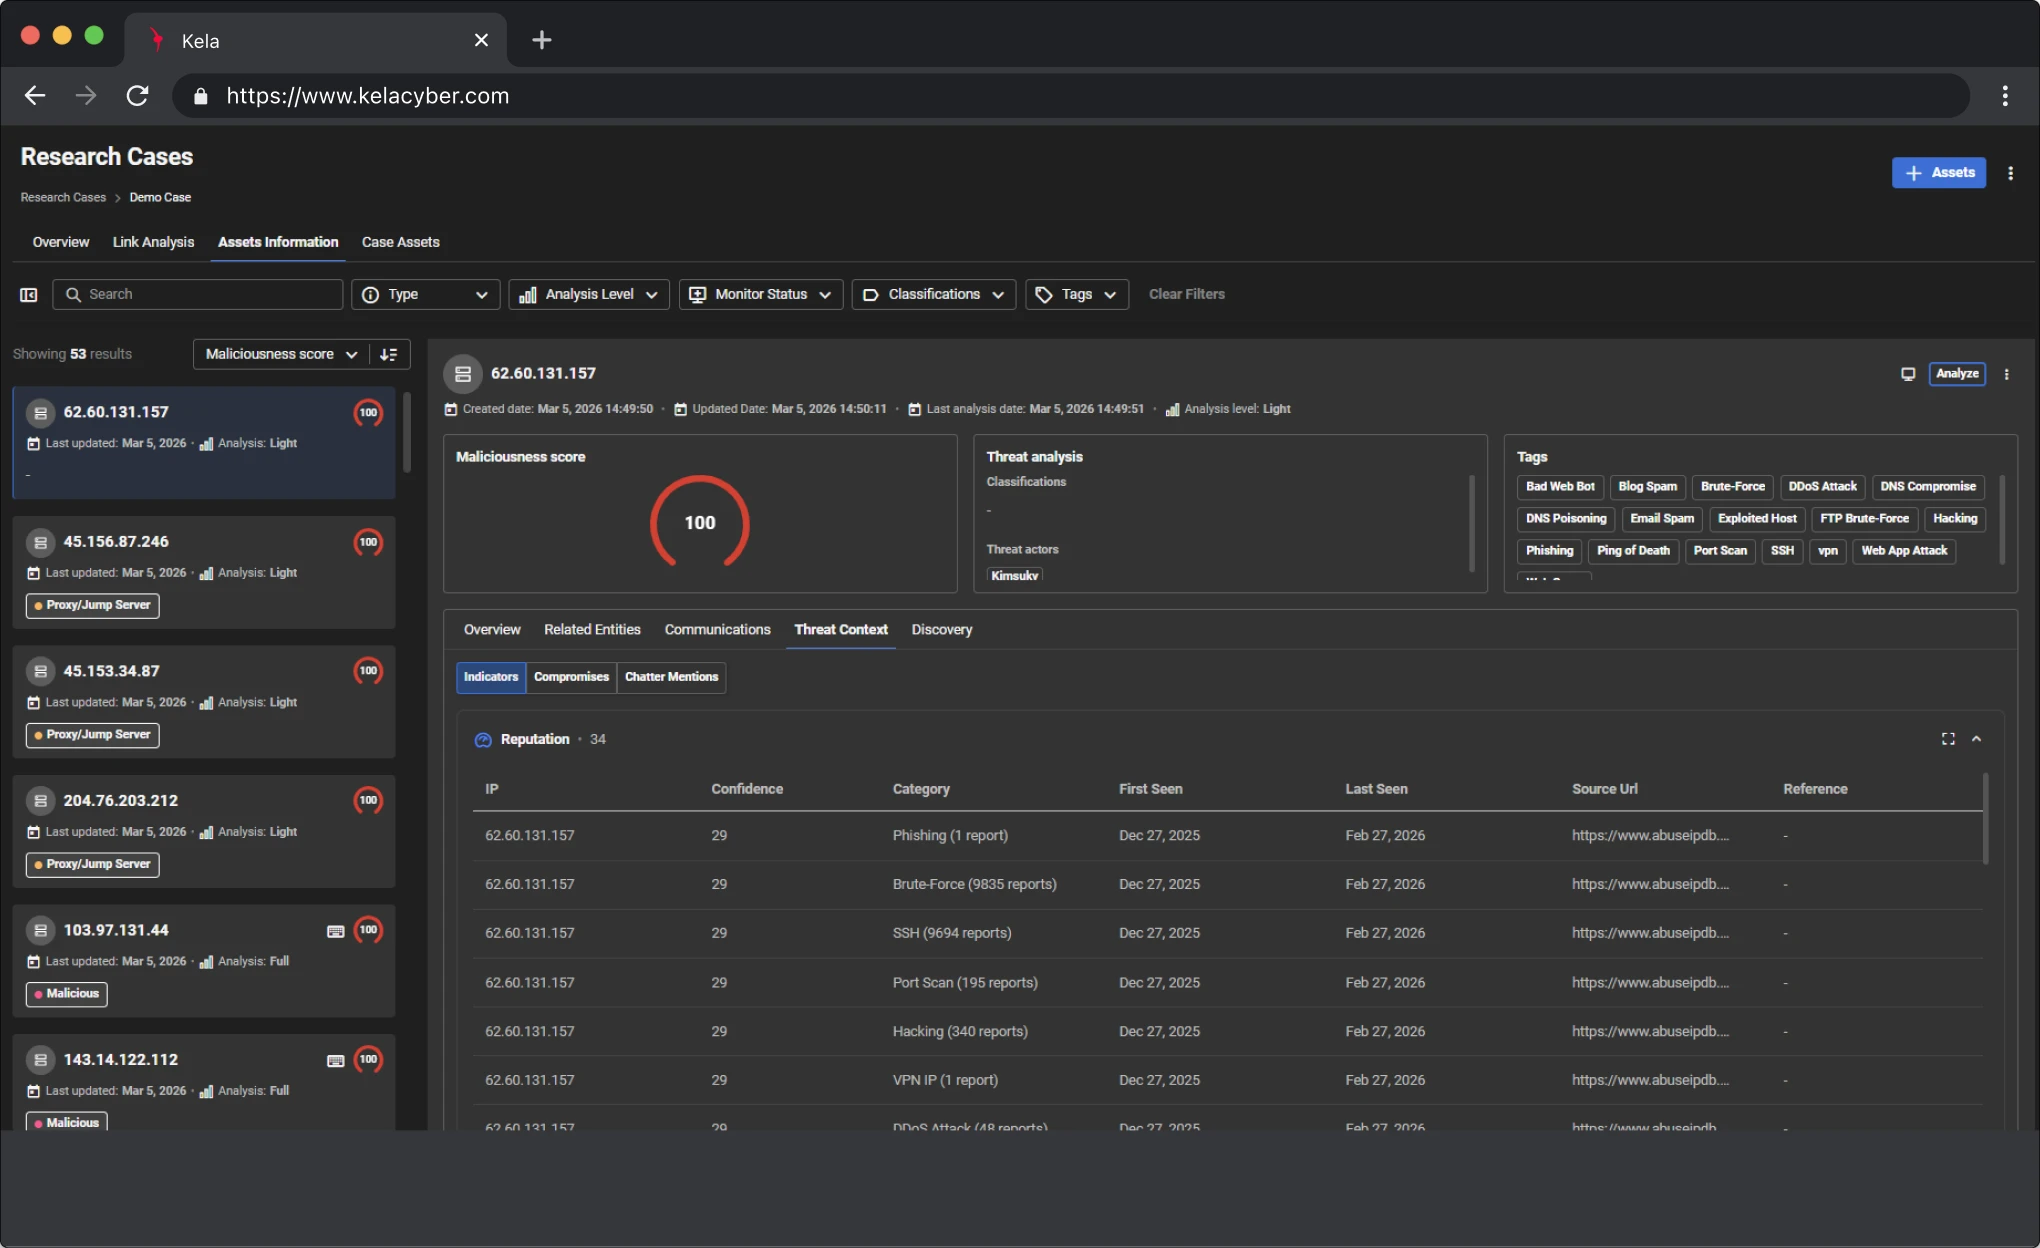
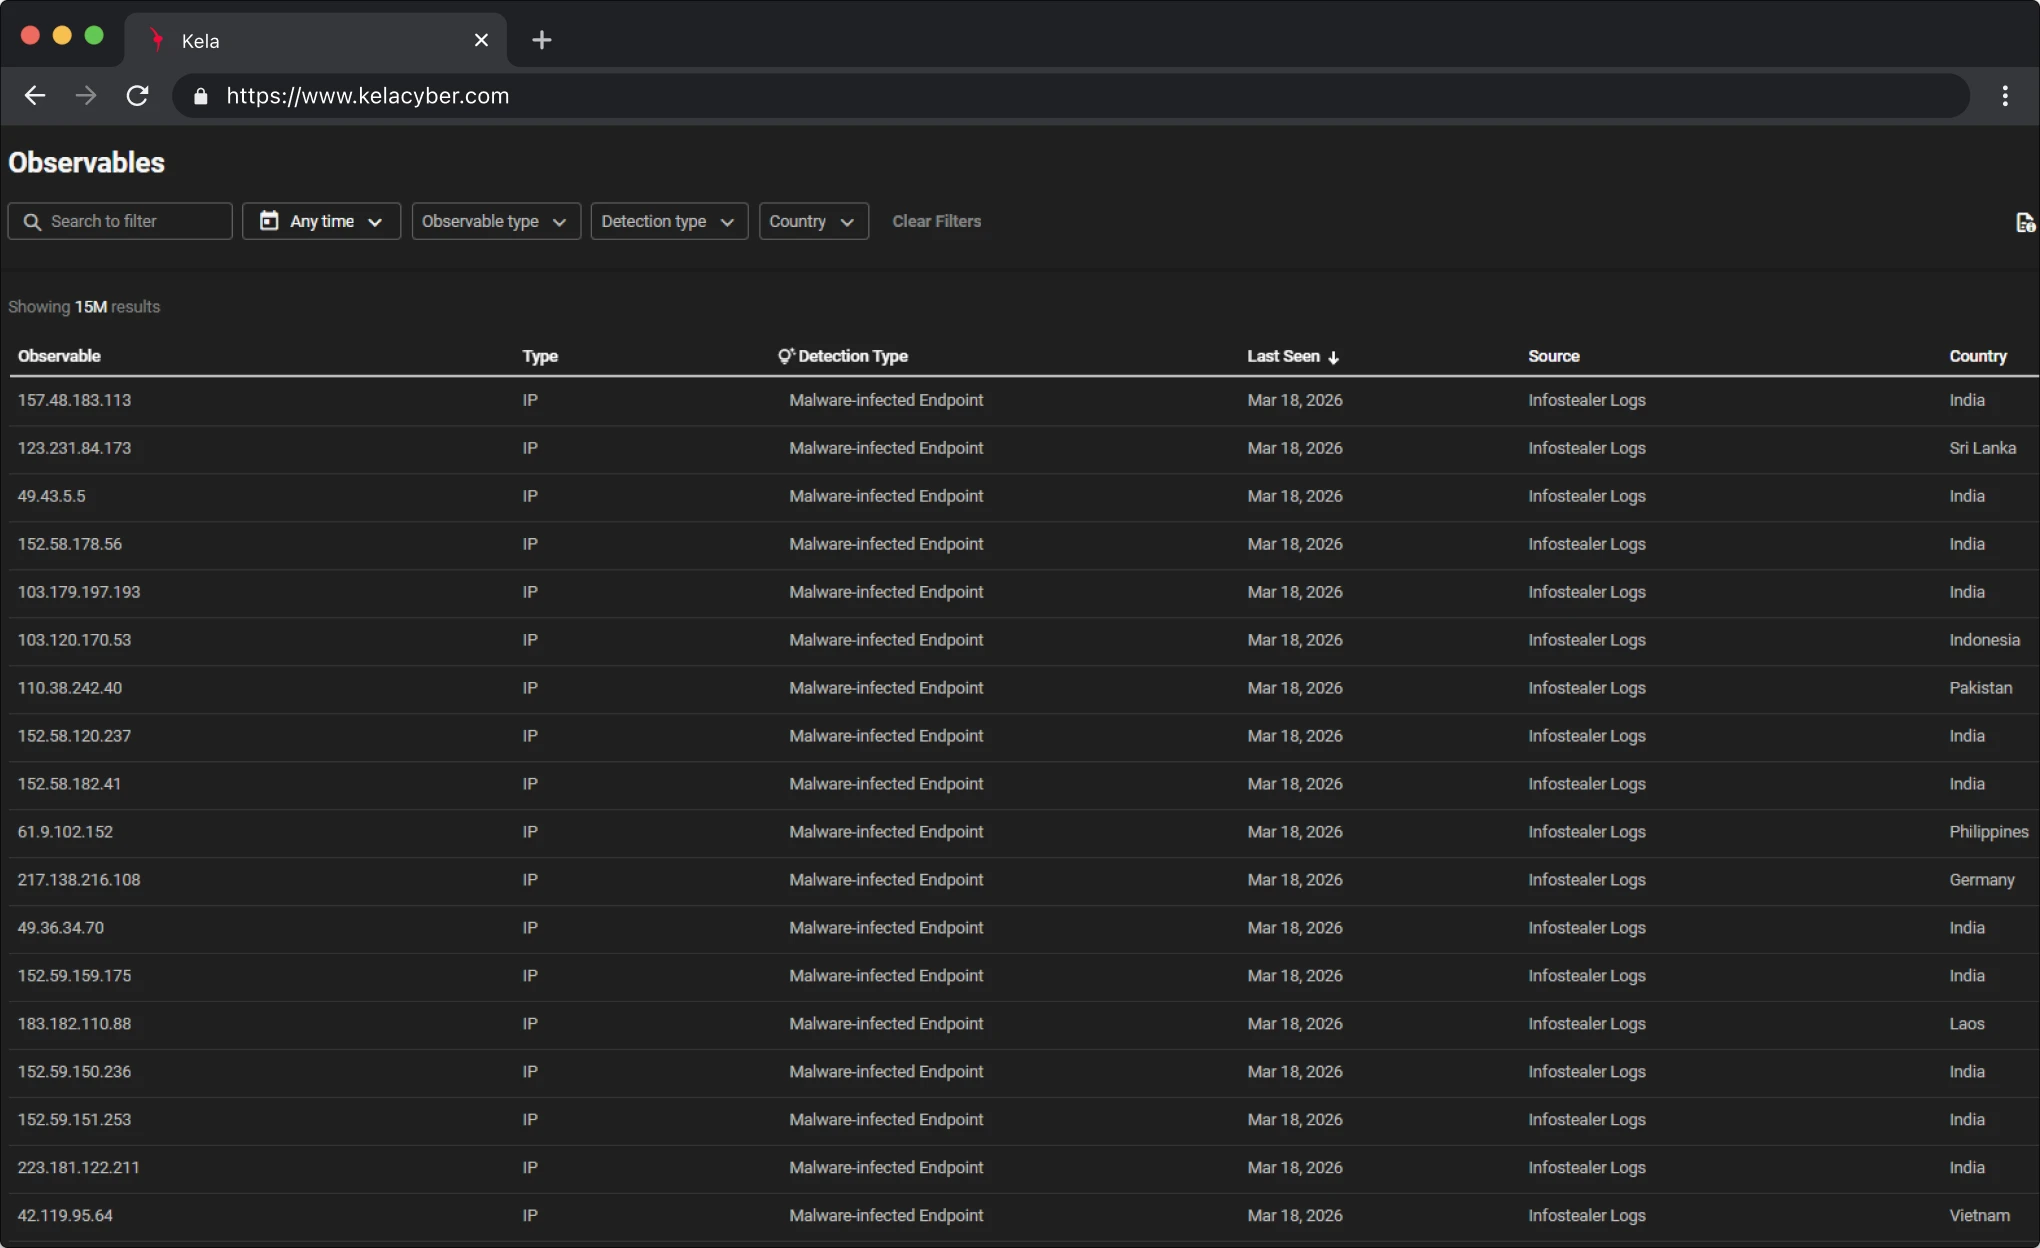
Technical Intelligence
Technical Intelligence
Access deep-dive technical indicators and to fortify your environment against threats.
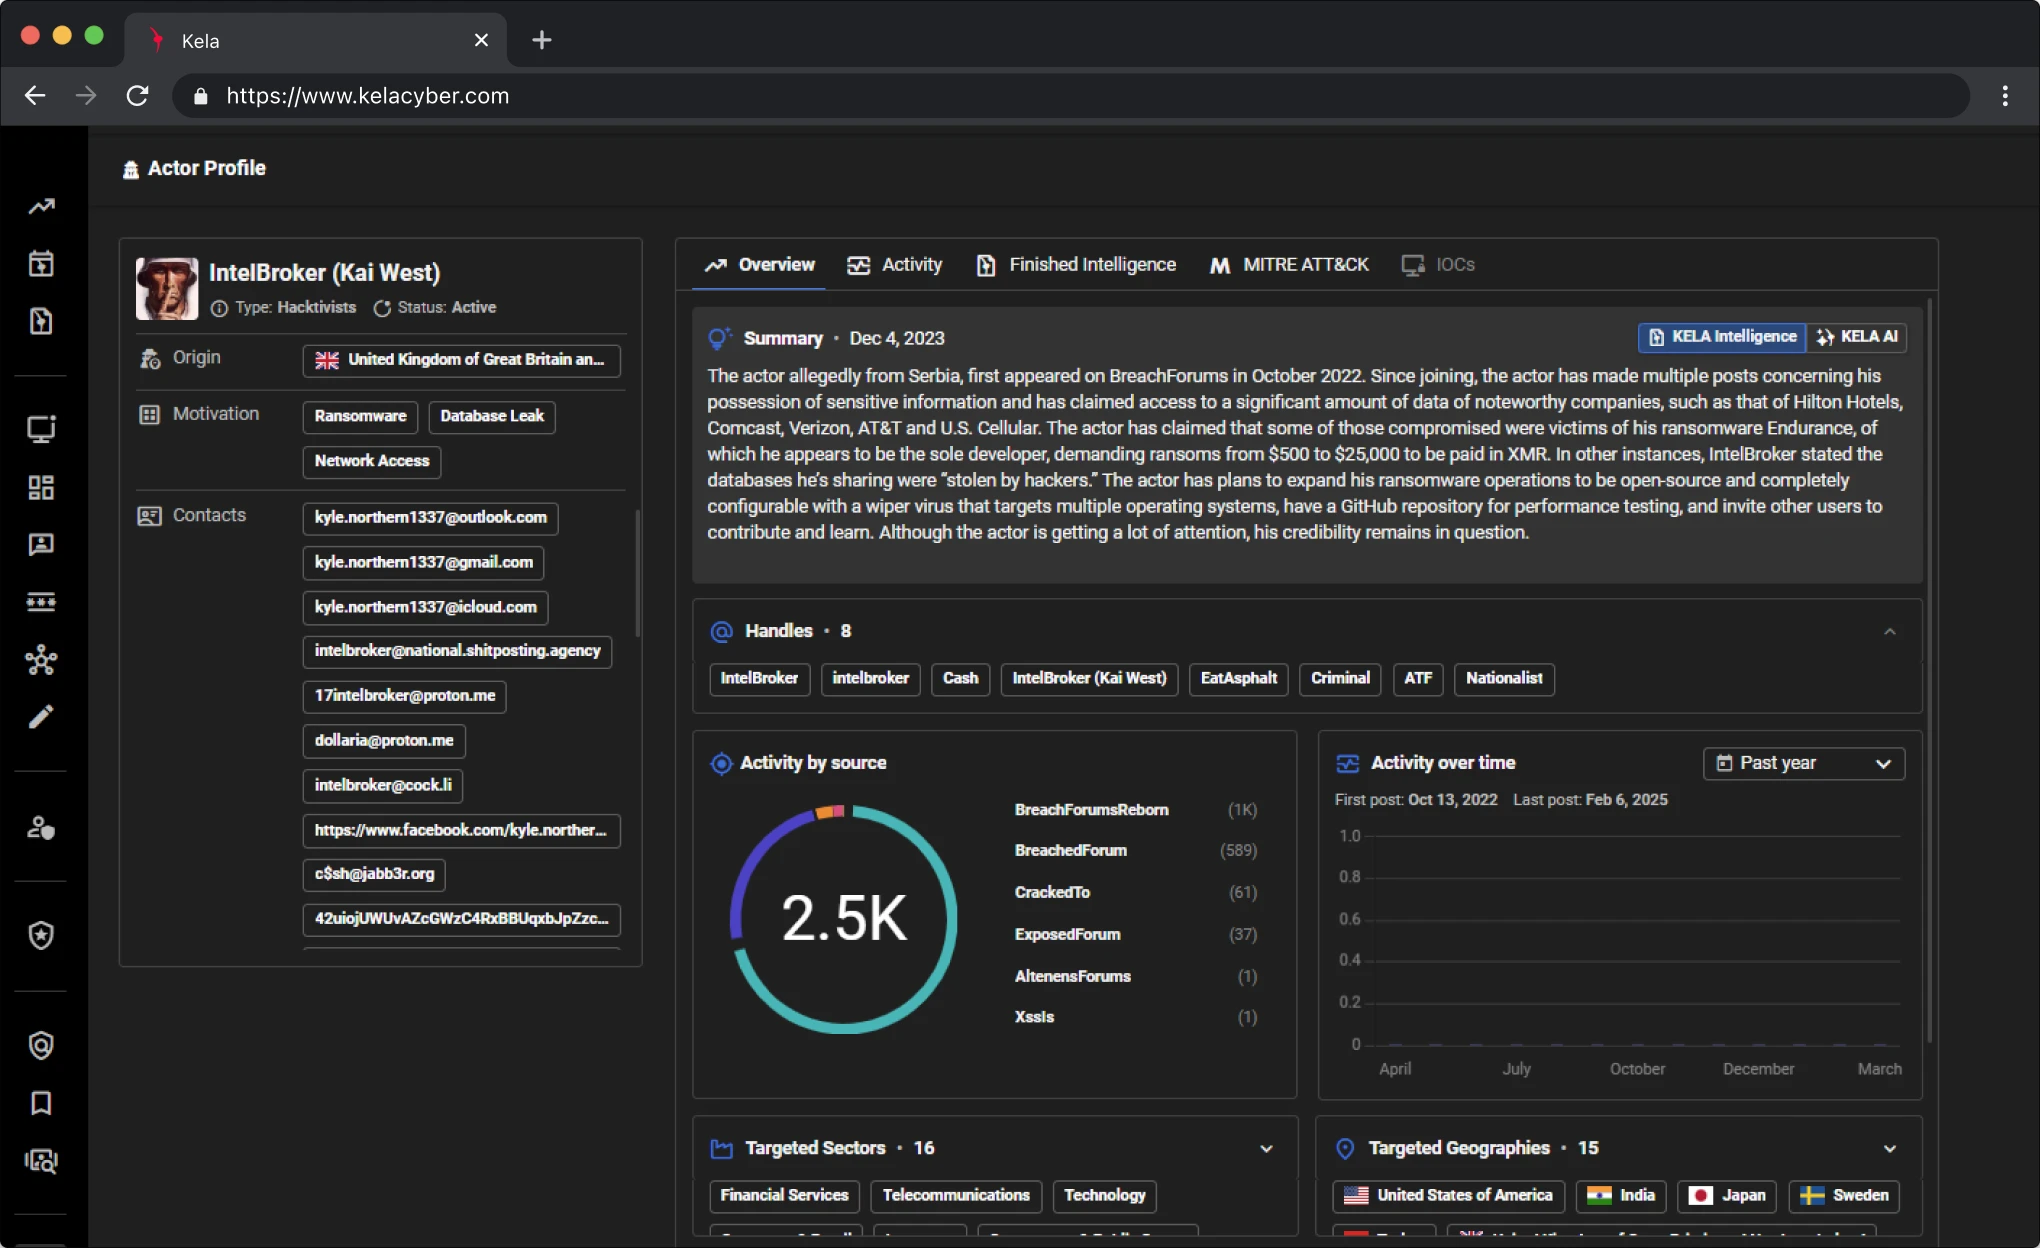
Threat Actor Profiling
Threat Actor Profiling
Understand the “who” and “why” behind attacks with comprehensive dossiers on active adversary groups.
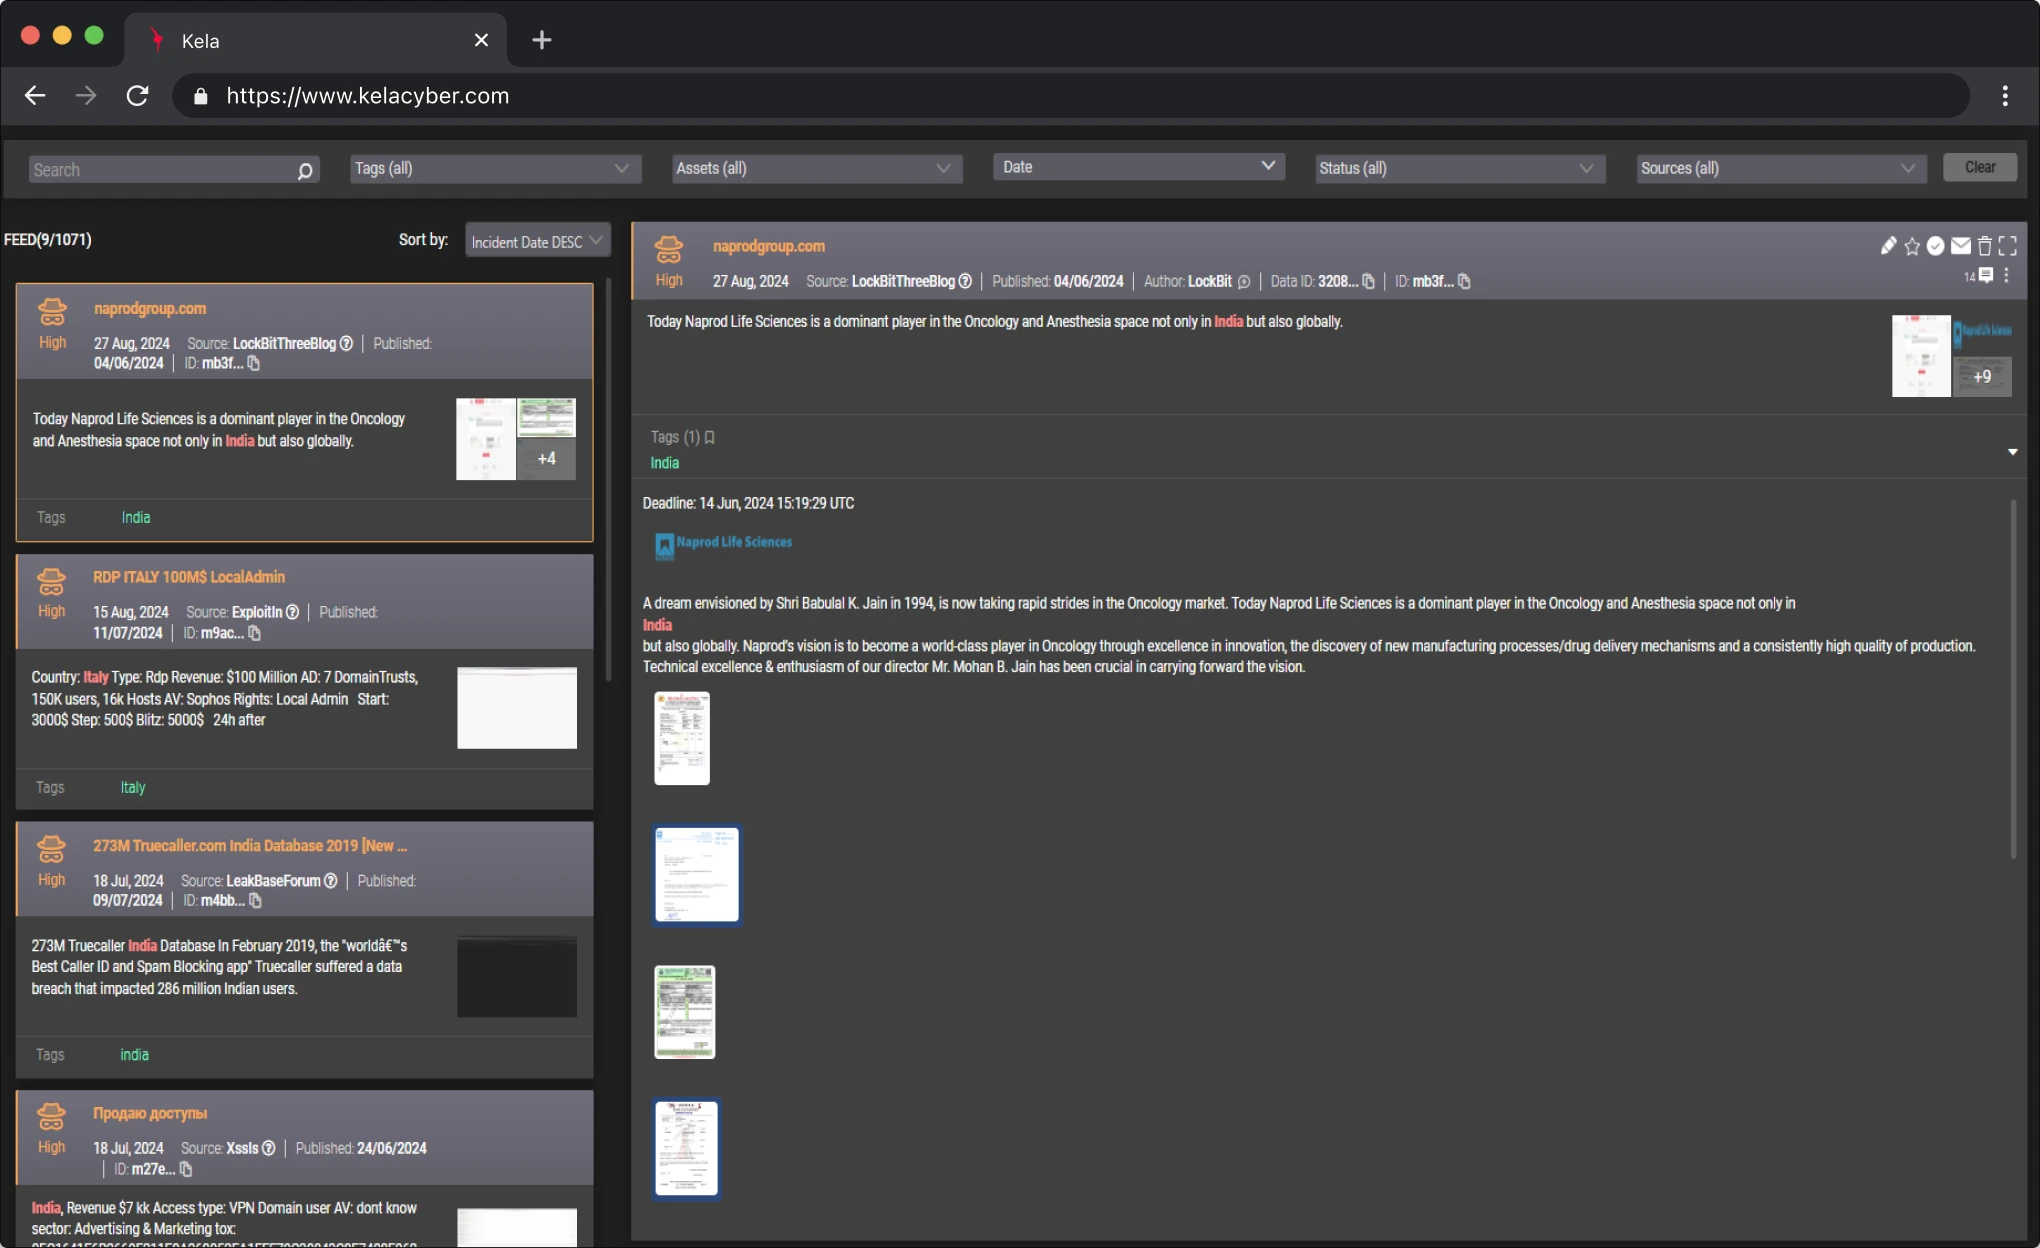
Hacking Discussions
Hacking Discussions
Stay ahead of the curve by monitoring underground forums for early chatter on new exploits and targets.
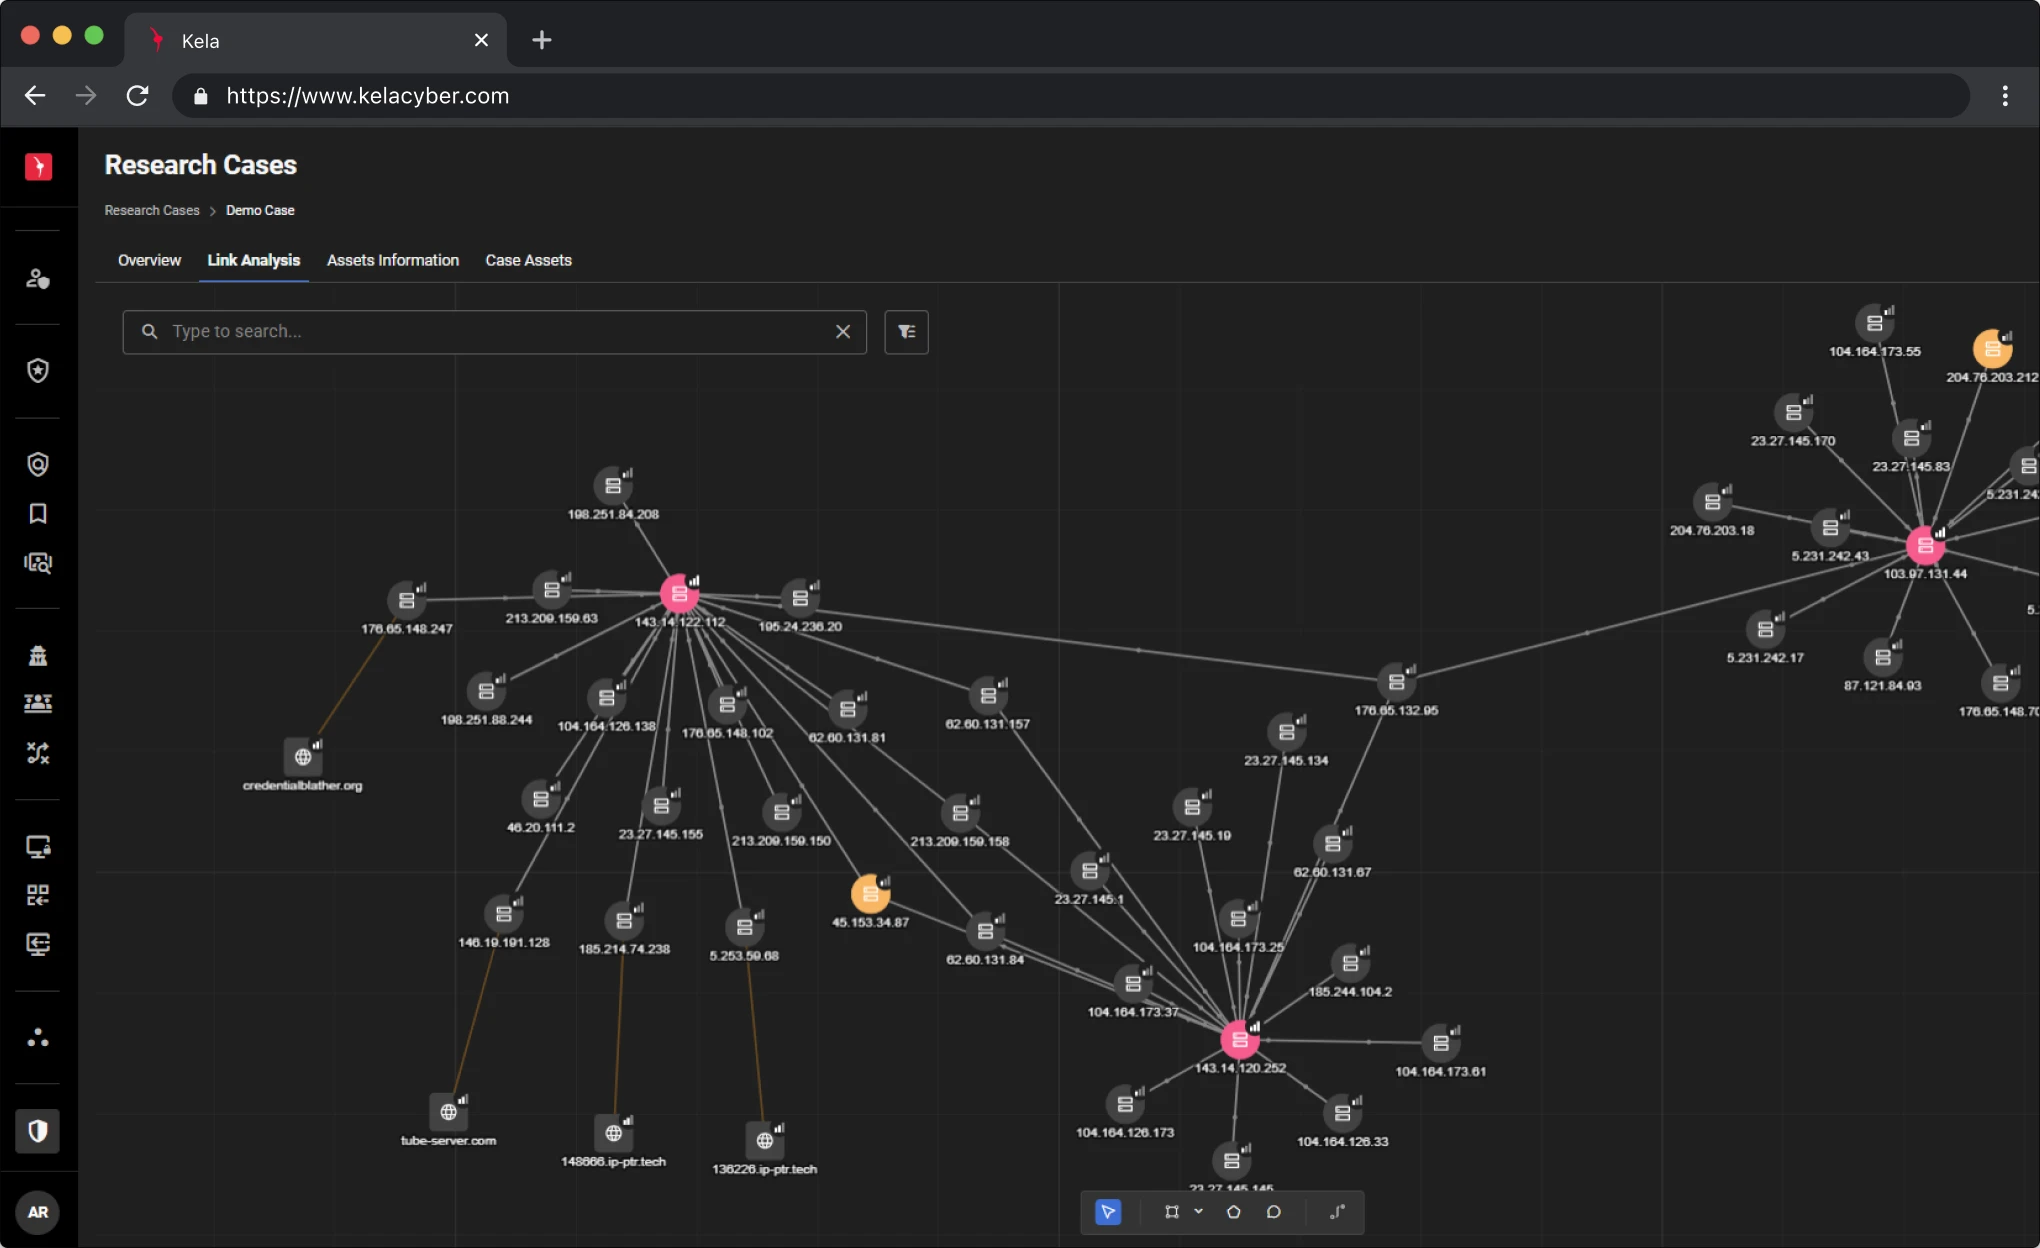
Threat Infrastructure Mapping
Threat Infrastructure Mapping
Deconstruct and track the backend servers and C2 networks used by attackers to stage their operations.
Finished Intelligence
Finished Intelligence
Receive expert-curated, strategic insights ready for immediate briefing to executive leadership.
Book a Demo
Prefer to schedule a meeting right now? Click here.
FAQ
What is cyber threat intelligence?
Cyber threat intelligence (CTI) is evidence about who is targeting you, how and when, collected from the places attacks are planned: cybercrime forums, markets, Telegram channels and infostealer logs. KELA turns that raw activity into validated, organization-specific findings with an action attached.
What sources does KELA collect from?
Closed and open cybercrime forums, illicit markets, automated shops, instant-messaging channels used by criminals, ransomware leak sites, infostealer logs and paste sites, plus global network telemetry. Collection is continuous and reaches sources most teams cannot access safely.
How is KELA different from a threat feed?
A feed hands you indicators to chase. KELA matches underground activity to your own assets, identities and vendors, enriches it with threat-actor context and severity, and tells you what to do, so analysts act on a short list instead of triaging noise.
Can analysts investigate directly in the platform?
Yes. The Investigate module is a searchable window into 20 years of underground data with the original evidence as posted, and the Threat Actors module profiles adversaries with their aliases, wallets, targets and MITRE ATT&CK techniques.
How does the intelligence reach our security stack?
Through APIs, webhooks and ready-made apps for Splunk and other SIEM and SOAR platforms, in machine-readable formats such as STIX, so findings become tickets, blocks and resets automatically.
Do we need our own analysts to use KELA?
No. Digital CTI Analysts, AI agents trained on KELA’s data, monitor sources, validate credentials, answer requests and produce briefings around the clock, and KELA’s Cyber Intelligence Center is available for deeper investigations.


