





How does KELA turn underground intelligence into action?

Discover & Collect
Map, Monitor, and Gather Intelligence
Analyze & Prioritize
Turn Data into Actionable Insights
Operationalize & Act
Integrate, Automate, and Strengthen Security
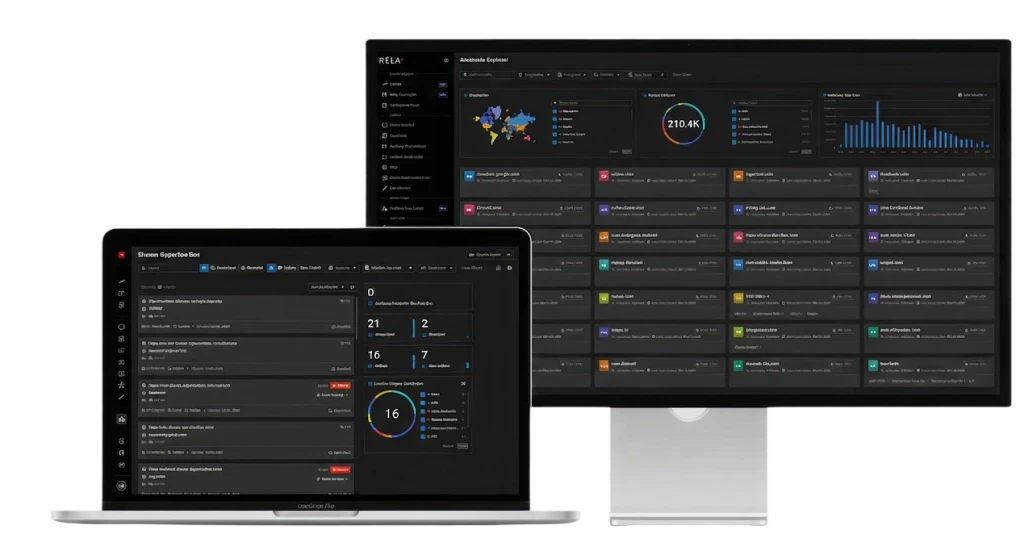
Let’s take a tour
Welcome to KELA’s Cyber Intelligence Platform
Get Started Now
The underground cybercrime, in KELA’s numbers
Compromised credentials and ransomware victims: January to August 2026 against the same period of 2025. Source: KELA data lake.
AI-Driven Digital Cyber Analysts
Built for the analysts you don’t have. Backed by intelligence you can’t get anywhere else!
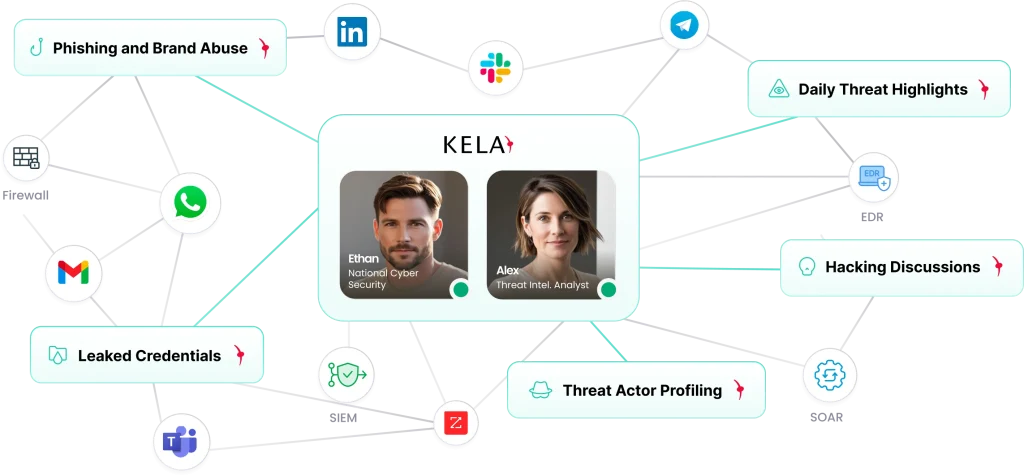

365/24/7 – Always On!
Interactive, Proactive
Fully Integrated
Solutions by threats


Solutions by industries
Why Our Customers Love Us
- Stop Real Attacks Before They Happen
- Exposure-Centric with Actionable Intelligence
- Automated and Easy to Use
Featured Content

Webinar
The TeamPCP arrests, from the inside
How KELA identified the operators behind TeamPCP and supported law enforcement, from the March supply chain cascade through…

Report
TeamPCP Threat Actor Profile
How KELA identified the man who led TeamPCP and handed law enforcement the identifier chain behind the arrest,…

Press Release
KELA research leads to alleged TeamPCP Members Arrested
KELA's Cyber Intelligence Center published the findings it shared with the AFP, WAPF and FBI in March and…
FAQ
What does KELA do?
KELA is an external threat exposure platform. It collects from an unmatched range of hard-to-reach sources, from the cybercrime underground to the open web and social media where brands and executives are impersonated, and turns what it finds into actions for your organisation: compromised credentials to reset, exposed assets and weaponised vulnerabilities to fix first, ransomware and fraud crews targeting your sector, and phishing sites and fake profiles to take down.
What is cyber threat intelligence, and how is KELA's different?
Cyber threat intelligence is knowledge about who is attacking, how, and what they are after. Most of it is built from public sources and other victims’ incidents. KELA’s comes from the attacker’s side, the hard-to-reach underground, and is matched to your own assets, people and suppliers, so it arrives as a decision about you rather than a feed about everyone.
Which threats does the KELA platform cover?
Ransomware, phishing and brand abuse, compromised credentials and infostealer infections, vulnerabilities criminals are exploiting, third-party and supply-chain risk, dark web exposure, and threats to and from AI. One platform, with the capability you need switched on.
Who uses KELA?
Enterprises, managed security providers, financial services and insurers, and government and law enforcement agencies. Inside those organisations it serves the SOC, threat intelligence analysts, vulnerability and risk teams, fraud teams, investigators and the CISO.
How do I get started?
Start for free with a domain: no agents, no setup, no card. You see your external exposure within minutes. Book a demo when you want the full platform walked through for your environment.


