





National Cyber Resilience Suite
- Strategic Threat Visibility
- Critical Sector Protection
- Cybercrime Investigations
Empowering Nations with Proactive Cyber Defense
Governments and law enforcement face increasingly sophisticated cyber threats that jeopardize national security. KELA’s National Cyber Resilience Suite provides the intelligence-driven tools needed to detect, analyze, and defend against nation-state actors and cybercriminals. Powered by KELA’s proprietary data lake and AI-driven analysis, the suite delivers real-time insights and advanced investigative capabilities to safeguard critical sectors and national assets.

National Threat Visibility
Real-time monitoring to swiftly detect and mitigate national-level cyber risks.

Securing Key Infrastructure
Proactive defense to protect critical sectors from evolving cyber threats.

Investigative Intelligence
Actionable insights to accelerate law enforcement efforts in disrupting cybercrime.
Comprehensive Suite – Modular
Deployment
Get Started for Free
Fortify Your National Defenses
Governments and law enforcement face increasingly sophisticated cyber threats that jeopardize national security. KELA’s National Cyber Resilience Suite provides the intelligence-driven tools needed to detect, analyze, and defend against nation-state actors and cybercriminals. Powered by KELA’s proprietary data lake and AI-driven analysis, the suite delivers real-time insights and advanced investigative capabilities to safeguard critical sectors and national assets.
National Threat Infrastructure Mapping
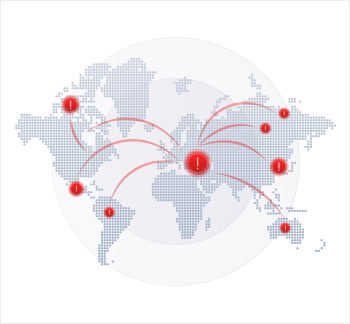
KELA’s suite provides comprehensive visibility into national-level cyber threats by mapping and analyzing malicious infrastructure, including C2 servers, botnets, and VPNs. With advanced detection capabilities, it allows governments to quickly identify, track, and mitigate threats targeting critical assets, ensuring proactive defense against evolving cyber risks.
Securing critical Sectors
KELA safeguards critical national sectors with real-time insights into compromised accounts and emerging threats. Drawing on massive visibility into compromised accounts across companies and industries, governments can monitor, analyze, and proactively defend key infrastructures like energy, healthcare, and transportation.
Empowering Cyber Investigations
KELA gives law enforcement real-time, anonymous access to underground cybercrime activity. With deep threat actor insights and continuous monitoring, agencies can track criminals, uncover hidden networks, and act decisively to disrupt cyber threats.
Featured Content

Webinar
The TeamPCP arrests, from the inside
How KELA identified the operators behind TeamPCP and supported law enforcement, from the March supply chain cascade through…

Report
TeamPCP Threat Actor Profile
How KELA identified the man who led TeamPCP and handed law enforcement the identifier chain behind the arrest,…

Press Release
KELA research leads to alleged TeamPCP Members Arrested
KELA's Cyber Intelligence Center published the findings it shared with the AFP, WAPF and FBI in March and…
FAQ
What is the National Cyber Resilience Suite?
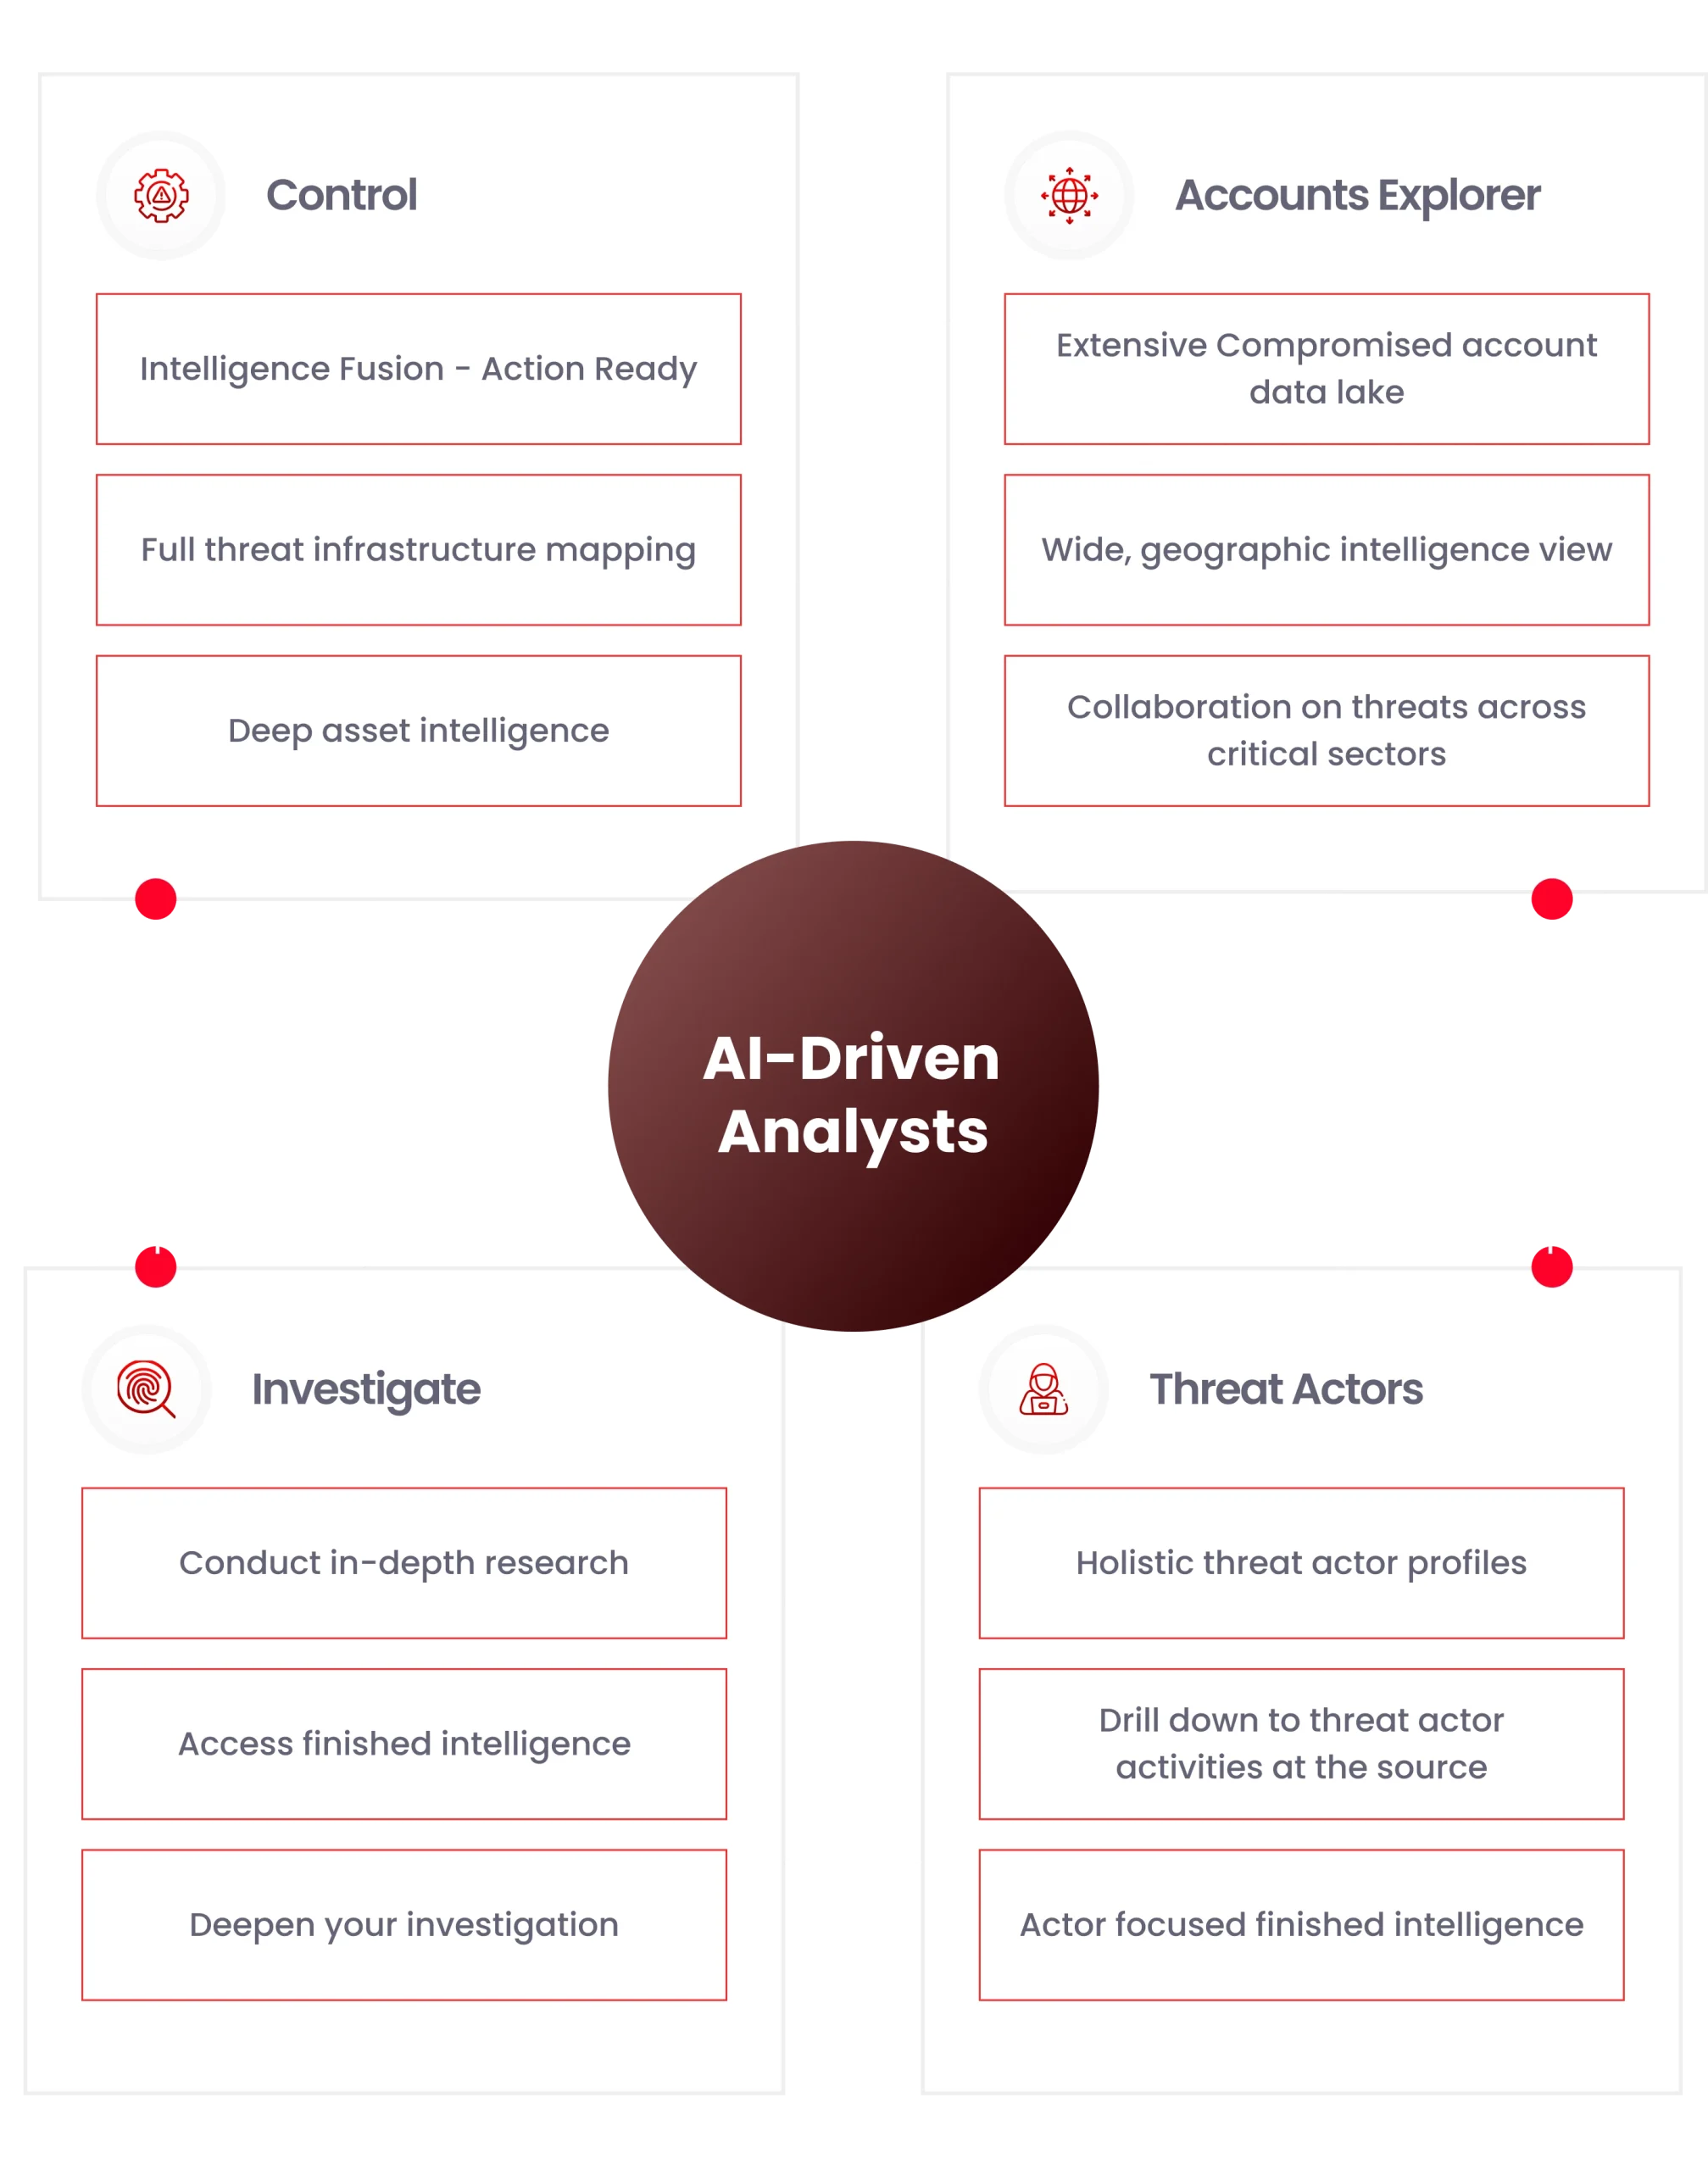
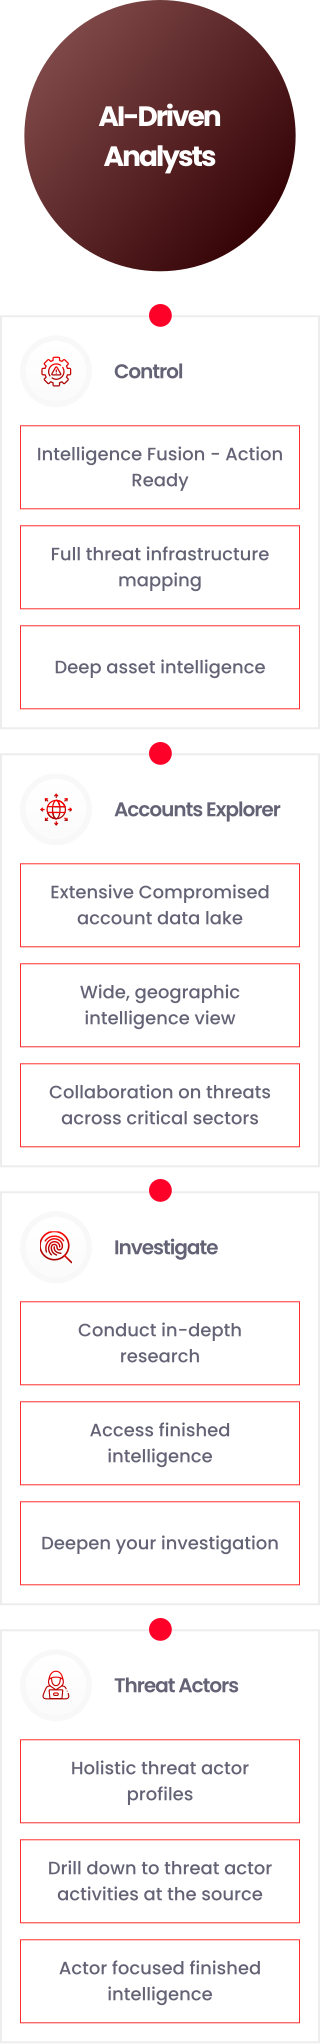
A set of KELA modules for governments, CERTs and law enforcement: nationwide visibility of compromised accounts and infected machines, attacker infrastructure mapping, and cybercrime investigation tools.
How does a national CERT see infections across the country?
Accounts Explorer aggregates KELA’s compromised-accounts data lake by region, domain and subnet, with drill-down to individual machines, so agencies can warn critical infrastructure operators early.
Can investigators map attacker infrastructure from a single indicator?
Yes. KELA Control starts from one IP or domain and uncovers connected command-and-control servers, proxies and botnets using netflow-based intelligence, shown as a visual graph of control paths.
Is the evidence traceable?
Findings link to the original source material exactly as it appeared in the underground, with timestamps and provenance, so cases are built on verifiable evidence.
How is analyst access secured?
Analysts work through an isolated environment and never touch cybercrime sources directly. Access is role-based and auditable.


