





Enterprise-Grade Cyber Intelligence
- Actionable Insights
- Minimized Risk
- Brand Integrity
Enterprise Threat Intelligence Solutions
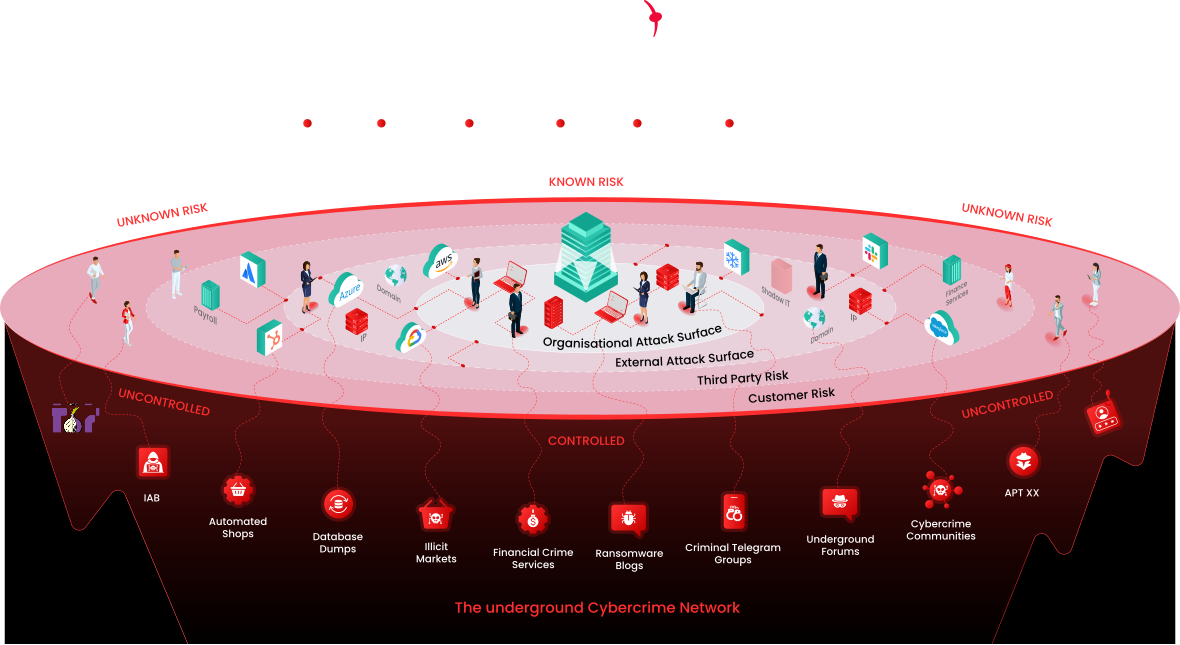
Modern enterprises operate in an environment where digital risk is constant, fast-moving, and increasingly targeted. From data leaks to ransomware and supply chain threats, organizations need intelligence that goes beyond generic alerts. KELA provides real-time, contextual threat intelligence to help security teams reduce risk, protect brand reputation, and stay ahead of cybercriminals operating across the deep, dark, and clear web.

Ransomware protection
KELA helps eliminate the #1 cause of cyber attacks and intercepts compromised employee identities from hundreds of millions of compromised credentials, in real-time.

Phishing and brand protection at scale
Detect exposed corporate assets, employee credentials, and customer data to prevent misuse and reputational harm.

Supply chain and third-party risk monitoring
Uncover vulnerabilities, leaks, and threats related to vendors and partners—before attackers exploit them.

KELA provides tailored intelligence for faster decision-making and equips your SOC, IR, and CTI teams with contextual, prioritized insights to act swiftly and confidently.
Learn how a global telecom company leveraged KELA’s real-time monitoring to identify a third-party data leak and prevent a breach.
Get Started for Free
Featured Content

Webinar
The TeamPCP arrests, from the inside
How KELA identified the operators behind TeamPCP and supported law enforcement, from the March supply chain cascade through…

Report
TeamPCP Threat Actor Profile
How KELA identified the man who led TeamPCP and handed law enforcement the identifier chain behind the arrest,…

Press Release
KELA research leads to alleged TeamPCP Members Arrested
KELA's Cyber Intelligence Center published the findings it shared with the AFP, WAPF and FBI in March and…
FAQ
What does an enterprise get from KELA that a generic threat feed does not?
Intelligence tied to your own assets: your leaked credentials, your infected devices, access to your network offered for sale, your brand inside phishing kits. Not indicators to sift through, but validated exposure with an action attached.
How does KELA reduce alert noise?
Every finding is matched to your assets and enriched with threat-actor context and severity, so teams receive a short, prioritized list instead of a stream of generic alerts.
Which security tools does KELA integrate with?
SIEM and SOAR platforms, including the KELA apps for Splunk, plus ticketing and identity systems through API and webhooks, so findings become tickets and remediation can run automatically.
Can KELA cover subsidiaries and the supply chain?
Yes. Multi-tenant monitoring covers subsidiaries and business units, and the Third-Party Risk Management module scores and monitors vendors from the attacker’s perspective.
How does the platform use AI?
Digital CTI Analysts, AI agents trained on KELA’s data, monitor sources, validate credentials, answer requests and produce briefings around the clock as an extension of your team.


