


Phishing infrastructure research
Is your bank being impersonated?
KELA is tracking a phishing network that impersonates more than 180 US financial institutions and shows a fake “account suspended” page to anyone who might report it. Enter your bank’s official domain or name to see if it is among them.
From the KELA research Not Actually Suspended: How a Bank-Phishing Network Fakes Its Own Takedown
What the campaign looks like
One naming recipe
Almost every domain is an urgency keyword such as secure, disable, protect or cancel, a hyphen and the bank’s name, under .com.
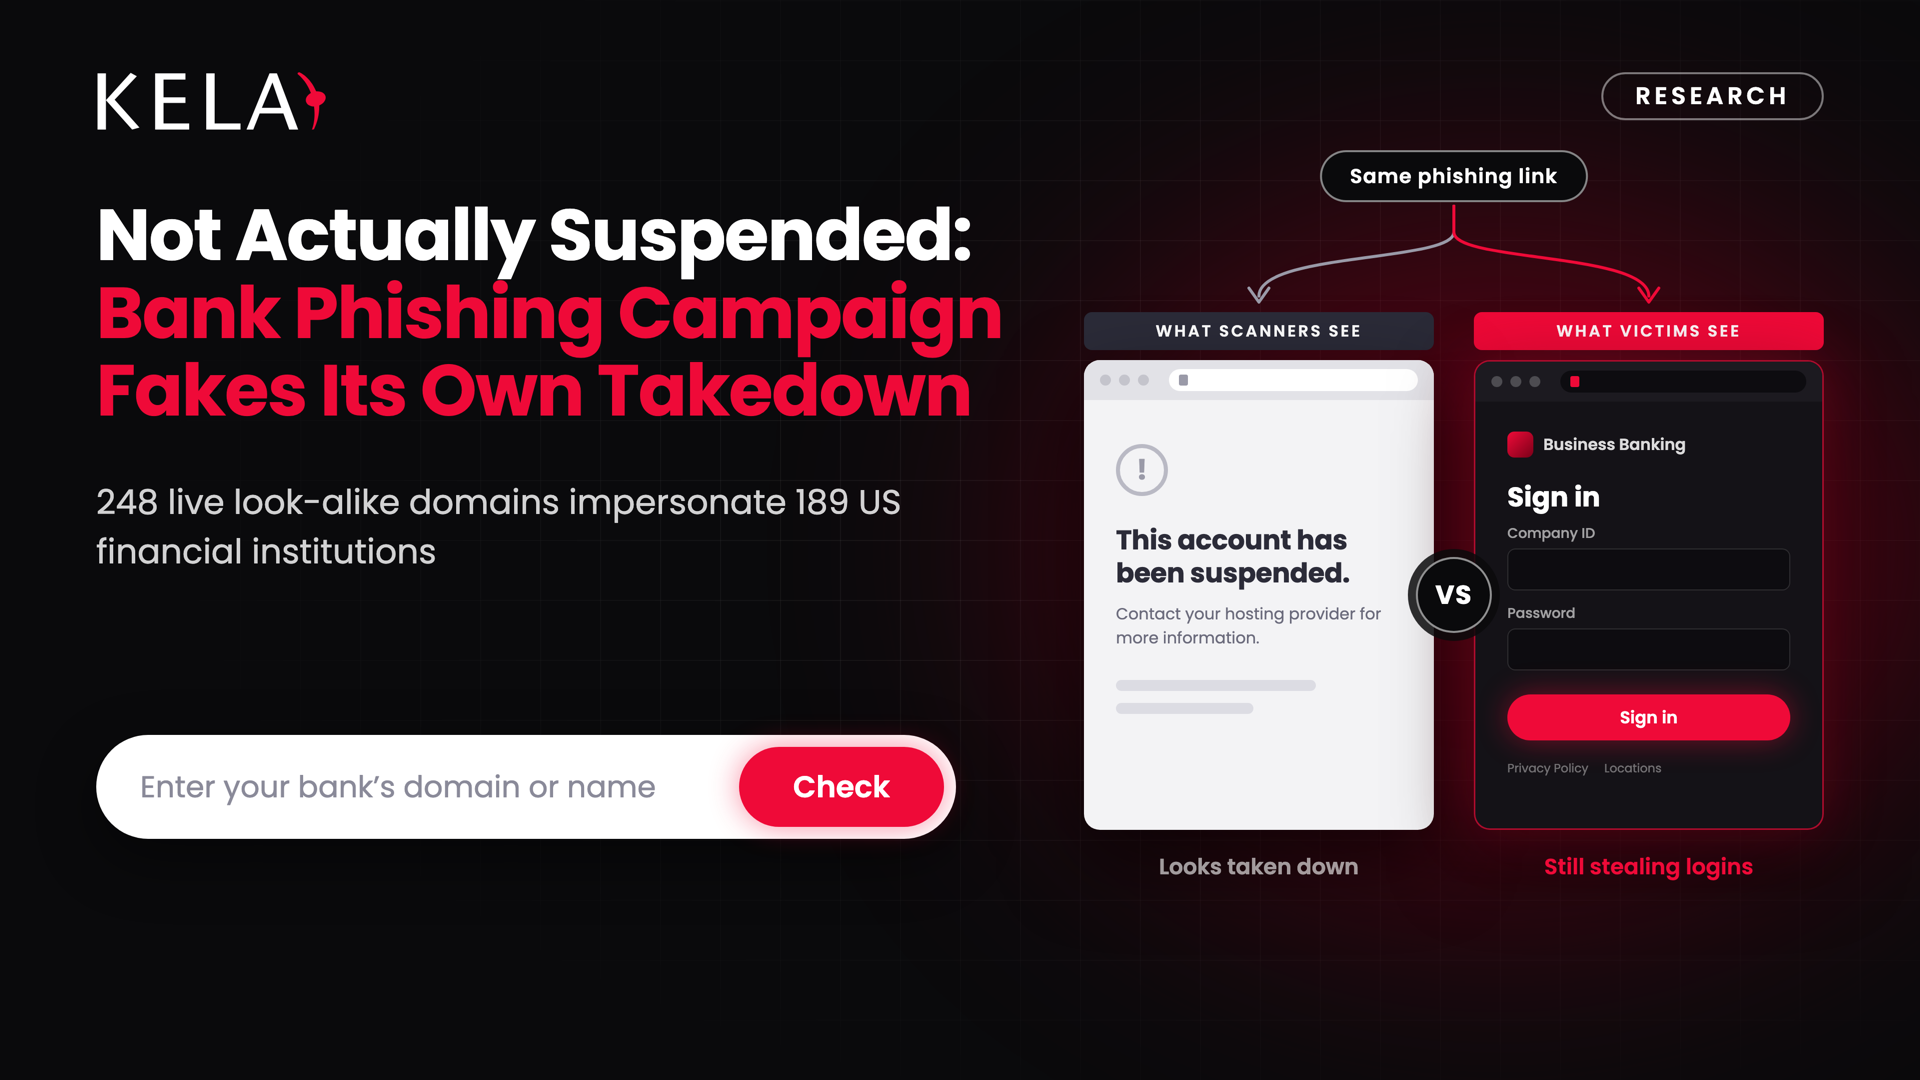
A fake takedown
Scanners and researchers see an “account suspended” page while victims still reach the fake login, so a live domain can pass for one that was taken down.
Hidden hosting
Every domain sits behind Cloudflare, which hides the real servers. Taking down one domain leaves the rest of the network untouched.
What to do if your bank is on the list
The look-alike domains are already live, and new ones follow the same recipe, so act on both the current domains and the next wave.
- Watch newly registered domains for secure, disable, protect, cancel, authorize or terminate, a hyphen and your bank’s name under .com, and confirm each one by its page behavior.
- Don’t clear a domain on one visit: a “suspended” page doesn’t mean it is inactive. Check again over time and from different locations.
- Warn business-banking customers that urgent messages about a cancelled transaction or a disabled account are a red flag, and confirm payment changes by phone.
- Report each domain to the registrar and to Cloudflare, then confirm the phishing page actually stopped. A provider that only sees the fake “suspended” page may close the report.
- Talk to KELA: we can share the look-alike domains we see for your bank and keep watching for new ones.


