





DATASHEET
KELA THREAT ACTORS
Stay ahead of adversaries with real-time intelligence and unified threat actor personas.
Share:
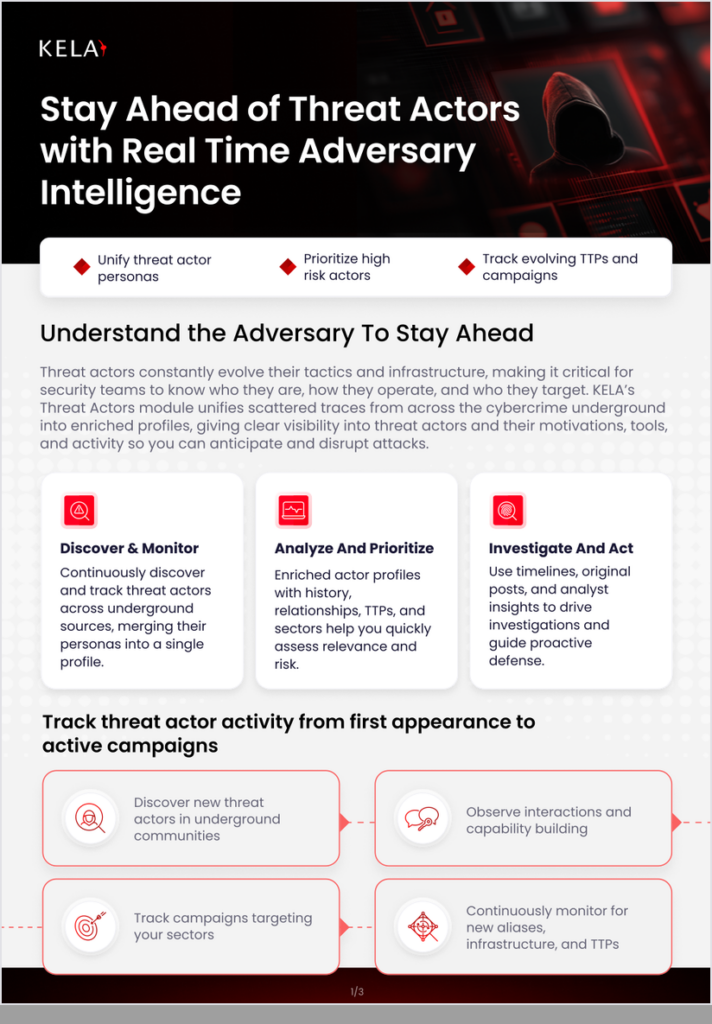
Threat actors constantly change their tactics, aliases and infrastructure. KELA’s Threat Actors module unifies scattered traces from across the cybercrime underground, from forum handles to contacts and crypto wallets, into enriched profiles that show who stands behind a campaign, how they operate and whom they target.
Drawing on the industry’s largest threat actor database, profiles highlight activity history, preferred TTPs mapped to MITRE ATT&CK, target sectors and links to related actors, so analysts can assess relevance and risk quickly and pivot straight to the original posts and evidence.
Key benefits:
- Unified actor profiles: personas, activities and relationships consolidated in one view
- Search and filter by aliases, handles, contacts or wallets, and by geography, sector and threat type
- MITRE ATT&CK mapped TTPs and the latest finished intelligence for each actor
- Investigation workspace with profile cards, activity timelines and AI summaries
- API integration to enrich SIEM, SOAR and case management tools with actor intelligence



