





DATASHEET
Zero-Trust and KELA Cyber Intelligence Platform
How cyber threat intelligence keeps your Zero Trust policies effective against new attacker tactics.
Share:
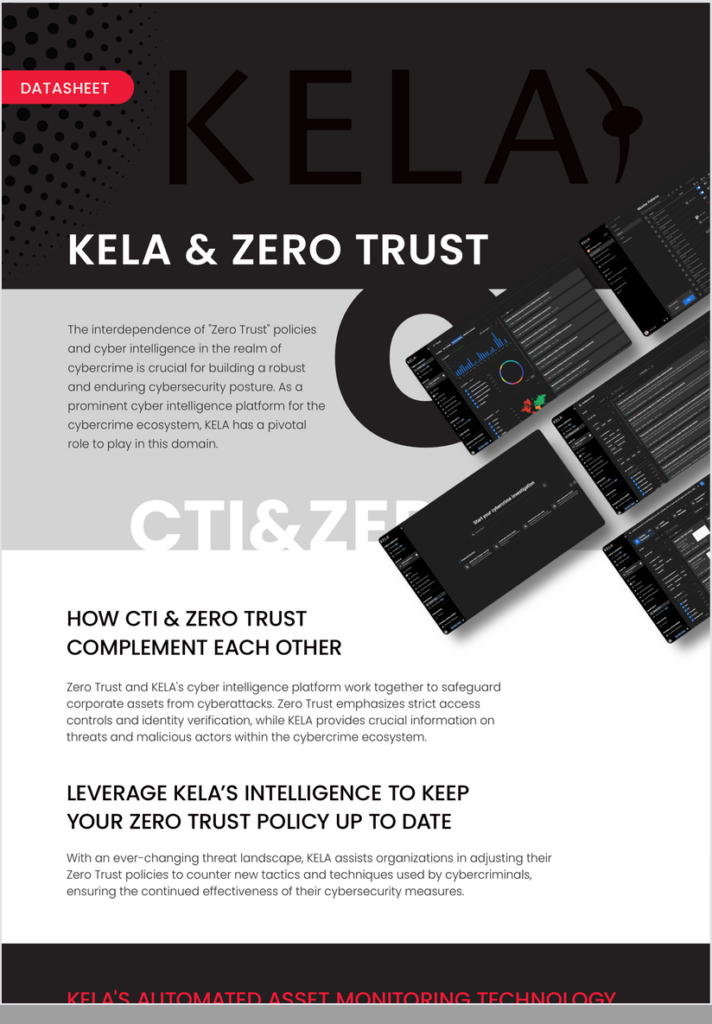
Zero Trust emphasizes strict access controls and identity verification. KELA’s cyber intelligence platform complements it with what Zero Trust cannot see on its own: which credentials, accounts and assets of yours are already circulating in the cybercrime ecosystem, and which tactics threat actors are using right now.
This datasheet explains how KELA’s automated asset monitoring and real-time alerts on compromised accounts help organizations adjust and enforce their Zero Trust policies as the threat landscape changes.
Key benefits:
- Identify and assess risks to your digital assets in real time
- Gain access visibility and control with alerts on organization-related compromised accounts
- Ensure rapid response and minimize exposure time when credentials leak
- Stay compliant with regulations that require Zero Trust, with a documented monitoring record
- Reduce insider threat risk and extend Zero Trust consistently across your supply chain



