

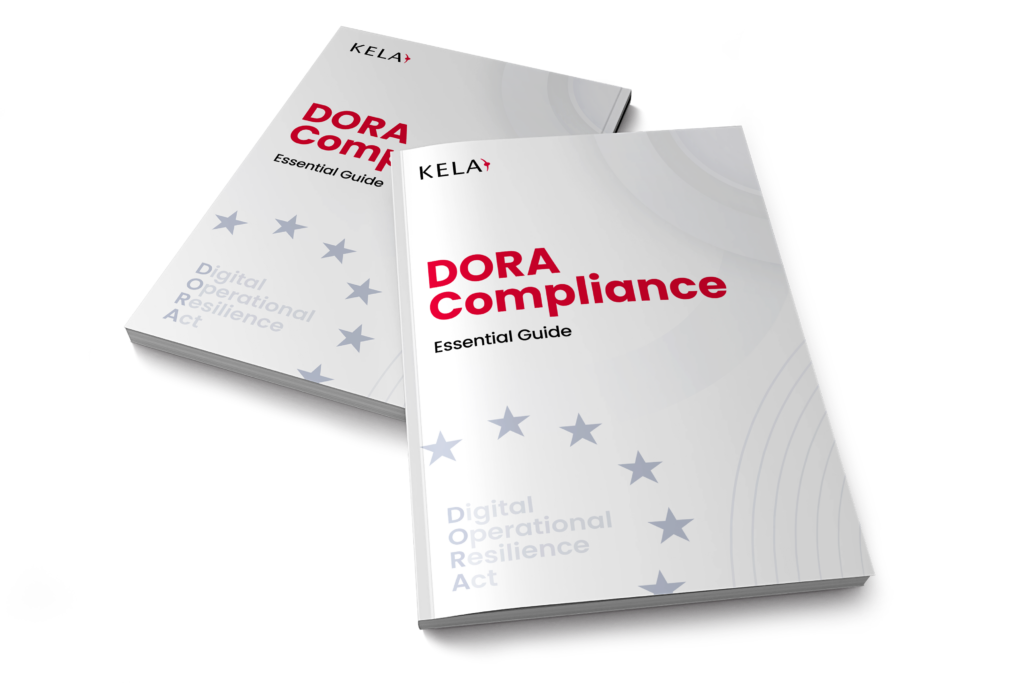
ESSENTIAL GUIDE
DORA Compliance
Building Digital Operational Resilience for financial entities and their ICT providers.
Share:
What's inside:
- Supply Chain Oversight: continuously monitor critical ICT third-party providers for risks, a mandatory requirement under DORA’s third-party risk pillar.
- Threat-Led Testing Support: Equip red teams with real-time threat intelligence to conduct the advanced resilience testing required by the regulation.
- Rapid Incident Reporting: Leverage real-time alerts on threats and leaks to meet DORA’s tight initial incident notification deadlines.
- Attack Surface Visibility: Map and secure all external-facing digital assets to ensure the integrity of network and information systems.