

The Big Thaw: Refrigeration Sabotage and Early-Warning Indicators
After attackers changed the settings of refrigeration controllers at about 700 French retail sites on October 11-12, 2026, French authorities attributed the attack to Shahid Kaveh, a cyber unit of Iran's Islamic Revolutionary Guard Corps (IRGC), but published no technical indicators. KELA traced the publicly reported indicators linked to the unit's personas and to refrigeration-controller attacks

Updated November 11, 2026
Executive Summary
On the night of October 11-12, 2026, attackers changed the settings of refrigeration controllers at about 700 French retail sites, causing large stock losses and at least 15 fires. On November 9, 2026, French authorities attributed the attack to Shahid Kaveh, a cyber unit of Iran’s Islamic Revolutionary Guard Corps (IRGC), but published no technical indicators. This report examines whether infrastructure linked to the unit and to attacks on refrigeration controllers has touched Israel, and what else it has been doing since the French attack.
KELA collected the publicly reported indicators linked to the unit’s personas and to refrigeration-controller attacks, and traced their activity in KELA Control. Apart from unrelated traffic on three addresses that now serve other purposes, none of this infrastructure communicated with Israeli IP addresses between August 12 and November 10, 2026. The same infrastructure was active elsewhere in that period. The key findings are:
- Sessions against Danfoss refrigeration controllers in South Africa, not reported elsewhere: On October 27-28, 2026, 188.208.141[.]210 held HTTPS sessions with four Danfoss AK-SM800A controllers in South Africa, days after researchers saw it try default Danfoss credentials on a decoy.
- CISA-listed infrastructure still active after its reported window: Two addresses from CISA’s July 2026 list of Iranian-affiliated PLC attackers scanned industrial-control ports in October, including Modbus (port 502) and two French hosts probed on October 6, 2026, five days before the attack.
- A burst of scanning into Saudi Arabia: On October 29, 2026, 88.80.150[.]200 sent 1,050 connection attempts to 252 hosts in Saudi Arabia, including two mail servers under the sahara.com domain.
- No actor-linked traffic to Israeli refrigeration controllers: About 45 Dixell XWEB controllers on Israeli networks are exposed to the internet, and none received sessions from the infrastructure in this report.
- One real Israeli Danfoss controller received anonymous sessions: Six of the seven Israeli hosts showing a Danfoss StoreView interface are decoys. The seventh received Tor-originated sessions on October 30, 2026, and shares a factory-default certificate with two of the South African targets; KELA cannot attribute these sessions.
- The addresses in this report could serve as early-warning indicators for Israel: CERT-FR describes the unit as mainly targeting Israel and the US, and the infrastructure was active against industrial and refrigeration equipment abroad in October while comparable Israeli equipment remains exposed.
Scope, Data Sources and Methodology
This report covers August 12 to November 10, 2026. It draws on KELA Control netflow, passive DNS and certificate data, and on internet scan data for exposed refrigeration controllers.
The French investigation published no indicators, so the initial indicators come from three public sources linked to the unit’s personas or to refrigeration-controller attacks:
- CISA AA26-097A: 21 IP addresses used by Iranian-affiliated actors exploiting internet-exposed PLCs, with association windows from January 2025 to July 2026.
- Danfoss decoy observations: 188.208.141[.]210, which researchers saw reach a Danfoss AK-SM decoy through the FOFA scanning engine on October 25, 2026, and try default credentials on October 27, 2026.
- Israeli food-plant sabotage, May 2026: the GRAT command-and-control server 84.201.6[.]131 and seven lower-confidence addresses, which researchers attribute to Cyber Isnaad Front.
Using KELA Control, KELA then examined the activity of these indicators:
- Indicator netflow: communications of each initial indicator from August 12, 2026, and of their hosting ranges from September 6, 2026, to November 10, 2026.
- Controller mapping: internet-exposed Danfoss StoreView and Dixell XWEB controllers in France (559 hosts) and Israel (53 hosts), and who communicated with a sample of 150 French controllers between October 8 and 13, 2026, and with all 53 Israeli hosts between September 6 and November 10, 2026.
- Pivots: hosts that the indicators contacted, and other hosts that held sessions with the same controllers.
Netflow is sampled, so a missing flow does not prove that no communication took place. Netflow also records connections, not their content: it cannot show logins or configuration changes. The documented Israeli incidents, a March-April 2026 refrigeration campaign and the May 2026 food-plant sabotage, predate the period covered.
Background: The October 2026 Refrigeration Attack
This section summarizes the French attack and the attribution that frames the rest of the report.
The attackers changed the defrost parameters of refrigeration controllers at about 700 French retail sites, fixing them at high temperatures. Victims were mainly the Casino, Leclerc, Coopérative U, Metro, Carrefour and Intermarché groups, plus butchers, a slaughterhouse and food plants. CERT-FR’s alert named the Danfoss AK-SM and AK-SC series, Copeland xweb and Dixell xweb as targeted equipment, all reached through management interfaces exposed to the internet.
France’s Cyber Crisis Coordination Centre (ANSSI, COMCYBER, DGA, DGSE and DGSI) attributed the attack to the Shahid Kaveh unit of the IRGC Electronic and Cyber Centre on a “bundle of indicators”:
- The attack infrastructure was also used in the same period for Modbus (port 502) reconnaissance of Schneider Electric equipment.
- The operators used the FOFA scanning engine.
- The unit’s outlet CyberbanNews relayed the attack from October 13, 2026.
- Traces of Farsi were found in the attack infrastructure.
CERT-FR lists the unit’s hacktivist personas as CyberAveng3rs, Soldiers of Solomon, Mr. Soul and Cyber Isnaad Front. It also states that the unit claimed a sabotage campaign against Israeli and US industrial equipment, including Israeli refrigeration equipment, in March and April 2026. On November 2-3, 2026, the Israel National Cyber Directorate warned Israeli supermarket chains to secure their refrigeration systems; the reported warning named no Israeli incident.
The following table sets the French attack against the infrastructure activity described in this report:
Date | Event |
|---|---|
November 9, 2026 | France attributes the attack to Shahid Kaveh |
November 2-3, 2026 | The Israel National Cyber Directorate warns Israeli supermarket chains |
November 2, 2026 | Refrigeration failures at supermarkets in several European countries, not covered by the French attribution |
October 30, 2026 | Tor exit nodes hold sessions with a real Israeli Danfoss controller |
October 29, 2026 | CISA-listed 88.80.150[.]200 sweeps hosts in Saudi Arabia |
October 27-28, 2026 | 188.208.141[.]210 holds sessions with Danfoss controllers in South Africa |
October 25-27, 2026 | 188.208.141[.]210 reaches a Danfoss decoy through FOFA and tries default credentials |
October 13, 2026 | CyberbanNews relays the attack |
October 11-12, 2026 | French refrigeration controllers sabotaged |
October 3-7, 2026 | CISA-listed 88.80.150[.]199 scans industrial-control ports, including two French hosts on October 6, 2026 |
Findings
This chapter covers the activity of the initial indicators in KELA Control: the sessions against Danfoss controllers in South Africa, the October reconnaissance by CISA-listed infrastructure, and the exposure of Israeli refrigeration controllers.
Danfoss Controller Sessions in South Africa
Between October 27 and 28, 2026, 188.208.141[.]210 held repeated HTTPS sessions with four Danfoss AK-SM800A refrigeration controllers in South Africa, activity not reported elsewhere. KELA Control records 71 flows between the address and these controllers, 59 of them on October 28, 2026. The address sits in 188.208.141.0/24, a LeapSwitch Networks range (ASN 132335) geolocated to India.
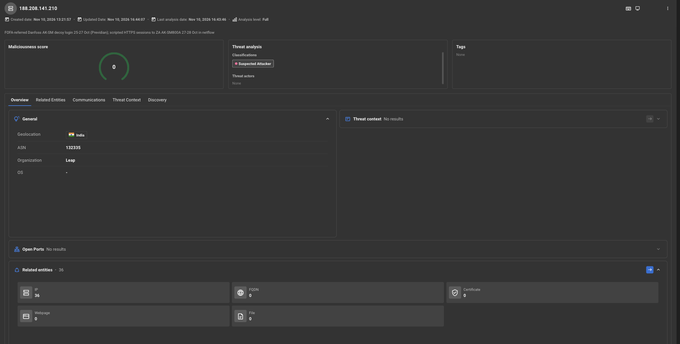
KELA Control overview of 188.208.141[.]210, geolocated to India, ASN 132335
All four targets present Danfoss AK-SM800A device certificates and sit on South African networks. The following table lists them with the flows KELA Control records:
Controller | Flows | First and Last Flow (UTC) | Notes |
|---|---|---|---|
154.68.174.213 | 53 | October 28, 2026, 03:17 - 04:06 | Port 443 only; 21 flows carry more than 200 bytes |
154.68.174.151 | 10 | October 27, 2026, 14:51 - October 28, 2026, 04:32 | Ports 443 and 80 |
154.68.174.149 | 6 | October 27, 2026, 14:51 - October 28, 2026, 04:31 | Port 443 |
41.78.230.66 | 2 | October 27, 2026, 15:03 - 15:55 | Port 443; both flows carry payload |
The 49-minute run against 154.68.174.213 is sustained activity, with repeated payload-carrying flows to the controller’s HTTPS port rather than a single scan probe. The sessions began on October 27, 2026, the day researchers’ decoy logged the same address trying default Danfoss credentials. On October 25, 2026 the address also contacted a cloud-hosted Australian address that KELA Control fingerprints as Danfoss.
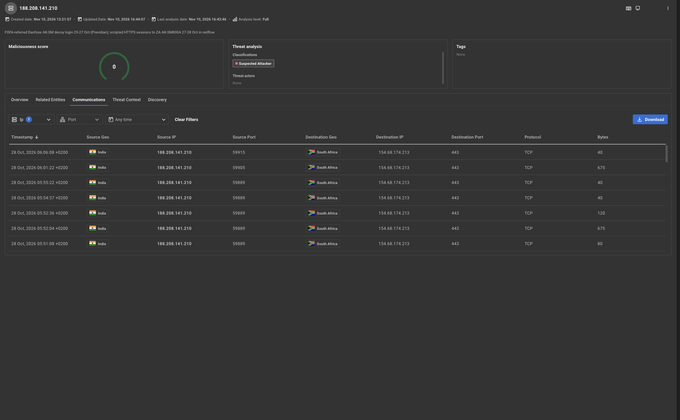
KELA Control communications of 188.208.141[.]210 filtered to 154.68.174.213, local times in UTC+2
The controllers present self-signed Danfoss certificates (issuer “SelfSigned-DanfossSM800A”, organization Danfoss). Netflow shows that the sessions took place, not what they did, so it cannot show whether the address logged in or changed controller settings.
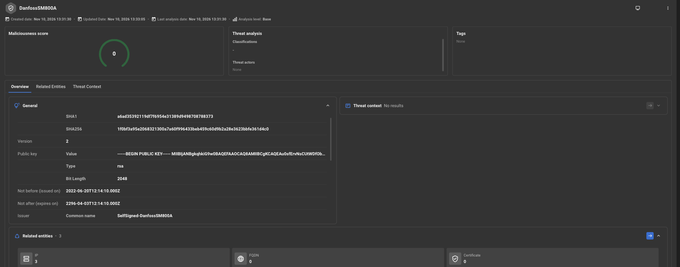
Danfoss AK-SM800A device certificate presented by one of the South African targets
CISA-Listed Infrastructure Active in October
Two addresses from CISA’s July 2026 indicator table, 88.80.150[.]199 and 88.80.150[.]200, were still scanning in October 2026, after the July 2026 association CISA gave them. Both sit in 88.80.150.0/24, a Bulgarian range registered to Redcluster LTD (ASN 44901, network name DEDISTART-COM).
88.80.150[.]199 ran a week of reconnaissance that ended four days before the French attack. The following table summarizes its activity in KELA Control:
Date | Activity |
|---|---|
October 3, 2026 | SSH (port 22) sweep of hosts in a Canadian cloud range |
October 5, 2026 | Probes of industrial-control ports, mostly in Canada: Niagara Fox (1911, 4911), Red Lion Crimson (789), 503 and 20257-20259; replies came from a Tridium Niagara controller and from hosts listening on port 789 |
October 6, 2026 | Port 1789 probe of one Canadian host (168.151.12.103) at 11:51 UTC, then port 505 probes of 17 hosts in 195.219.0.0/16 at 12:33-12:34 UTC: ten in Spain, three in Belgium, two in Germany and two in France (195.219.104.133 and 195.219.44.55) |
October 7, 2026 | Modbus (port 502) probes of two US hosts, a port 1201 probe of one US host, and port 8789 and probes of five hosts, mostly cloud servers not classified as potential victims |
The Modbus probes match the port 502 reconnaissance that CERT-FR attributes to the attack infrastructure. The services the European hosts run on port 505 could not be established.
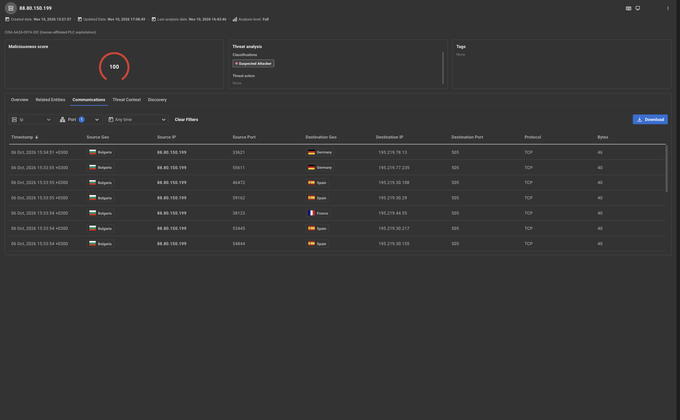
KELA Control communications of 88.80.150[.]199 filtered to port 505, local times in UTC+3
88.80.150[.]200 was mostly quiet until October 29, 2026, when it sent a burst of connection attempts between 01:16 and 13:07 UTC. KELA Control records 1,076 outbound flows that day to 278 hosts across 389 different ports; 1,050 of them went to 252 hosts in Saudi Arabia, including two mail servers under the sahara.com domain (212.76.69.98 and 212.76.69.99).
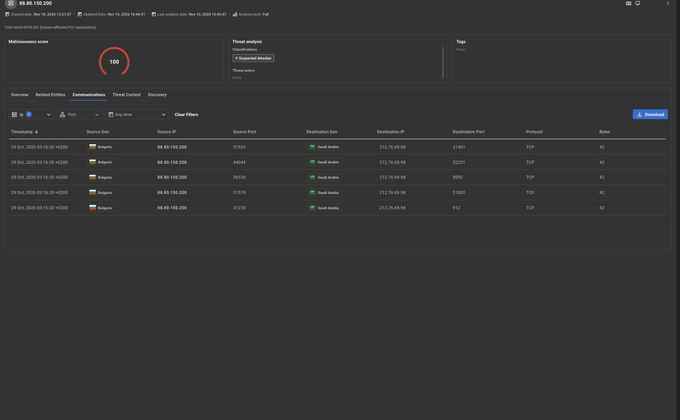
KELA Control communications of 88.80.150[.]200 to 212.76.69.98 (securemail03.sahara.com), local times in UTC+2
KELA classified 45 hosts as potential victims: the controllers 188.208.141[.]210 held sessions with, the hosts 88.80.150[.]199 probed on industrial-control ports and the two sahara.com mail servers 88.80.150[.]200 swept. They are listed in Appendix B.
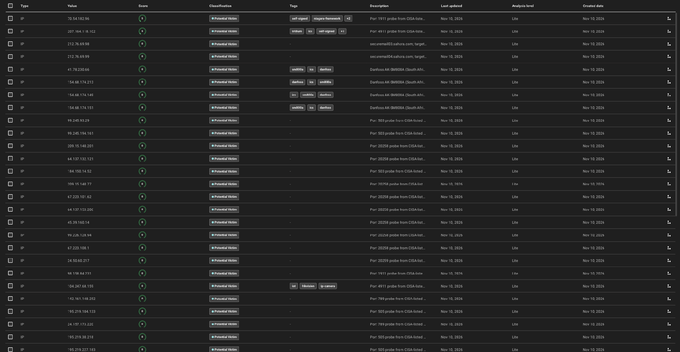
Hosts classified as potential victims in KELA Control as a list
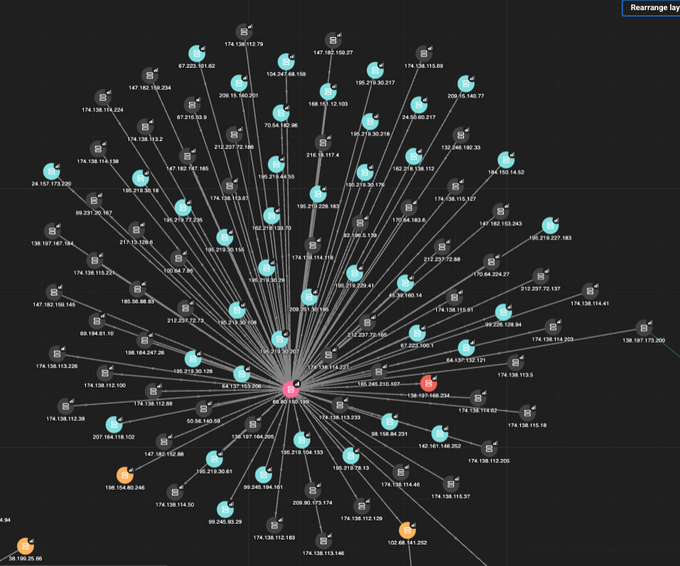
Hosts classified as potential victims in KELA Control in Link Analysis
Israeli Exposure and Early-Warning Indicators
None of the infrastructure in this report communicated with Israeli IP addresses in an actor-like way between August 12 and November 10, 2026. KELA Control returned thousands of flows for the 23 initial indicators examined there (the 21 CISA addresses, 188.208.141[.]210 and 84.201.6[.]131), none with an Israeli peer, and the LeapSwitch and Redcluster ranges hosting 188.208.141[.]210 and 88.80.150[.]199-200 show no Israeli traffic either. The seven lower-confidence addresses from the food-plant research were checked in the same netflow data without being added to KELA Control. The only Israeli traffic involving initial indicators is unrelated: readers of the manga website now on 45.82.66[.]163 (502 flows), Cloudflare edge servers fetching from the website on 175.110.121[.]39 (5 flows) and DNS traffic to the open resolver on 185.82.73[.]171 (4 flows).
The addresses in this report could serve as early-warning indicators for Israeli organizations. CERT-FR describes Shahid Kaveh as mainly targeting Israel and the US, and states that it claimed attacks on Israeli refrigeration equipment in 2026. In October, two of the indicators probed industrial-control ports in Canada, the US and Europe, and a third held sessions with refrigeration controllers in South Africa. Israel exposes the same classes of equipment to the internet, so a first contact from any of these addresses to Israeli industrial or refrigeration equipment could be an early sign of targeting.
Internet scan data from November 10, 2026, shows the following Israeli exposure:
Equipment | Hosts | Notes |
|---|---|---|
Dixell XWEB (XWEB, XWEB EVO, XWEB PRO) | 45 | Mostly on Bezeq ranges (33), also Cellcom, Partner, XFone and others; excludes one address that answers with an XWEB page on 899 ports |
Danfoss StoreView, real device | 1 | 46.210.121.159 on Cellcom, port 8080, an end-of-life nginx version |
Danfoss StoreView, decoys | 6 | Azure, Google Cloud, AWS and one hosting provider in Israel, all serving the same 772-byte page (one HTML hash), four of them on random high ports; scan data tags two as honeypots |
None of the 45 XWEB hosts received sessions from the infrastructure in this report; most traffic to them in the period came from internet-wide scanners.
On October 30, 2026, between 12:30 and 13:48 UTC, three Tor exit nodes (192.42.116.21, 192.42.116.117 and 192.42.116.104) sent traffic within established TCP sessions to the web interface of 46.210.121.159, three days before the November 2, 2026, European refrigeration incidents. Tor hides who was behind the sessions, and netflow does not show what they did, so this activity cannot be linked to Shahid Kaveh or to the infrastructure in this report.
The Israeli device is also linked to the South African targets by a certificate. On port 1041, 46.210.121.159 presents a factory-default Danfoss AK-SM800A certificate (SHA-1 02:71:5A:B8:3D:61:D6:EB:5F:E2:C7:B8:E7:34:4D:EF:DA:78:DC:F8, self-signed, issued March 25, 2020). The same certificate appears on 154.68.174.149 and 154.68.174.151, two of the South African controllers that 188.208.141[.]210 contacted, and on eight controllers in France. A search for this certificate in an internet-scanning engine such as FOFA returns all 11 devices together, which shows a possible route from the South African targets to the Israeli device but is not evidence that the same operator reached it.
46.210.121.159 is not part of the KELA Control investigation. The investigation holds the reported infrastructure and the hosts it communicated with, and no actor-linked address communicated with this device; KELA identified it separately, by mapping exposed Israeli controllers and examining their netflow.
Indicator Appendix
The appendices list the initial indicators with the activity observed for each, and the hosts classified as potential victims.
Appendix A: Initial Indicators
All addresses below are initial indicators from public reporting, with the activity KELA observed for each between August 12 and November 10, 2026. For Israeli organizations, contact from any of them to industrial or refrigeration equipment could be an early-warning indicator; several CISA-listed addresses now carry unrelated traffic, so they should be vetted before blocking. The following table lists them:
Indicator | Reported By | Activity Observed by KELA |
|---|---|---|
188.208.141[.]210 | HTTPS sessions with four Danfoss AK-SM800A controllers in South Africa, October 27-28, 2026 | |
88.80.150[.]199 | CISA AA26-097A | Industrial-control port reconnaissance October 3-7, 2026, including port 505 probes of two French hosts on October 6, 2026 |
88.80.150[.]200 | CISA AA26-097A | Burst of connection attempts, mostly to Saudi Arabia, October 29, 2026 |
88.80.150[.]202 | CISA AA26-097A | Inbound traffic only |
84.201.6[.]131 | GRAT command-and-control server; 10 flows, no industrial-control or refrigeration-controller activity | |
185.82.73[.]162, .164, .165, .167, .168, .170, .171, .175 | CISA AA26-097A | No industrial-control or refrigeration-controller activity; 185.82.73[.]167 carries VPN traffic and 185.82.73[.]171 runs an open DNS resolver |
175.110.121[.]39, .41, .42, .107 | CISA AA26-097A | Web-server traffic, mainly on ports 80 and 443; 175.110.121[.]39 serves a website behind Cloudflare |
135.136.1[.]133, 141.11.164[.]153, 185.225.17[.]225, 192.142.54[.]79, 84.200.205[.]165, 79.133.46[.]209 | CISA AA26-097A | Server-side or low-volume traffic only; no industrial-control or refrigeration-controller activity |
84.201.6[.]128, 84.201.6[.]129, 146.103.40[.]190, 193.29.104[.]5, 85.137.56[.]9, 85.17.55[.]232 | Researchers, lower confidence | No industrial-control or refrigeration-controller activity |
45.82.66[.]163 | Researchers, lower confidence | Hosts a public manga website (mangasoda.com) in this period |
Researchers also published file indicators of the GRAT toolkit from the Israeli food-plant intrusion, listed in the following table:
SHA-256 | File Name |
|---|---|
6f5f427d96656ae51405e6a5e65253759db45ea0a17da2d70f881404a4ed717b | Checker.exe.exe |
0ad128e813314e4562489478e6def8c6dfcc251e006d7f55b24273e93d3bc7fb | WindowsUpdater.exe |
c4909b2d7a7f813b5a3d729fe64535033e716ae89dc39c402a6cb8ccbccaadca | SpellChecker.exe |
86194eb5c5abcfe763899aaad7eb64894c71e816dd7d27427c8bac4ab280533d | WindowsUpdater.exe |
Appendix B: Potential Victims
The following table lists the 45 hosts classified as potential victims in KELA Control, with the activity observed for each:
IP Address | Country | Activity Observed in KELA Control |
|---|---|---|
154.68.174[.]149 | South Africa | Danfoss AK-SM800A refrigeration controller; HTTPS sessions from 188.208.141[.]210, October 27-28, 2026 |
154.68.174[.]151 | South Africa | Danfoss AK-SM800A refrigeration controller; HTTPS sessions from 188.208.141[.]210, October 27-28, 2026 |
154.68.174[.]213 | South Africa | Danfoss AK-SM800A refrigeration controller; HTTPS sessions from 188.208.141[.]210, October 27-28, 2026 |
41.78.230[.]66 | South Africa | Danfoss AK-SM800A refrigeration controller; HTTPS sessions from 188.208.141[.]210, October 27-28, 2026 |
212.76.69[.]98 | Saudi Arabia | securemail03.sahara.com (mail server); 88.80.150[.]200 sweep, October 29, 2026 |
212.76.69[.]99 | Saudi Arabia | securemail04.sahara.com (mail server); 88.80.150[.]200 sweep, October 29, 2026 |
195.219.104[.]133 | France | Port 505 probe from 88.80.150[.]199, October 6, 2026 |
195.219.227[.]183 | Belgium | Port 505 probe from 88.80.150[.]199, October 6, 2026 |
195.219.228[.]183 | Belgium | Port 505 probe from 88.80.150[.]199, October 6, 2026 |
195.219.229[.]41 | Belgium | Port 505 probe from 88.80.150[.]199, October 6, 2026 |
195.219.30[.]108 | Spain | Port 505 probe from 88.80.150[.]199, October 6, 2026 |
195.219.30[.]128 | Spain | Port 505 probe from 88.80.150[.]199, October 6, 2026 |
195.219.30[.]155 | Spain | Port 505 probe from 88.80.150[.]199, October 6, 2026 |
195.219.30[.]176 | Spain | Port 505 probe from 88.80.150[.]199, October 6, 2026 |
195.219.30[.]18 | Spain | Port 505 probe from 88.80.150[.]199, October 6, 2026 |
195.219.30[.]207 | Spain | Port 505 probe from 88.80.150[.]199, October 6, 2026 |
195.219.30[.]217 | Spain | Port 505 probe from 88.80.150[.]199, October 6, 2026 |
195.219.30[.]218 | Spain | Port 505 probe from 88.80.150[.]199, October 6, 2026 |
195.219.30[.]29 | Spain | Port 505 probe from 88.80.150[.]199, October 6, 2026 |
195.219.30[.]61 | Spain | Port 505 probe from 88.80.150[.]199, October 6, 2026 |
195.219.44[.]55 | France | Port 505 probe from 88.80.150[.]199, October 6, 2026 |
195.219.77[.]235 | Germany | Port 505 probe from 88.80.150[.]199, October 6, 2026 |
195.219.78[.]13 | Germany | Port 505 probe from 88.80.150[.]199, October 6, 2026 |
209.251.30[.]195 | United States | Port 1201 probe from 88.80.150[.]199, October 7, 2026 |
168.151.12[.]103 | Canada | Port 1789 probe from 88.80.150[.]199, October 6, 2026 |
70.54.182[.]96 | Canada | Port 1911 probe from 88.80.150[.]199, October 5, 2026 |
98.158.84[.]231 | Canada | Port 1911 probe from 88.80.150[.]199, October 5, 2026 |
209.15.140[.]201 | Canada | Port 20258 probe from 88.80.150[.]199, October 5, 2026 |
209.15.140[.]77 | Canada | Port 20258 probe from 88.80.150[.]199, October 5, 2026 |
45.39.160[.]14 | United States | Port 20258 probe from 88.80.150[.]199, October 5, 2026 |
64.137.132[.]121 | Canada | Port 20258 probe from 88.80.150[.]199, October 5, 2026 |
64.137.153[.]206 | Canada | Port 20258 probe from 88.80.150[.]199, October 5, 2026 |
67.223.100[.]1 | Canada | Port 20258 probe from 88.80.150[.]199, October 5, 2026 |
67.223.101[.]62 | Czechia | Port 20258 probe from 88.80.150[.]199, October 5, 2026 |
99.226.128[.]94 | Canada | Port 20258 probe from 88.80.150[.]199, October 5, 2026 |
24.50.60[.]217 | Canada | Port 20259 probe from 88.80.150[.]199, October 5, 2026 |
104.247.68[.]159 | Canada | Port 4911 probe from 88.80.150[.]199, October 5, 2026 |
207.164.118[.]102 | Canada | Port 4911 probe from 88.80.150[.]199, October 5, 2026 |
162.218.138[.]112 | United States | Port 502 probe from 88.80.150[.]199, October 7, 2026 |
162.218.139[.]70 | United States | Port 502 probe from 88.80.150[.]199, October 7, 2026 |
184.150.14[.]52 | Canada | Port 503 probe from 88.80.150[.]199, October 5, 2026 |
99.245.194[.]161 | Canada | Port 503 probe from 88.80.150[.]199, October 5, 2026 |
99.245.93[.]29 | Canada | Port 503 probe from 88.80.150[.]199, October 5, 2026 |
142.161.148[.]252 | Canada | Port 789 probe from 88.80.150[.]199, October 5, 2026 |
24.157.173[.]220 | Canada | Port 789 probe from 88.80.150[.]199, October 5, 2026 |

Advanced Cyber Threat Intelligence
KELA's Cyber Intelligence Center provides finished intelligence and threat-actor monitoring for Global 1000 and Government security teams as part of our platform offering.
Refrigeration Sabotage FAQ
What happened in the French supermarket refrigeration sabotage?
On the night of October 11-12, 2026, attackers changed the defrost settings of refrigeration controllers at about 700 French retail sites, fixing them at high temperatures. The attack caused large stock losses and at least 15 fires. The targeted equipment included Danfoss AK-SM and AK-SC series, Copeland xweb and Dixell xweb controllers, all reached through management interfaces exposed to the internet.
Who did France attribute the refrigeration sabotage to?
On November 9, 2026, French authorities attributed the attack to Shahid Kaveh, a cyber unit of Iran's Islamic Revolutionary Guard Corps (IRGC). The attribution rested on a bundle of indicators: Modbus (port 502) reconnaissance from the attack infrastructure, use of the FOFA scanning engine, relay of the attack by the unit's outlet CyberbanNews from October 13, 2026, and traces of Farsi in the attack infrastructure. France published no technical indicators.
Did indicators linked to Shahid Kaveh communicate with Israeli networks?
KELA examined publicly reported indicators linked to the unit's personas and to refrigeration-controller attacks between August 12 and November 10, 2026. Apart from unrelated traffic on three addresses that now serve other purposes, none communicated with Israeli IP addresses. None of about 45 internet-exposed Dixell XWEB controllers on Israeli networks received sessions from this infrastructure. Netflow is sampled, so a missing flow does not prove that no communication took place.
What refrigeration controller activity has been observed in South Africa?
On October 27-28, 2026, the address 188.208.141[.]210 held HTTPS sessions with four Danfoss AK-SM800A refrigeration controllers in South Africa; KELA recorded 71 flows, 59 of them on October 28, 2026. Researchers had seen the same address try default Danfoss credentials on a decoy on October 27, 2026. Netflow shows that the sessions took place, not what they did, so it cannot show whether the address logged in or changed controller settings.
How can Israeli organizations use these indicators?
The takeaway is that a first contact from any of these addresses to Israeli industrial or refrigeration equipment could be an early sign of targeting. In October 2026, one indicator held sessions with refrigeration controllers in South Africa and another probed industrial-control ports in Canada, the US and Europe, and Israel exposes the same classes of equipment to the internet. Several CISA-listed addresses now carry unrelated traffic, so they should be vetted before blocking.