Qilin Ransomware Gang Adopts Uncommon Payment System: All Ransom Payments Funneled through Affiliates



Published August 1, 2023
In July, KELA observed that actors behind Qilin (Agenda) RaaS program have announced that ransom payments are paid only to their affiliates’ wallets. Apparently, only then a share of profits is transferred to the Qilin RaaS owners. This approach is less common for RaaS programs: usually victims are paying ransom to wallets controlled by RaaS developers/managers, and only then affiliates receive their share of ransom. The “opposite” approach, now adopted by Qilin, is known to be used by LockBit.
In recent months, KELA has seen Qilin affiliates demanding ransoms in the range of USD 25,000 – 600,000. For example, KELA has identified a real estate development company in Thailand paying USD 600,000 after 20 days of negotiations. Once receiving the ransom, Qilin claimed that initial access was obtained after an employee opened a phishing email on his work computer. The actors also said: “It was absolutely easy to get further into your network. Your administrator passwords are some of the easiest we have seen.”
The group has been active since August 2022. In 2023, Qilin compromised at least 26 victims.
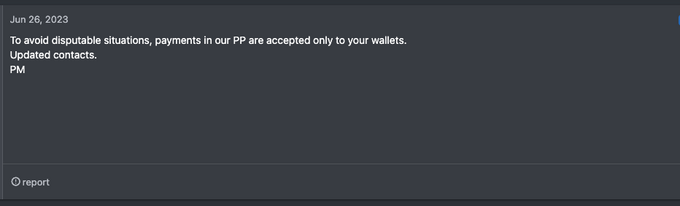
Auto-translated from Russian
Get notified about threats targeting your organization in real-time. Try KELA’s Cyber Threat Intelligence Platform for Free.