







The KELA Platform
Cybercrime activity, threat actors, hacking discussions and hard-to-reach sources, fused with your exposure and attack surface in one place. Enterprises, governments and law enforcement work from the same picture of the attacker, and act on it before it is used against them.
One picture of the attacker
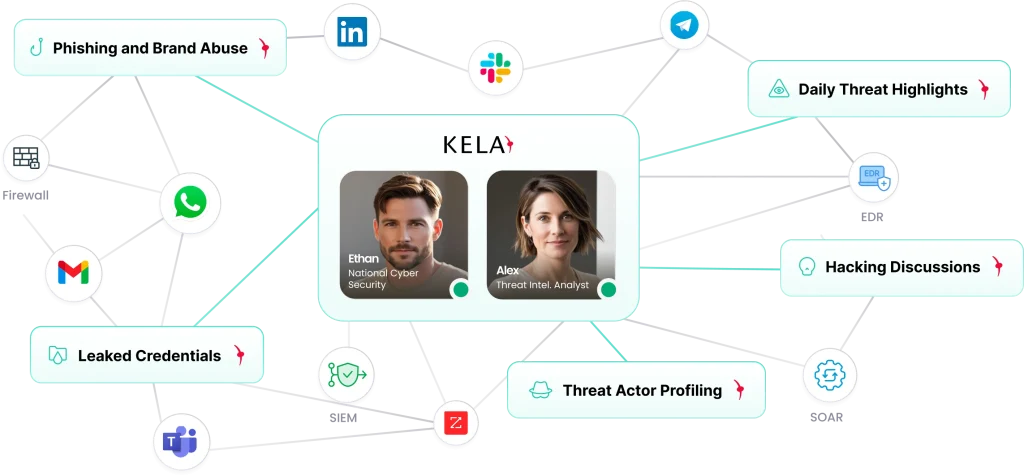
Attackers do not work in silos, so intelligence about them should not either. KELA collects from the places they actually operate: cybercrime forums and markets, closed messaging channels, infostealer logs, leaked credential dumps, ransomware and extortion sites, exploit writeups and proofs of concept mapped to CVE IDs, threat actor identities and your own external attack surface. It fuses all of it into a single view, correlated to your assets, people and suppliers. One source of truth, whether the question comes from the SOC, the CTI desk, vulnerability management, an investigator or the board.
From collection to action, in one platform

Discover & Collect
Map, Monitor, and Gather Intelligence
Analyze & Prioritize
Turn Data into Actionable Insights
Operationalize & Act
Integrate, Automate, and Strengthen Security
Take the product tour
See the fused view for yourself, in a few minutes
What the platform covers
Seven capabilities on one fused intelligence layer. Start with one, add the rest when you need them.

Cyber Threat Intelligence
Finished and raw intelligence from the cybercrime underground, tailored to you.

Continuous Threat Exposure Management
Find, validate and fix the exposures attackers can actually exploit.

Vulnerability Intelligence
Which CVEs criminals are discussing, weaponising and selling, mapped to CVE IDs, often days before EPSS or KEV catch up.

Digital Risk Protection
Brand, domain, executive and data-leak monitoring, with takedowns.

Third-Party Risk Management
Your suppliers’ exposure, seen from the attacker’s side.

AI Trust, Risk and Security Management
Governance and threat coverage for the AI your organisation runs.

Different teams, different use cases. One platform.
The same intelligence, cut for the people who need it, and board-ready views of the threat landscape and your exposure for the people who sign off.

SOC and incident response
Triage alerts with attacker context, and block compromised credentials and infected machines before they are used. Uses CTI and DRP.

Threat intelligence analysts
Investigate actors, campaigns and TTPs with source-level evidence, hacking discussions and threat actor profiles. Uses CTI and Agentic AI.

Vulnerability and exposure management
Prioritise by proof of exploitability and what criminals are actually building, not by CVSS alone. Know when a working exploit is circulating while EPSS still says low and KEV has no entry. Uses Vulnerability Intelligence and CTEM.

Fraud, brand and trust & safety
Catch impersonation, phishing kits, leaked customer data and account-takeover supply early. Uses DRP.

Third-party and supply-chain risk
Score and monitor suppliers on their real exposure, continuously. Uses TPRM.

Government and law enforcement
Track threat actors, their identities, infrastructure and victims across hard-to-reach sources, and build the evidence trail for investigations. Uses CTI and Agentic AI.
Agentic AI, built for the analysts you do not have
Digital CTI analysts that work inside the same fused intelligence: always on, proactive, and integrated with your workflow.

Always on, 24/7
Proactive and interactive
Fully integrated
Works with what you have

Integrations
Push findings to your SIEM, SOAR and ticketing tools and act without changing screens.
API and feeds
Every module is available programmatically, for your own pipelines and dashboards.
Agentless SaaS
No sensors, no agents, no setup. Start with a domain.
The underground cybercrime, in KELA’s numbers
Compromised credentials and ransomware victims: January to August 2026 against the same period of 2025. Source: KELA data lake.
Why Our Customers Love Us
- Stop Real Attacks Before They Happen
- Exposure-Centric with Actionable Intelligence
- Automated and Easy to Use
FAQ
What is the KELA platform?
The KELA platform is one place for cybercrime intelligence. It fuses what KELA collects from the cybercrime underground with your own exposure and attack surface, and delivers it as seven capabilities: Cyber Threat Intelligence, Continuous Threat Exposure Management, Vulnerability Intelligence, Digital Risk Protection, Third-Party Risk Management, AI Trust, Risk and Security Management, and Agentic AI analysts.
What sources does KELA collect from?
Cybercrime forums and markets, closed messaging channels, infostealer logs, leaked credential dumps, ransomware and extortion sites, exploit writeups and proofs of concept, threat actor identities and your organisation’s external attack surface. Findings are correlated to your assets, people and suppliers.
Do I need to deploy anything?
No. The platform is agentless SaaS. You start with a domain, and findings reach your SIEM, SOAR and ticketing tools through integrations and the API.
Which teams use the KELA platform?
SOC and incident response, threat intelligence analysts, vulnerability and exposure management, fraud and brand protection, third-party risk, and government and law enforcement investigators. Leadership gets board-ready views of the threat landscape and the organisation’s exposure.
How is it different from a threat feed?
A feed is a list of indicators. KELA fuses raw and finished intelligence, correlates it to your organisation and prioritises it, so a finding arrives with the who, the where and the why, ready to act on.
How is KELA's vulnerability intelligence different from CVSS, EPSS and KEV?
CVSS scores theoretical severity, EPSS models exploitation probability from public signals, and KEV lists exploitation after it is confirmed in the wild. KELA watches the criminal forums and channels where exploits are built and sold, and maps that activity to CVE IDs while the gap is still open. For CVE-2026-27825, a working proof of concept appeared on the XSS.PRO forum six days after NVD publication, while EPSS rated it 2.3% and KEV had no entry. Read the analysis: https://www.kelacyber.com/blog/intelligence-gap-kev-cve-cvss-mcp-atlassian/


