







SUCCESS STORY
KELA Successfully Prevents A Cyberattack On A Large Telecom Company
An infostealer victim identified without the bot file, letting a major telecom cut off the compromised access.
Share:
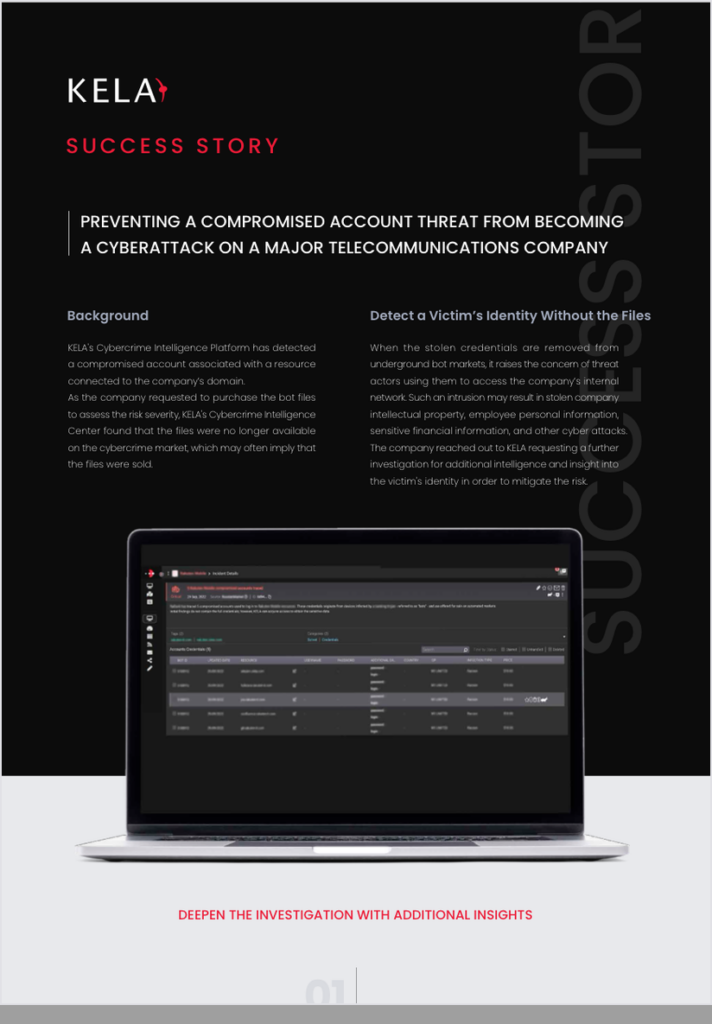
KELA’s platform detected a compromised account tied to a resource on the telecom company’s domain. When the company asked to buy the bot files to assess the risk, KELA’s Cyber Intelligence Center found they were no longer for sale on Russian Market, a sign the credentials had likely been sold to a threat actor.
Pivoting on the bot ID in the Investigate module, KELA’s analysts traced the malware-infected URLs, identified the infostealer as Raccoon Stealer, and surfaced the victim: a former intern whose old company credentials were still live. KELA recommended disabling them, removing the path into the network.
Key results:
- A compromised account on the company’s domain flagged by real-time monitoring
- The infostealer identified as Raccoon Stealer and the infected machine’s owner traced without the bot file
- A former intern’s still-active credentials found and disabled before they were used
- Unauthorized access to internal systems, intellectual property and employee data prevented
- Investigation delivered by KELA’s Cyber Intelligence Center on top of the platform alert



