







KELA Apps for Splunk
Operationalize KELA’s Threat Intelligence Within Splunk
Bolster threat detection and response capabilities,
monitor and protect identities, and access enriched data Inside your Splunk environment –
powered by KELA.
Empower your Splunk environment with KELA’s cutting-edge threat intelligence to enhance proactive threat detection and risk mitigation. KELA’s integration with Splunk provides real-time intelligence on compromised assets, cloud applications and identities, enriching your security event data with attacker-driven insights to deliver contextual, risk-driven defense

Accelerate Threat Response
With actionable intelligence on compromised assets and identities, security teams can quickly prioritize and respond to high-risk events.

Strengthen Threat Detection
KELA’s integration delivers real-time alerts directly within Splunk, ensuring immediate visibility on emerging threats and compromised entities.

Optimize Security Operations
KELA’s intelligence integrates seamlessly with Splunk, reducing alert fatigue and providing critical context to optimize workflows and enhance decision-making.

Powerful Splunk Apps addressing critical use cases
KELA IOC APP for Splunk: Discover, Identify and Track Threats
The KELA IOC App is downloadable from Splunkbase. It enables users to identify, track, and investigate potential threats inside Splunk by collecting data points that signify global malicious events as KELA detects them. This module ensures you can quickly identify compromised assets and take preemptive action to mitigate risks. It enables you and your team to become proactive, and not wait for incidents and attacks to target and impact your company.
KELA Scans for Threats and Extracts IOCs
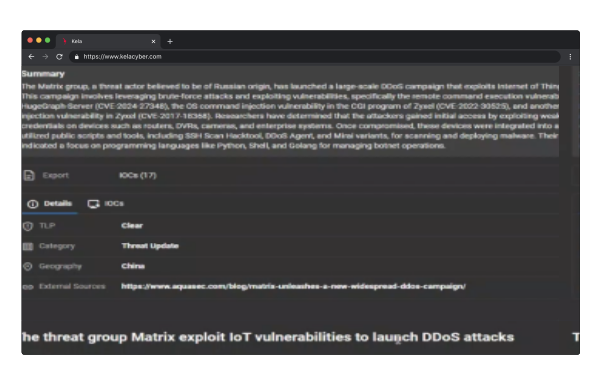
Leverage KELA’s global scanning for cyber threats and IOCs. Access complete intelligence dossiers in the KELA APP, or receive alerts when IOCs automatically populate Splunk dashboards.
IOCs Appear in Splunk Dashboard
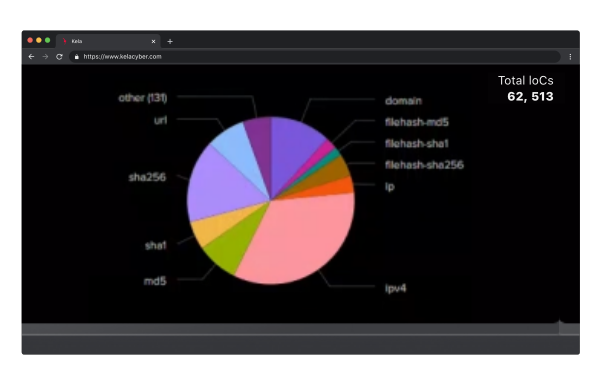
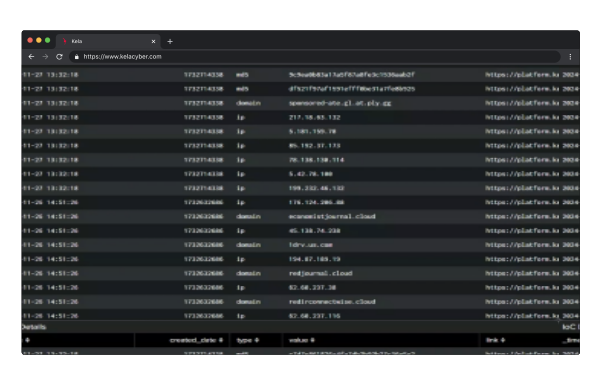
This information will automatically appear in Splunk’s IOC dashboard, and is driven by KELA’s vast data lake of IOC threat Intelligence. Splunk alerts from KELA are context-rich and include valuable information for each IOC including specific IP addresses, file hashes, and domains. The dashboard helps you easily identify the number of IOCs as well as a visual breakdown of IOCs by type.
Daily Updates with Full Context
This information is updated daily and makes it easy to identify threats. Users in the SOC may want to dive deeper into the information and learn more about TTP’s. Users can easily pivot from an IP address in Splunk and open a complete report from KELA for a deeper understanding, or to initiate an investigation.
Fully Integrative in Splunk
This information is available within Splunk and can be displayed in any Splunk dashboard. Kela data is formatted according to Splunk standards, so any IOCs added by the app are according to the Splunk Common Information Model (CIM) to allow easy integrations into custom-built dashboards. For deeper analysis, analysts can select an IOC for deeper investigation and pivot to KELA to review the original source of information for additional information and context.
Benefits

Proactively identify potential threats and compromised assets

Take preemptive steps to fortify defenses and reduce risk before attacks

Gain context and accelerate response to malicious activity on a global scale
KELA Monitor App for Splunk:
Detect identity-based threats and vulnerabilities
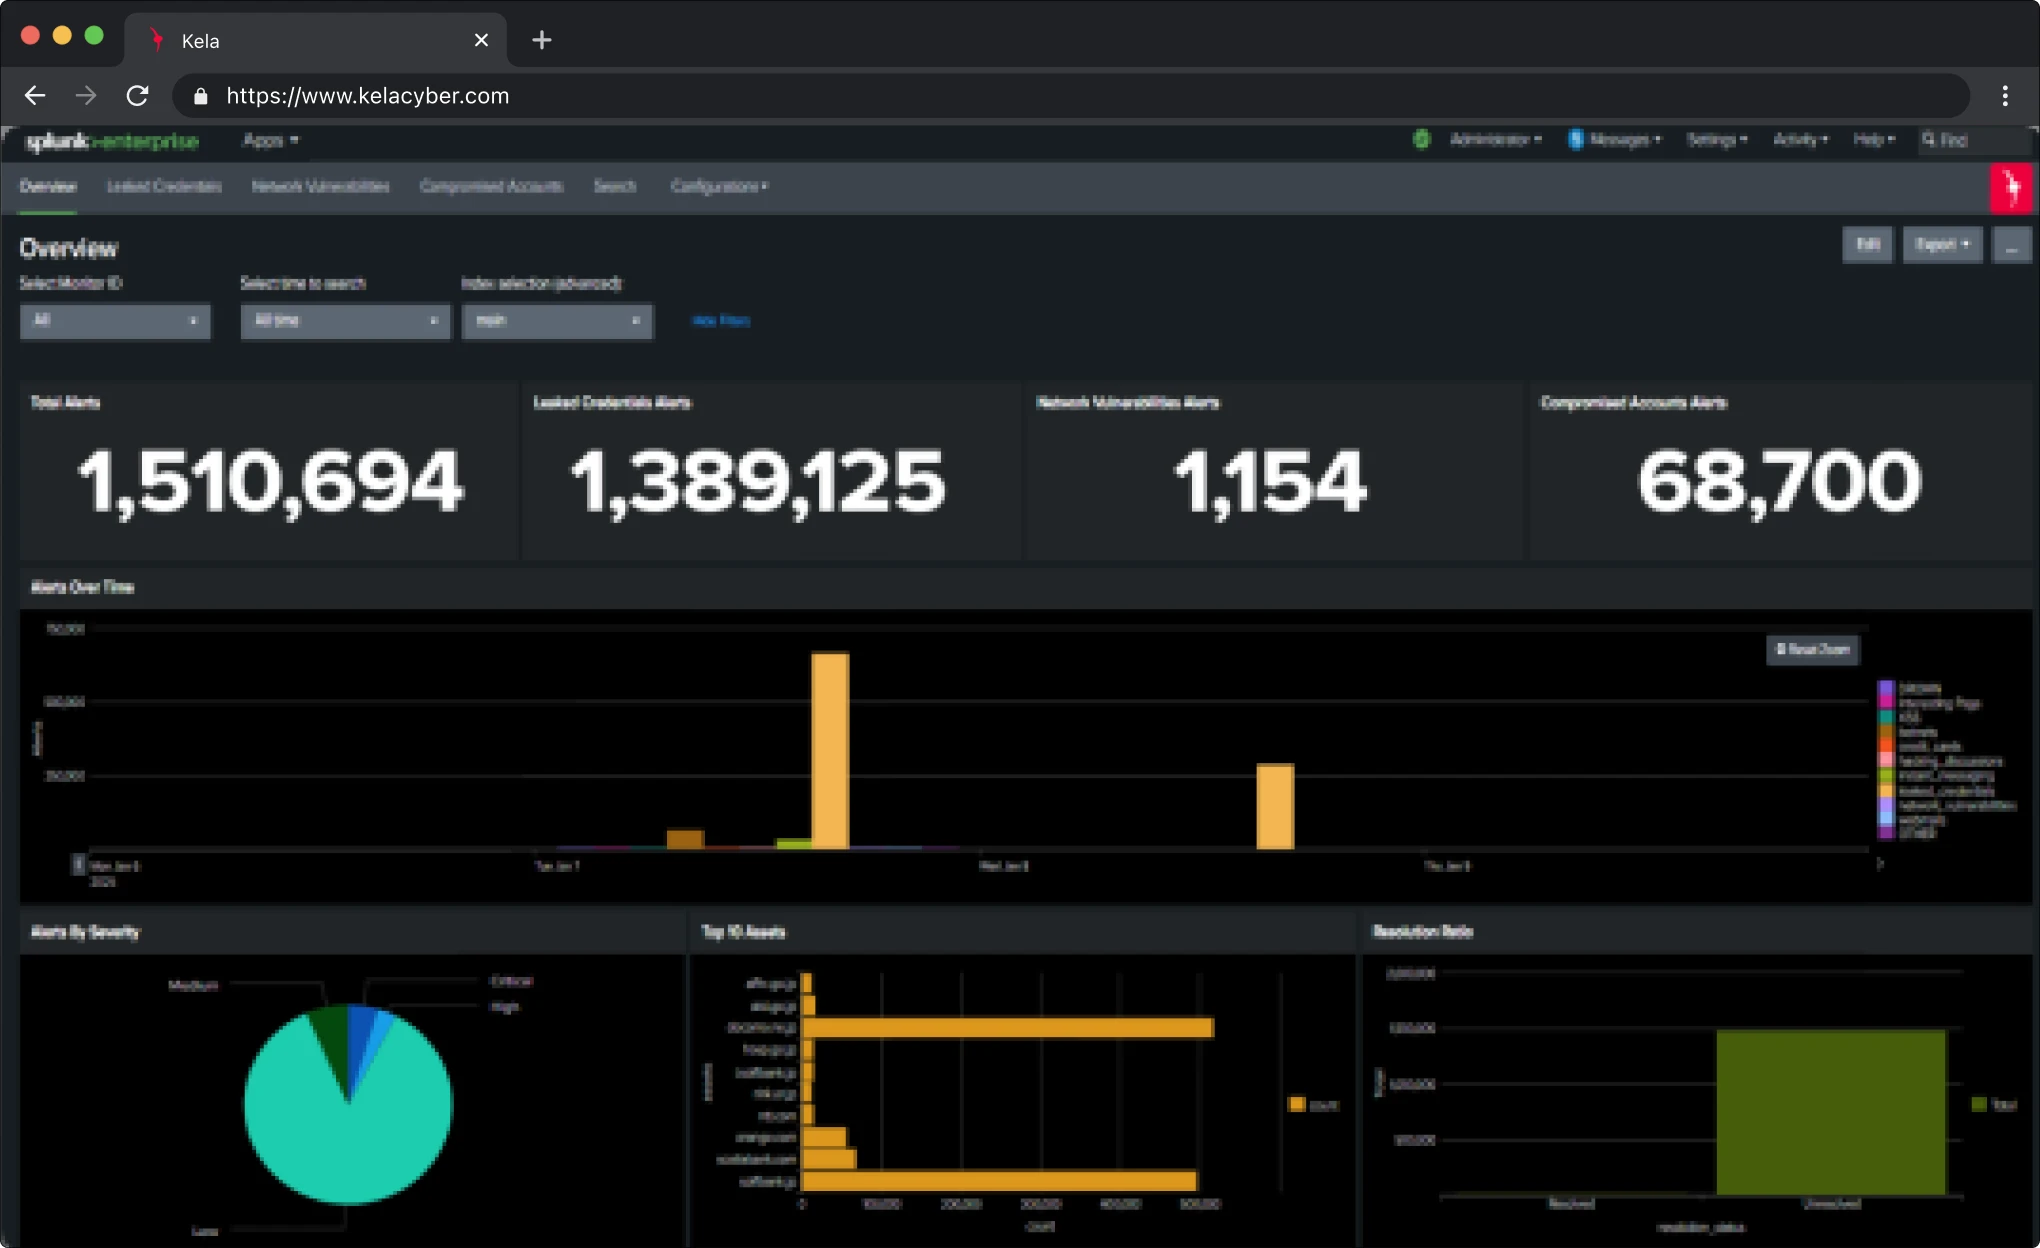
This certified Splunk app enables security teams to view and analyze critical security events related to organizations’ assets and identities. This app monitors identity and credential-based events and risks related to your organization and vulnerabilities affecting network infrastructure. The app provides a clear, intuitive dashboard in Splunk, with immediate visibility into security incidents detected and observed by the KELA Threat Intelligence platform.
Security events available on the Monitor App dashboard include:
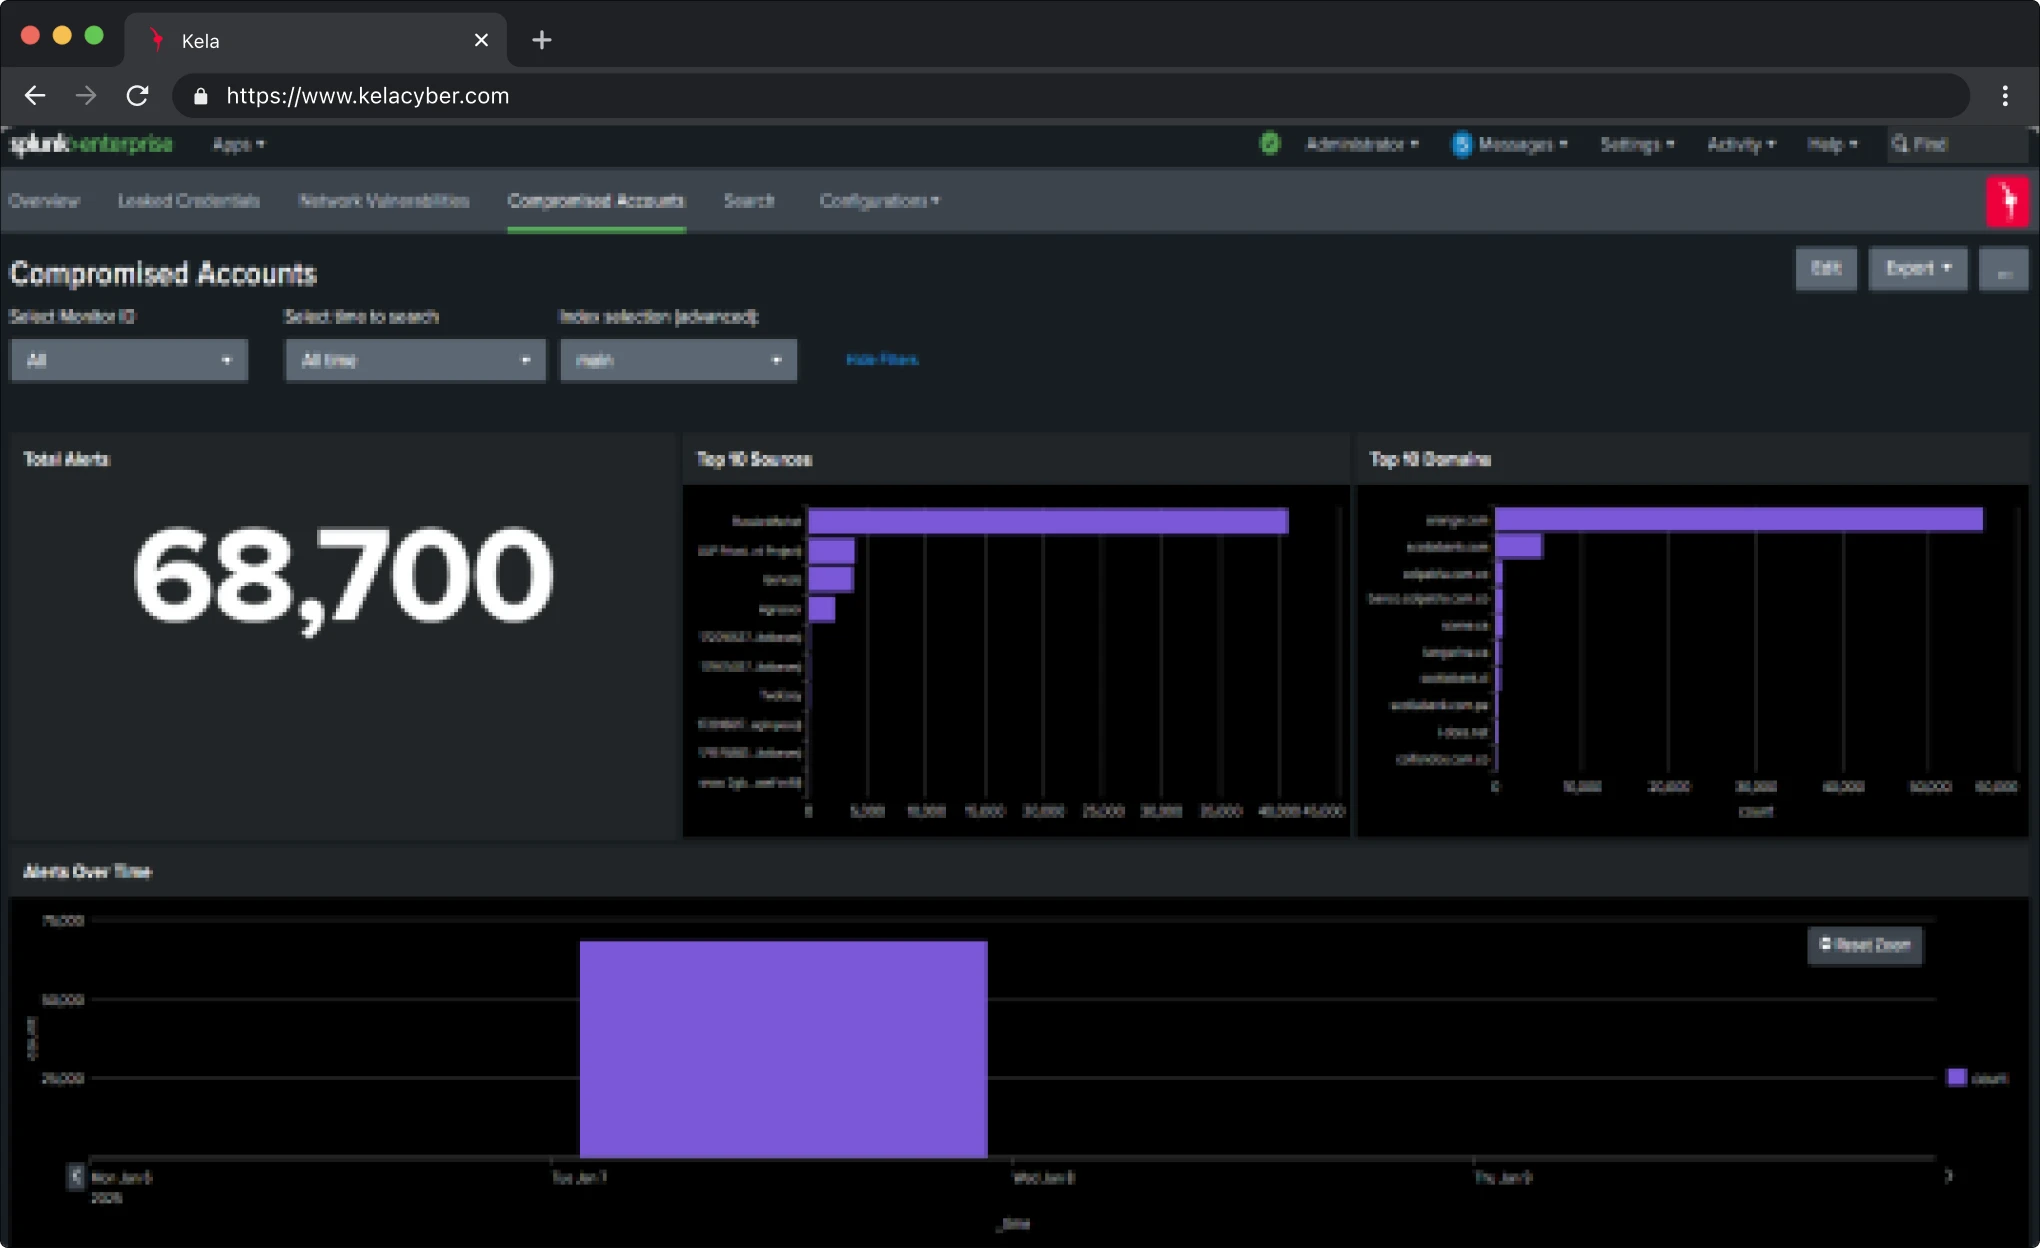
Compromised accounts
Compromised accounts
Aggregated information, as well as a detailed list of all compromised accounts detected with a ranking of severity, users, and – if available – passwords
Leaked credentials
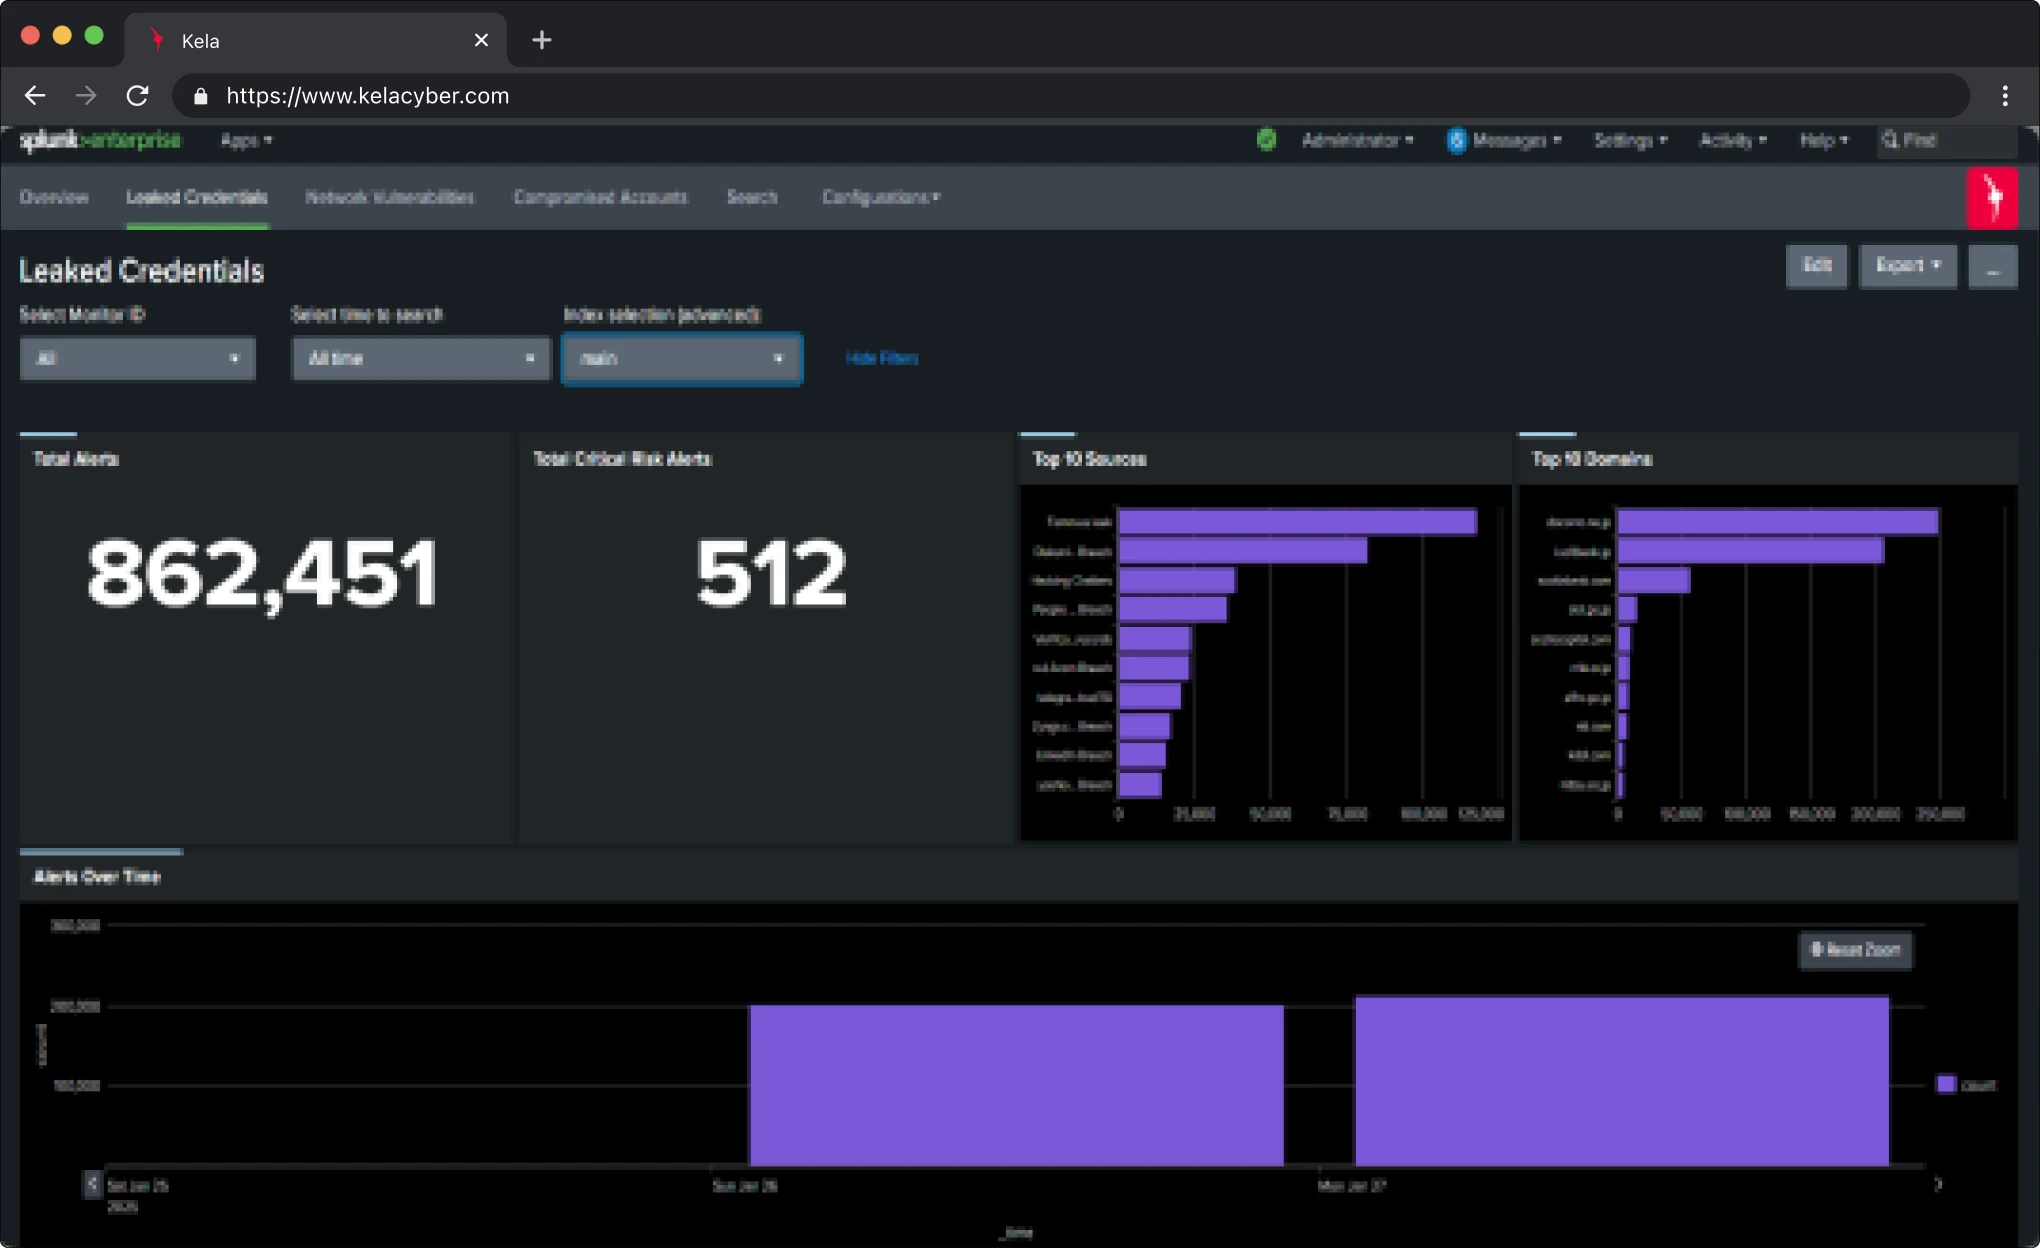
Leaked credentials
Understand historical evidence of credentials leaked to a broader audience to enable corrective measures.
Network vulnerabilities
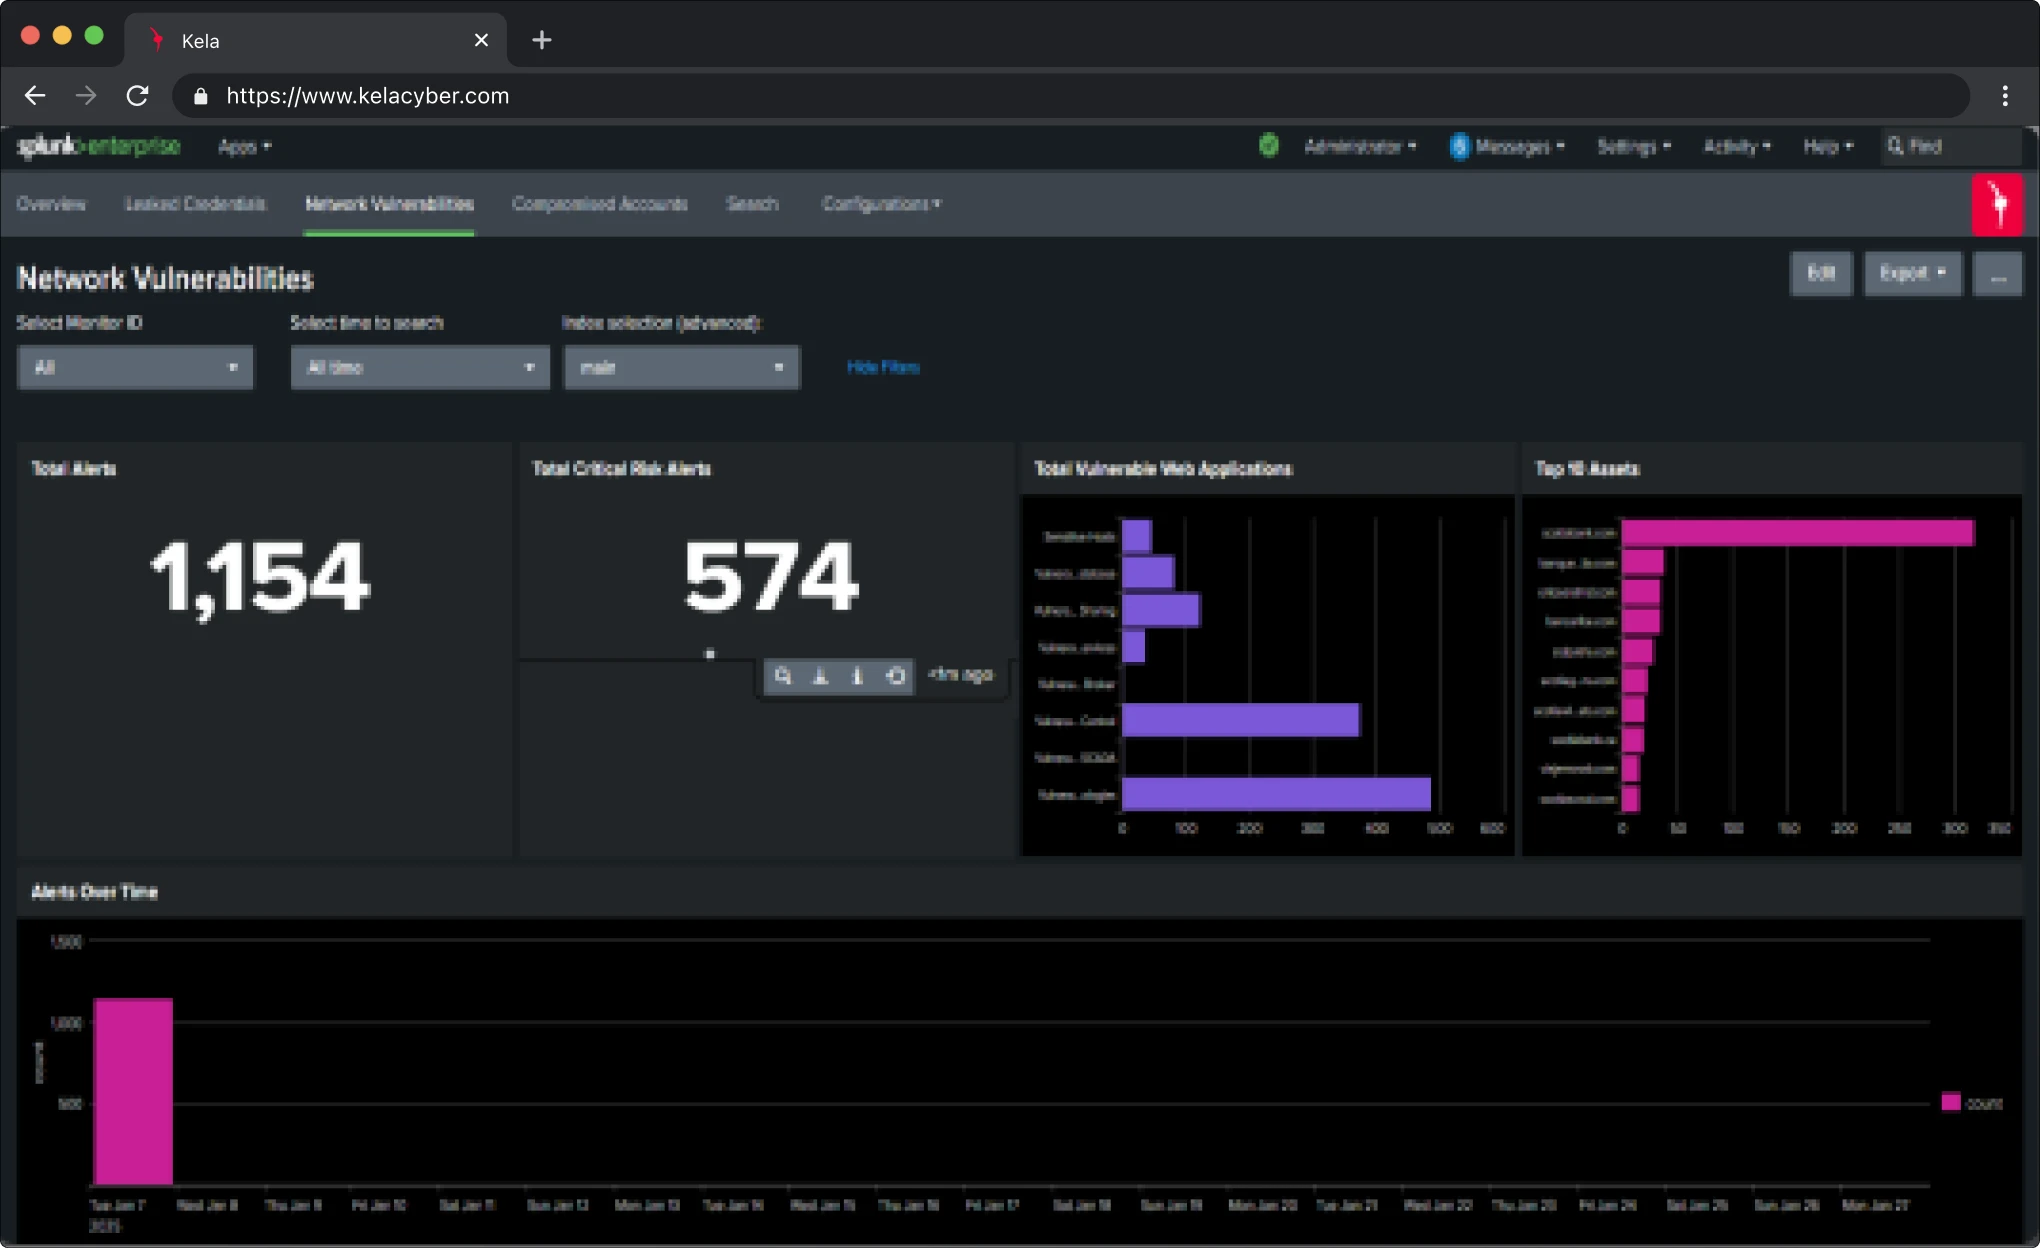
Network vulnerabilities
Identify and detect network devices and specific versions with known vulnerabilities, so you can respond, harden infrastructure, and eliminate vulnerabilities.
Darkweb Insights and
Hacking Discussions
Darkweb Insights and
Hacking Discussions
Visual insights into Hacking Discussions and more
Benefits

Discover and act decisively against real-time risks and vulnerabilities

Investigate IOCs faster with fewer false positives leveraging deep context

Accelerate remediation by pinpointing sources of attacks and vulnerabilities

Instantly identify and monitor compromised credentials, sensitive data, and exposed assets, helping your team protect your employees

Understand when and where data and account leakage has occurred to take corrective and protective action
How KELA Apps Work? Increase Your Effectiveness in Splunk:

Both the IOC and Monitor applications pull information from KELA into your Splunk instance using REST APIs and require a KELA API key for initial setup. This is available from KELA customer support.

Ingested events are stored within Splunk for optimized search performance and align with Splunk’s Common Information Module ensuring seamless data integration across different Splunk apps and tools.
Book a Demo
Prefer to schedule a meeting right now? Click here.


