







Continuous Threat Exposure Management
Reduce your threat exposure with confidence
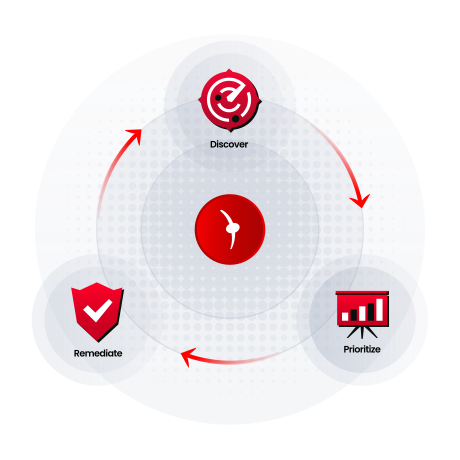
Expose Less, Validate More
ULTRA RED automatically validates every exposure and attack vector through active, external testing. With real-world proof of exploitability in hand, SecOps teams can trust their findings, focus on real risks, and respond with confidence — without second-guessing every alert.

Complete Attack Surface Visibility
Continuously discover and monitor all internet-facing assets leaving no exposure unmanaged.

Exploitability-Driven Prioritization
Focus on the vulnerabilities that are truly exploitable, with evidence accelerated decisions.

Faster, Smarter Remediation
Uncover hidden high-impact risks and use VITA AI guidance to mitigate exposures with confidence

100%
Exposure Validation
<1%
False Positives
-75%
Fewer Alerts
2x-3x
Faster MTTR
100%
Agentless SaaS
Attackers already know where you’re exposed. Do you?
Complete Attack Surface Coverage
ULTRA RED continuously discovers, maps, and monitors internet-facing assets across the external environment. This gives organizations a clear, current view of exposed assets, helping security teams reduce blind spots and maintain stronger control over their attack surface.
Exploitability-Based Risk Prioritization
ULTRA RED validates which vulnerabilities are truly exploitable, helping teams focus on the risks that matter most. Instead of chasing large volumes of alerts and CVEs, organizations can prioritize remediation based on evidence and real-world attacker relevance.
Confident, Accelerated Remediation
ULTRA RED helps uncover hidden and high-impact vulnerabilities that may be missed by traditional testing approaches. With proof of exploitability and practical guidance from VITA AI, ULTRA RED enables teams to remediate faster and act with greater confidence.
Built for Proactive Exposure Management
Capabilities that help organizations identify, validate, and remediate external exposures with greater speed and confidence.
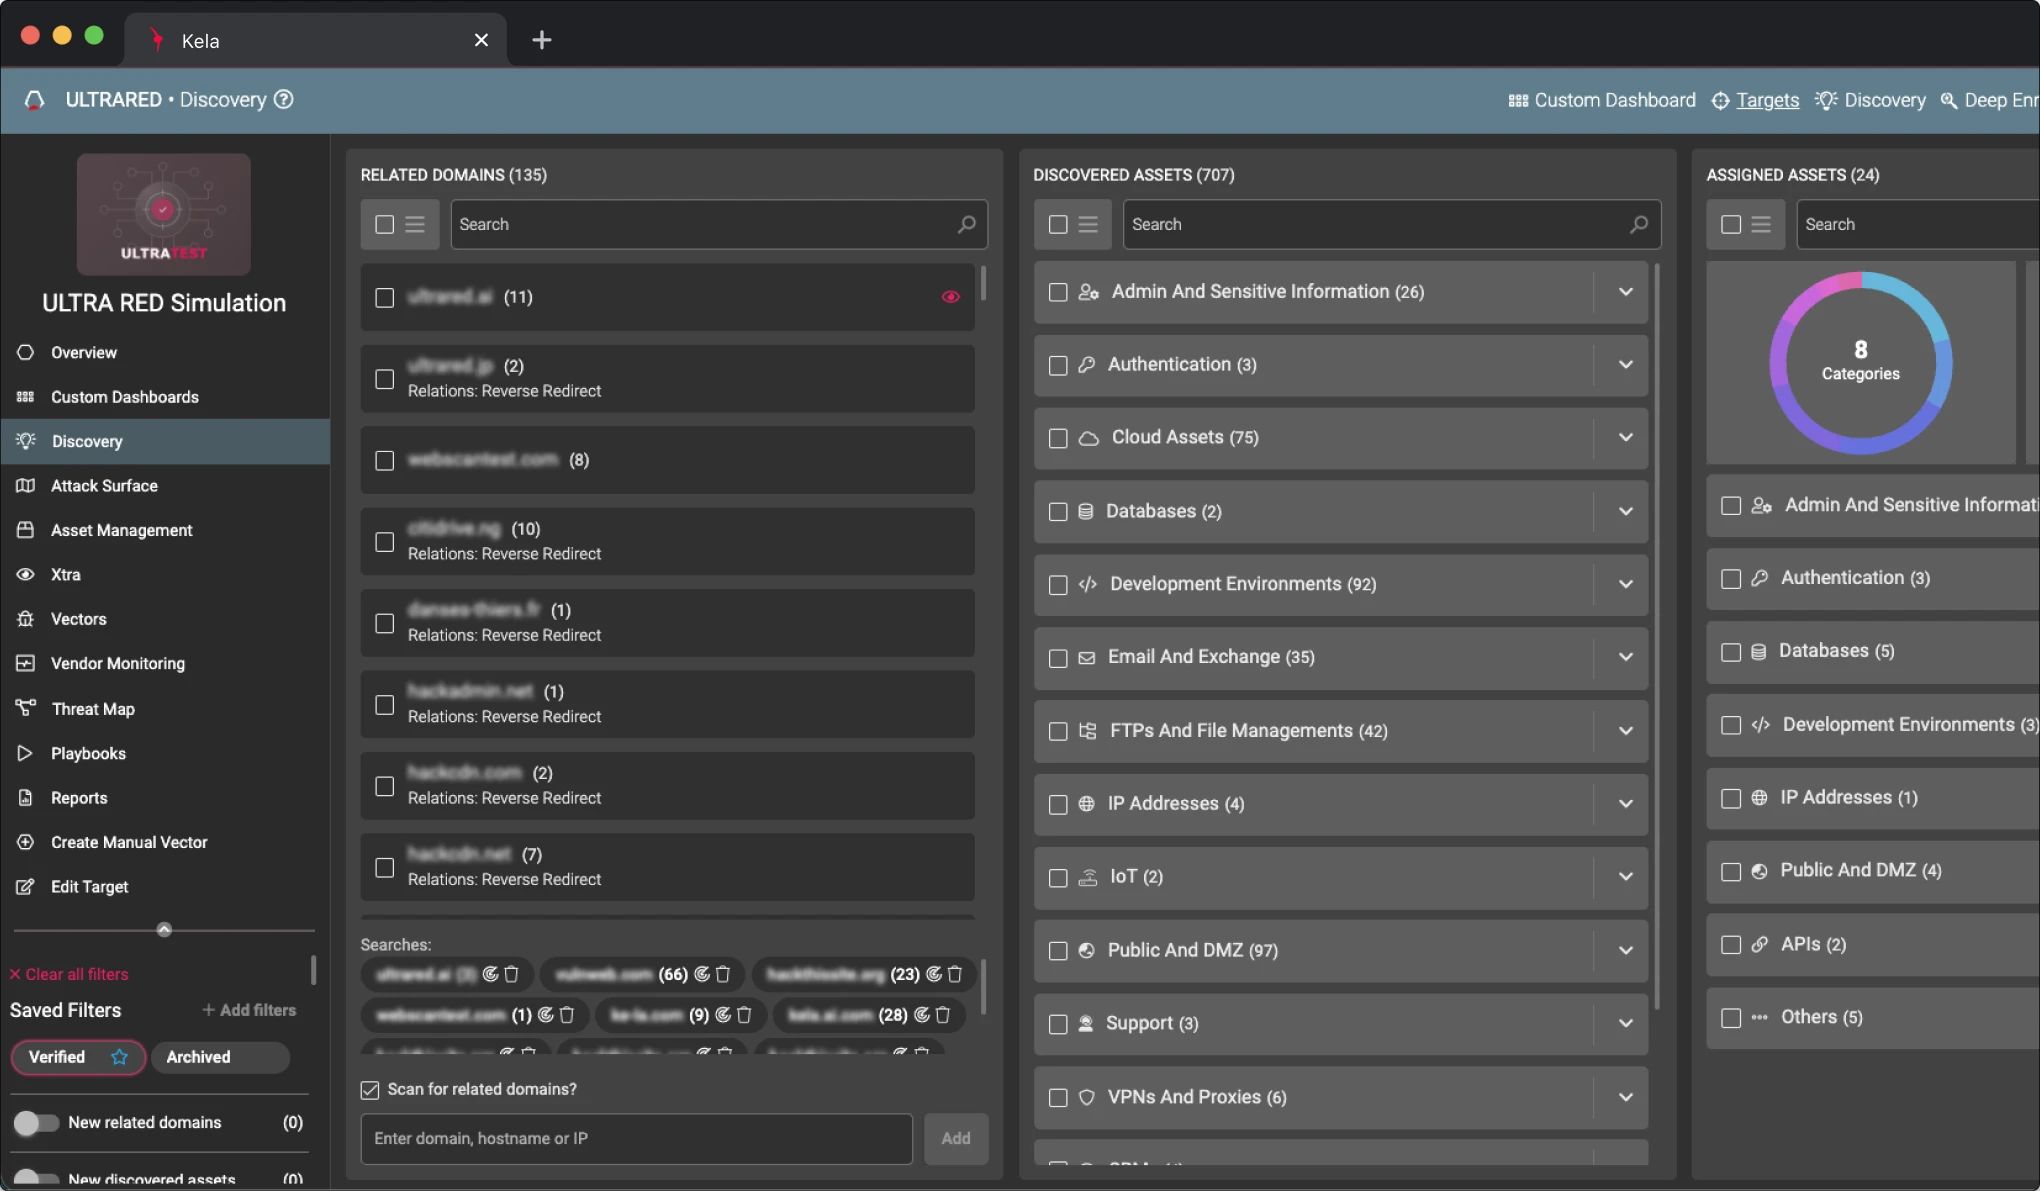
External Attack Surface Discovery
External Attack Surface Discovery
From a single domain, ULTRA RED continuously uncovers everything attackers can see, including acquired infrastructure, shadow IT, and assets no one knew existed. No setup, no configuration required.
Contextual Asset Mapping
Contextual Asset Mapping
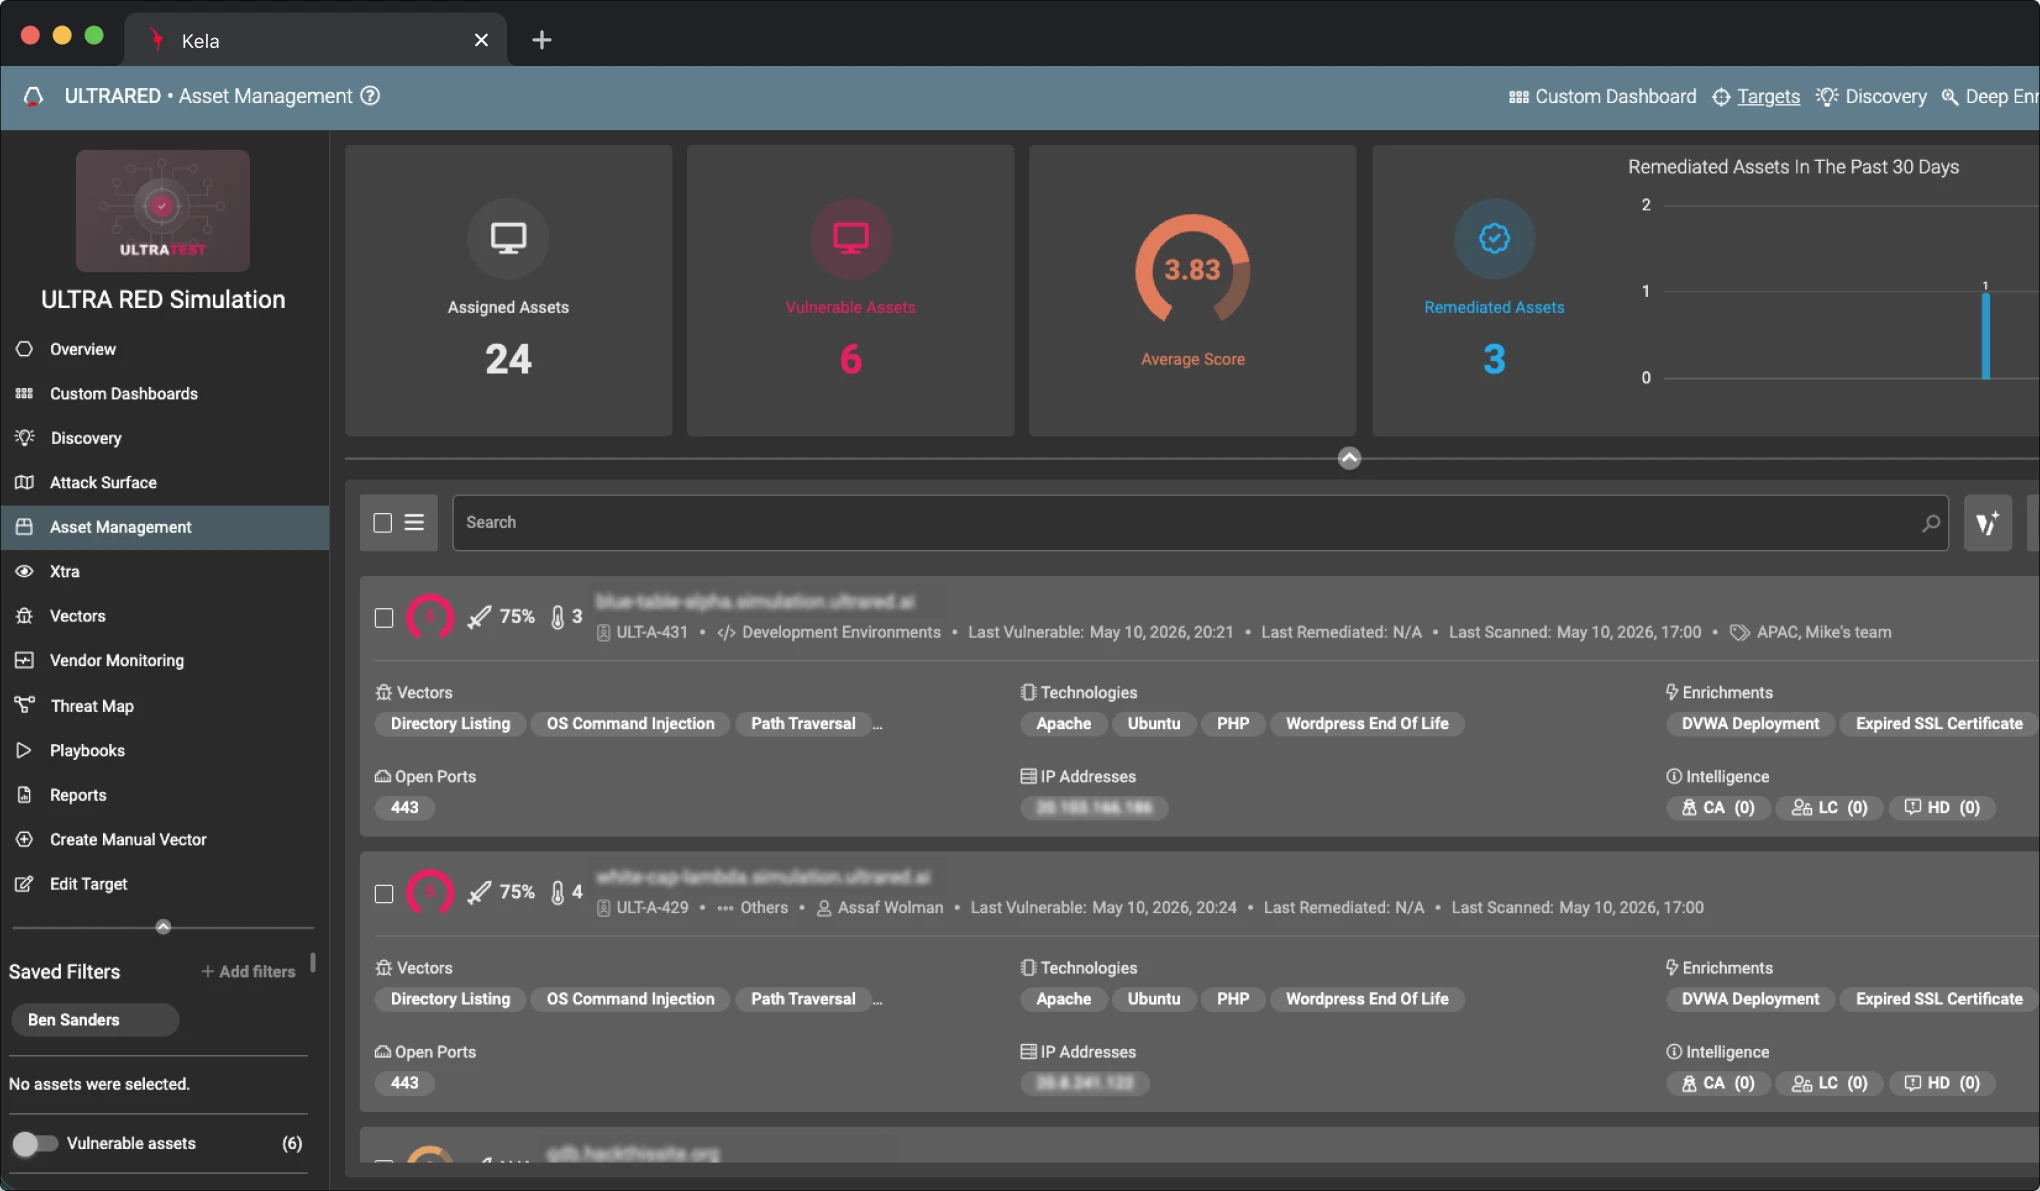
Every asset is analyzed in context to reveal how it can actually be reached — giving you a live view of your true external exposure.
Exploitability-Driven Prioritization
Exploitability-Driven Prioritization
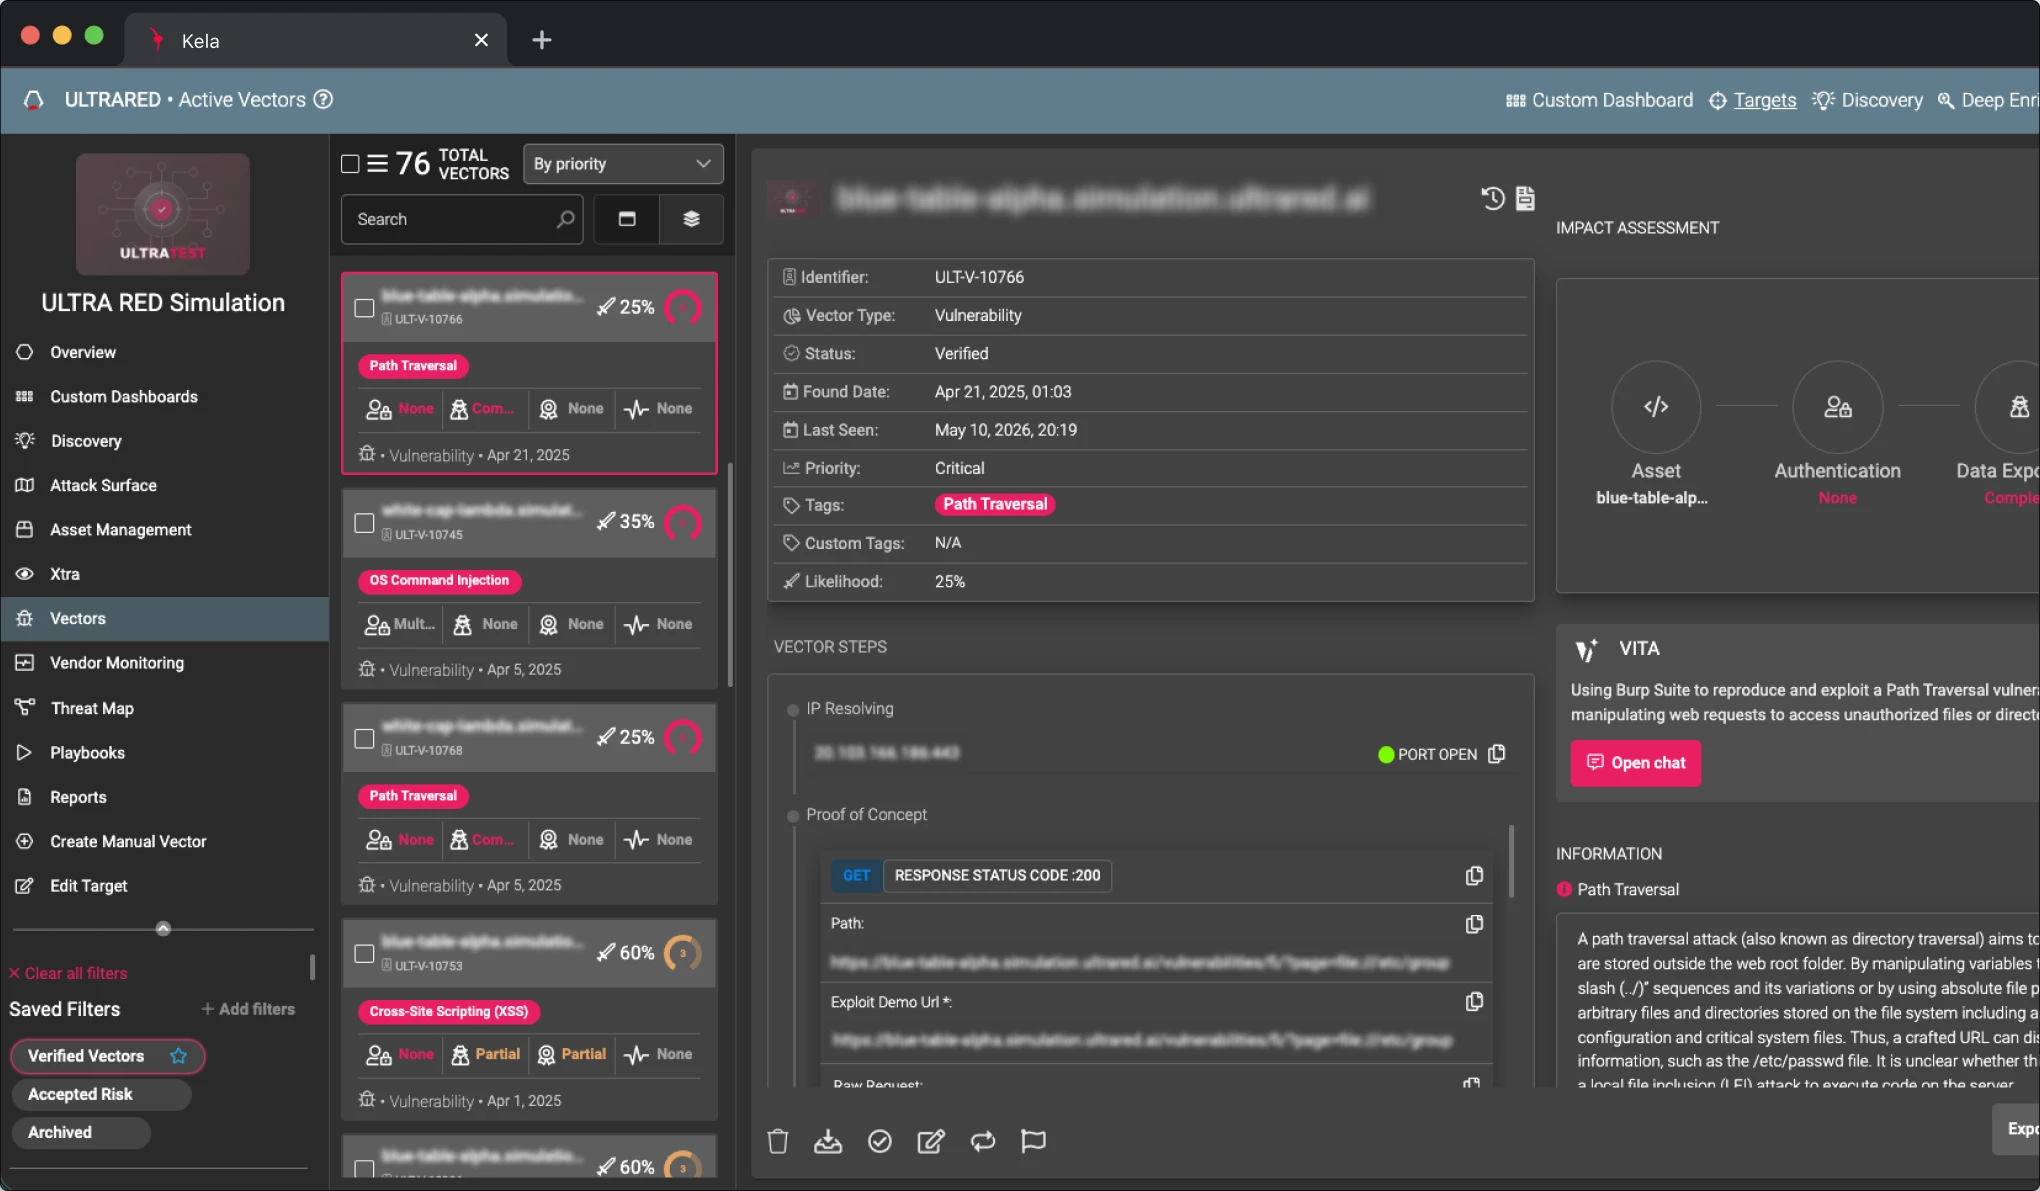
Findings are ranked by real-world risk, combining exploitability, asset criticality, EPSS score, and business impact — so teams focus on what can actually cause damage.
Safe Validation
Safe Validation
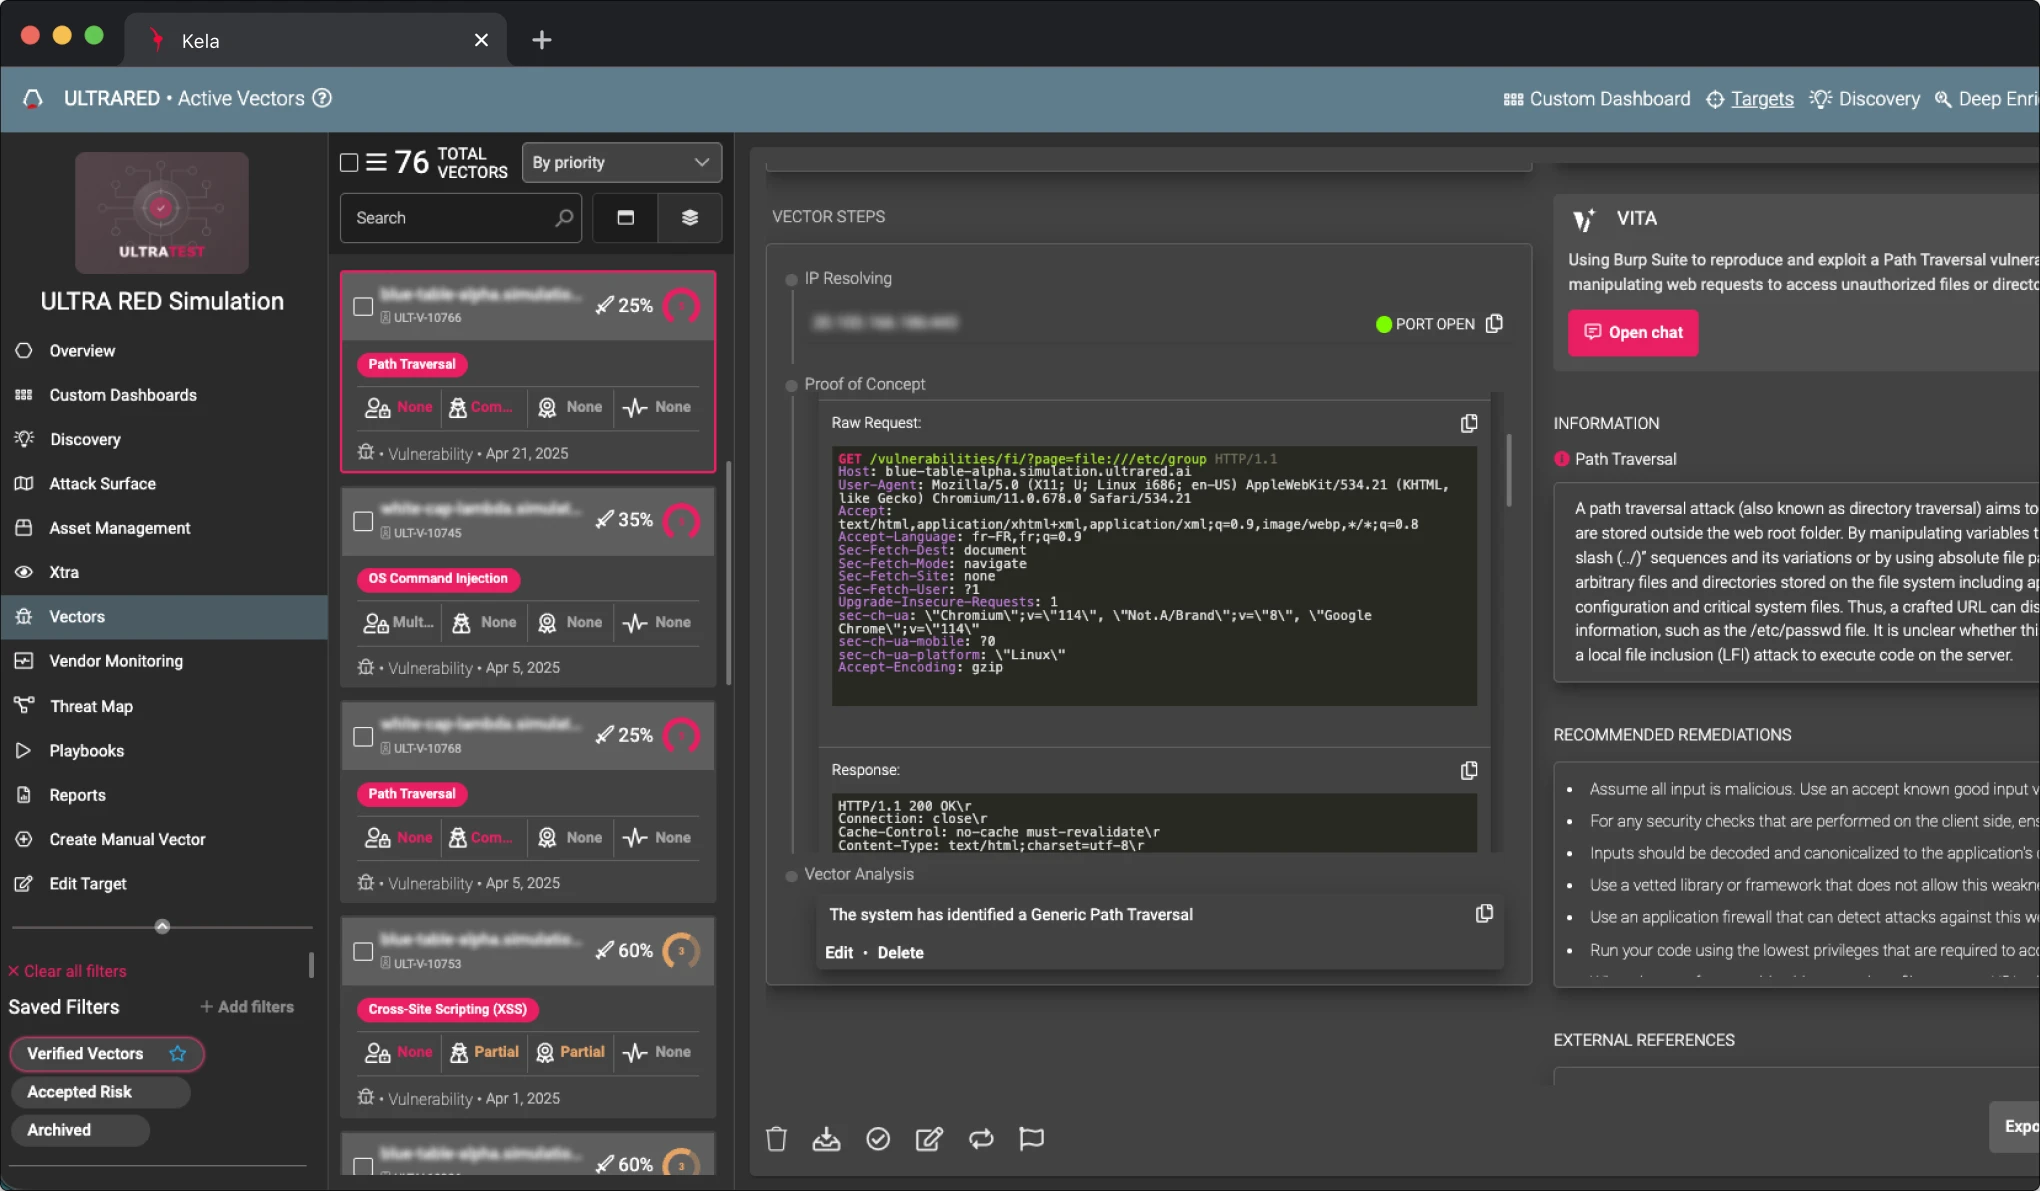
ULTRA RED performs deep, non-intrusive testing to confirm exploitability — delivering verified findings with proof-of-concept and a full evidence chain, without impacting production systems.
Remediation-Ready Findings
Remediation-Ready Findings
Each validated finding arrives as a remediation-ready package — complete with fix guidance, technical context, and evidence — so you can hand it off directly to engineering and resolve it fast.
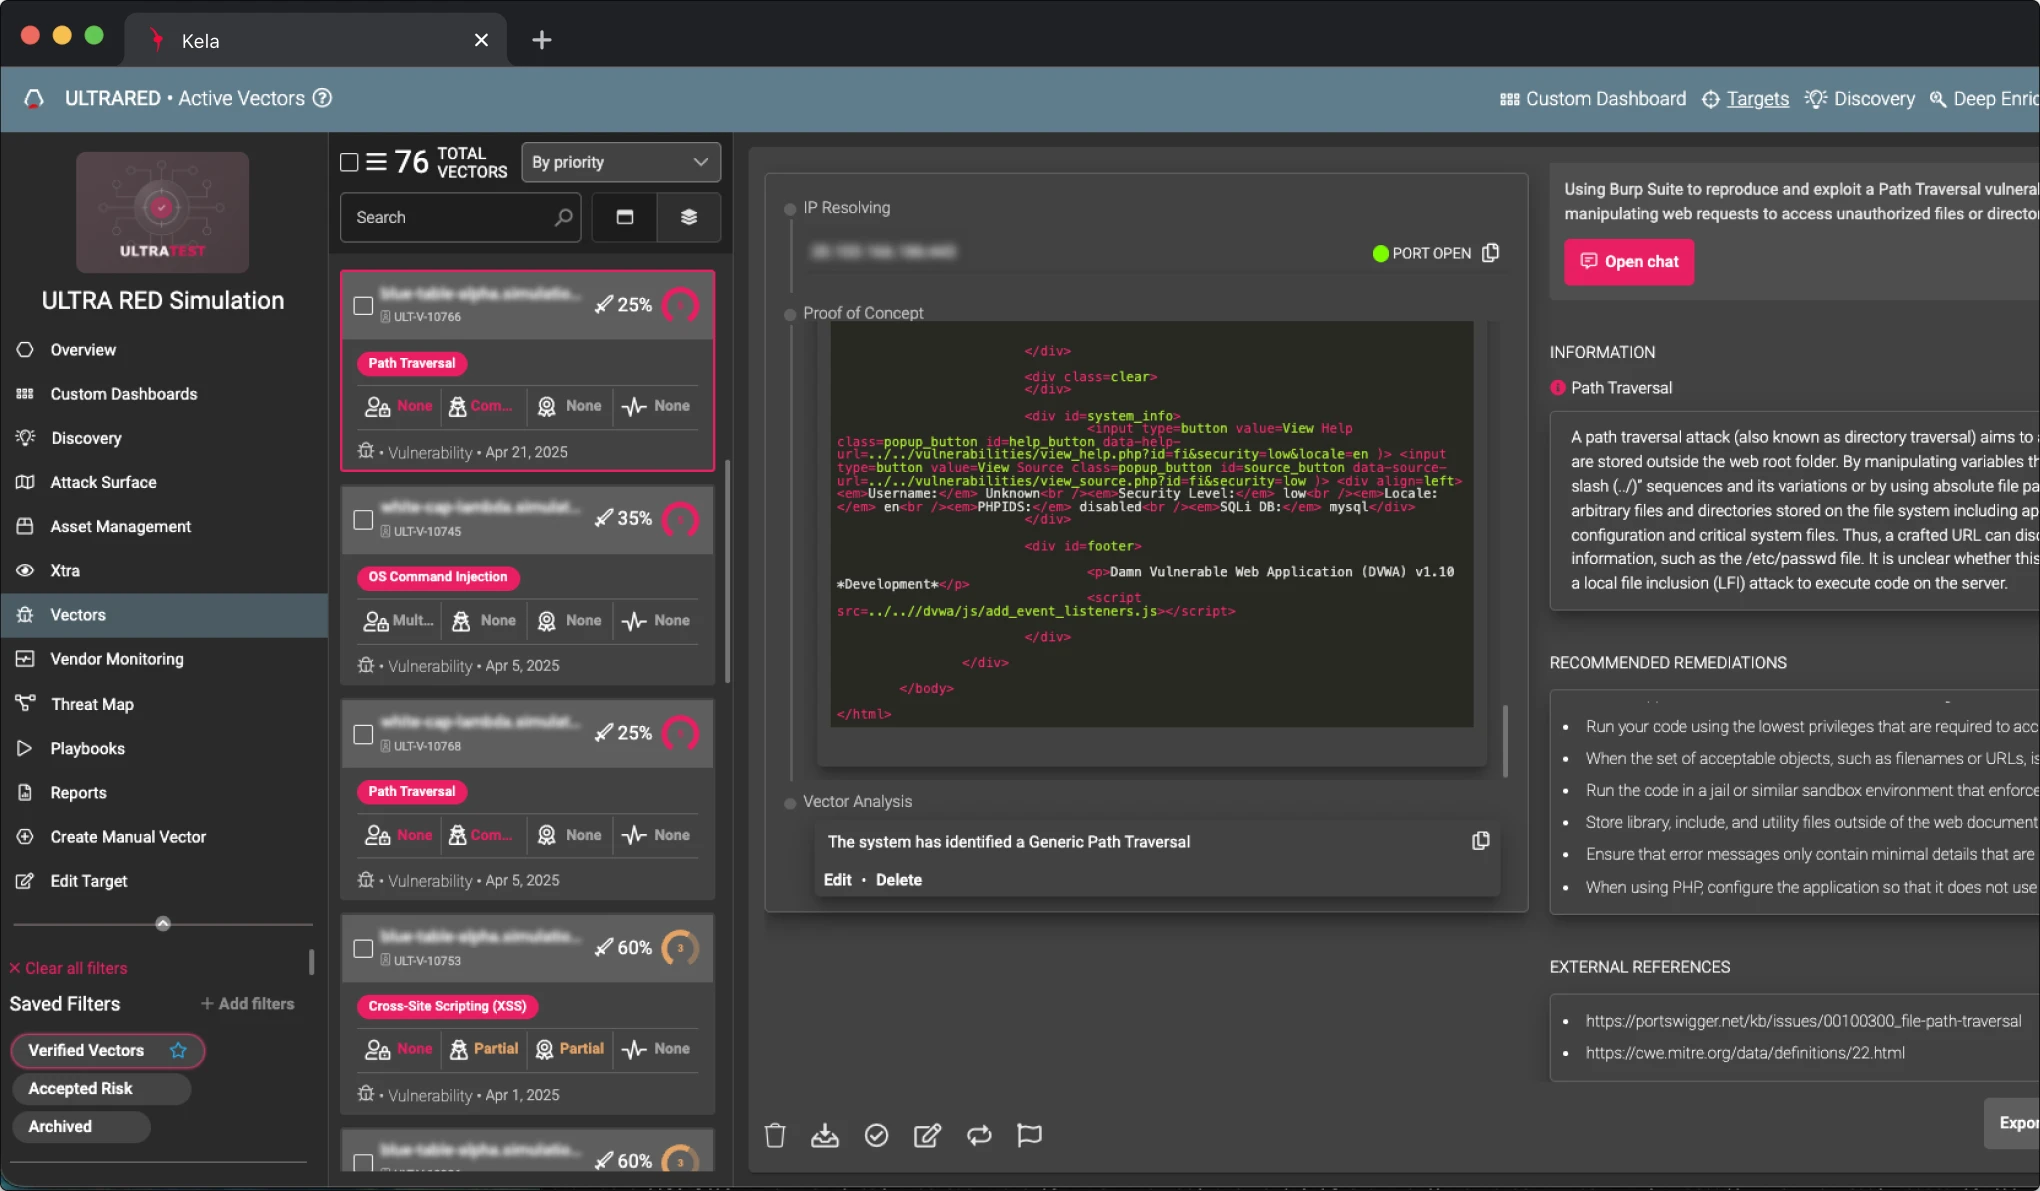
Continuous Attack Surface Monitoring
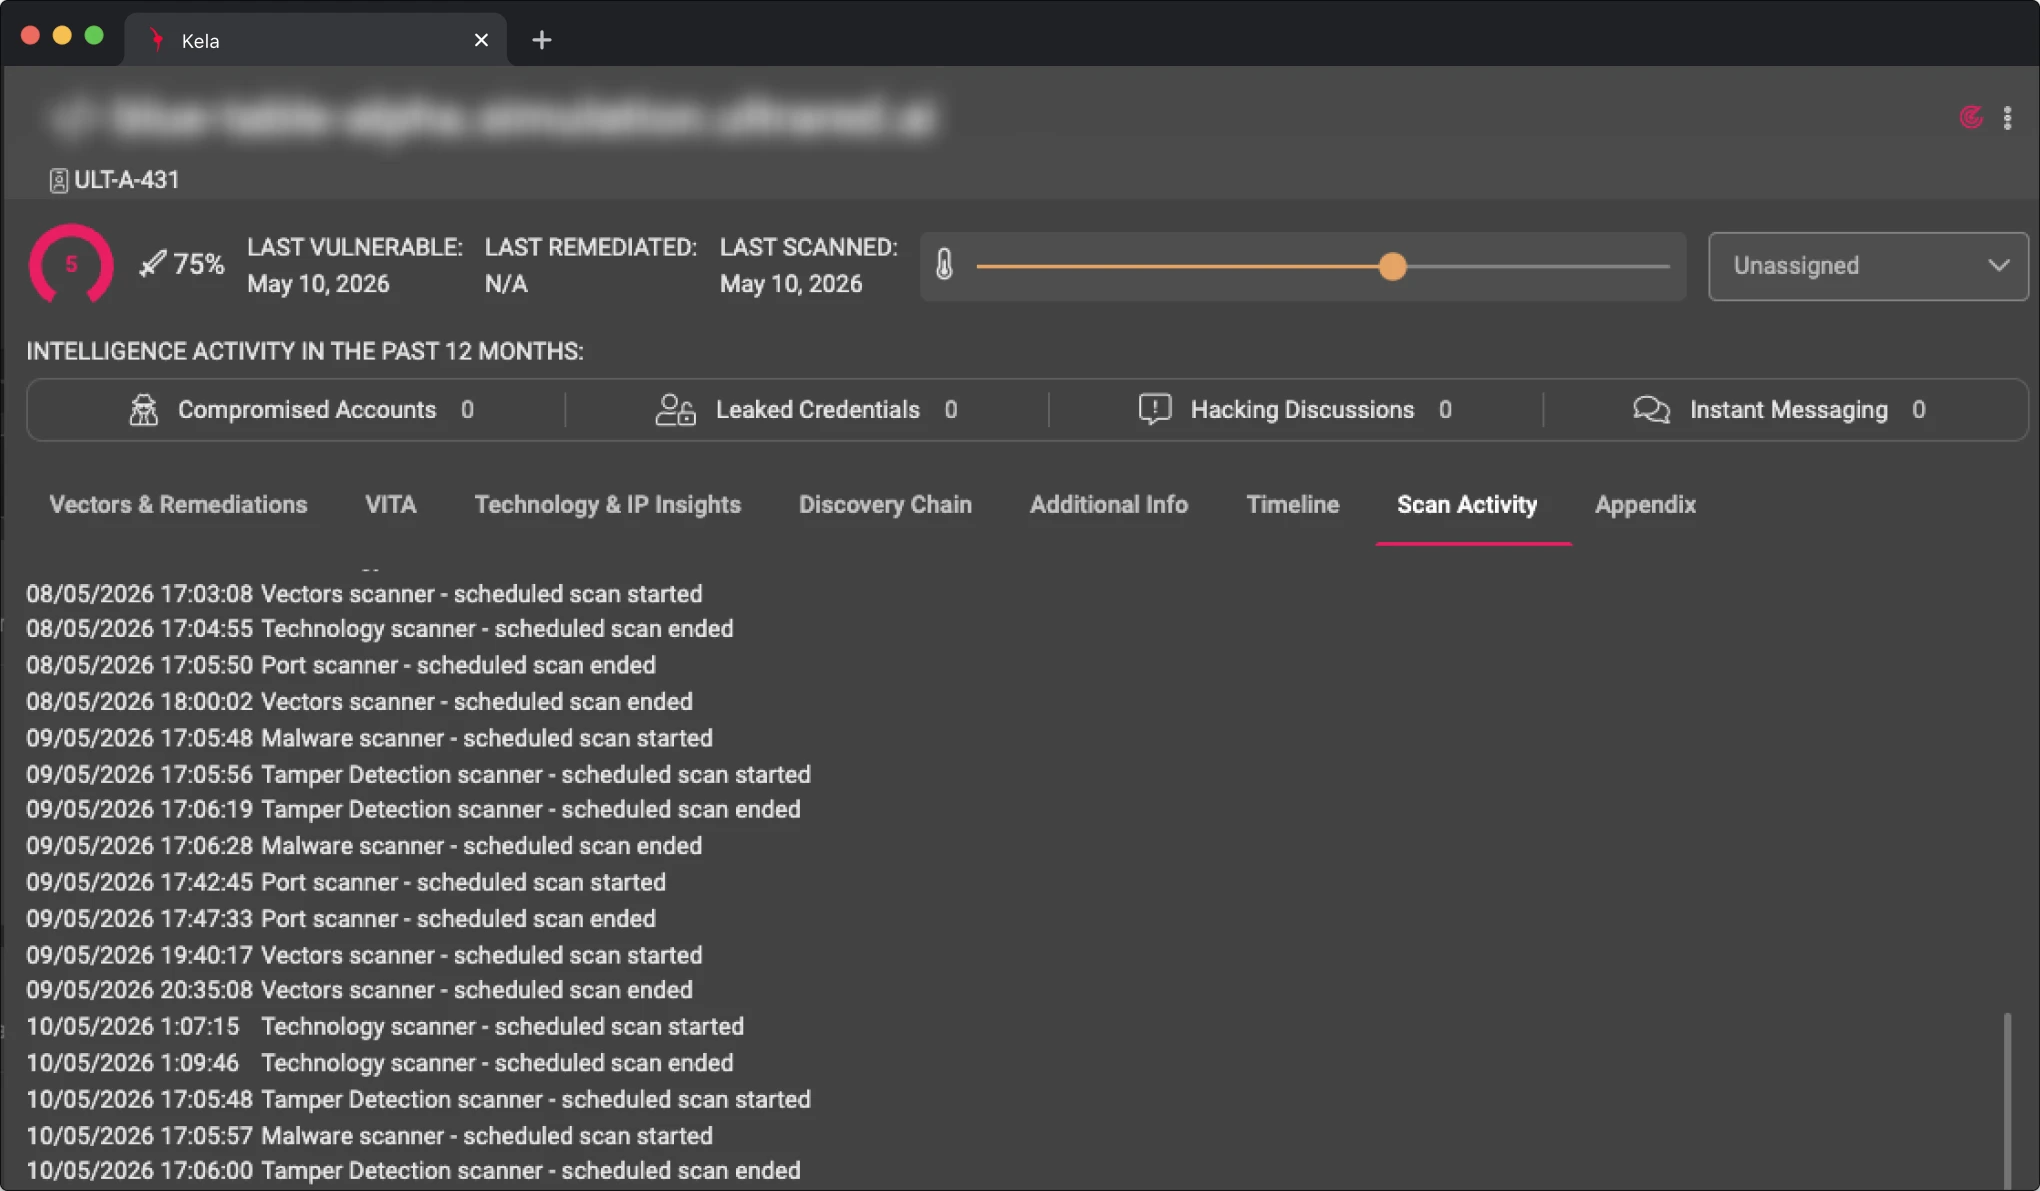
Continuous Attack Surface Monitoring
As new assets and exposures appear, ULTRA RED detects, validates, and surfaces them immediately — keeping your risk posture continuously up to date.
Book a Demo
Prefer to schedule a meeting right now? Click here.
FAQ
What is continuous threat exposure management (CTEM)?
CTEM is a continuous cycle of discovering your external attack surface, validating which exposures an attacker can actually exploit, and fixing those first. ULTRA RED, KELA Group’s exposure management platform, runs that cycle automatically.
How does ULTRA RED validate exposures?
By testing them the way an attacker would: active, safe, external validation of each finding, so you get proof of exploitability rather than a scanner’s guess. Findings that cannot be exploited are deprioritized, which is why the noise drops.
Do we need to install agents or open access?
No. Discovery and validation work from the outside, starting from your domains, with nothing to deploy. Internal changes are limited to remediation.
How does it work together with KELA's threat intelligence?
Exposure findings are enriched with intelligence on which vulnerabilities and services attackers are exploiting now, and with signals that your organization is being targeted, so priority reflects real adversary interest, not only severity scores.
How often is the attack surface re-checked?
Continuously. New assets, certificates, ports and technologies are discovered and validated as they appear, and alerts go out when a critical exposure emerges between reviews.
Which teams use it?
Security operations and vulnerability management teams for prioritization and remediation, CISOs for exposure reporting, and red teams that want validated targets rather than long scan reports.


